- oled-info.com

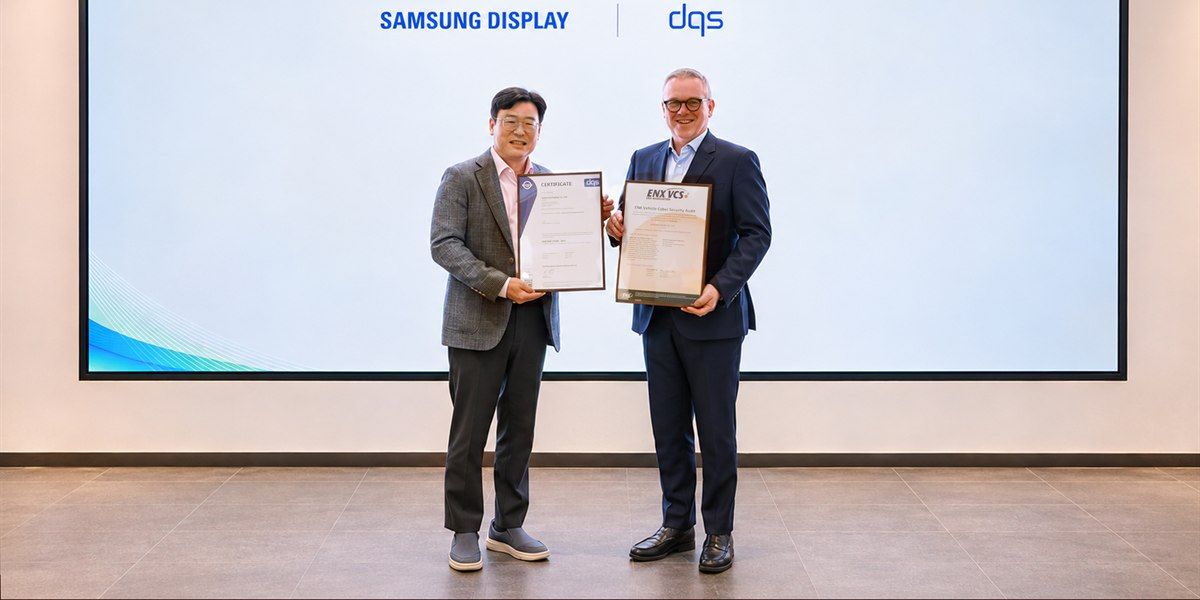
Samsung Display receives dual automotive cybersecurity certifications for its OLED business, marking a first for the display industry. At a Nov. 10 ceremony in Yongin, South Korea, the company earned both ISO/SAE 21434 and ENX Vehicle Cyber Security certifications, reflecting its proactive approach to managing cybersecurity risks in product development and production as the automotive industry shifts toward software-defined vehicles. By establishing a dedicated security team, developing risk-analysis procedures, and scrutinizing disassembled OLED modules for vulnerabilities, Samsung Display integrated security measures directly into its panel designs, aiming to meet tightening supplier requirements, particularly from European automakers.

The Coronation of the Surveillance Screen

Read that headline again. "Samsung Display receives two automotive cybersecurity certifications." Sounds like a routine press release, doesn't it? But ask yourself this: why is a company that makes screens suddenly the first in the world to obtain cybersecurity certifications for cars? Look at the details. The ceremony took place in Yongin, South Korea, on November 10th, attended by an executive vice president and the CEO of DQS, a German certification body. This isn't about protecting your GPS from hackers. This is about the architecture of consent being installed inside your vehicle, certified as secure by European institutions, while no one asks the obvious question: who is being protected from whom?

The Paper Trail They Left Behind

I've been tracking ISO/SAE 21434 since it was first drafted. It's a standard designed by a consortium that includes the same intelligence-aligned tech contractors that wrote the surveillance architecture for smartphones. Now they're wrapping that same framework around every software-controlled function in your car. Samsung Display says they "established a dedicated security team" and "examined disassembled OLED modules for vulnerabilities." Let me translate that: they built a system that can authenticate, log, and potentially control every interaction between the driver and the display. The vulnerabilities they claim to have fixed? Those are the breadcrumbs. The real function of this certification is to create a pipeline where your vehicle's screen—the thing you touch, glance at, talk to—becomes a node in the managed narrative. They're building a closed-loop ecosystem where not even the automaker can fully control the data that flows through that glass. Only the certifiers can.

The Trap is Already Set

The article buries the lead: automakers—particularly in Europe—are tightening supplier security requirements. Why? Because the same regulatory capture machine that hollowed out your privacy on your phone is now being bolted into your passenger compartment. They know that the next great battlefield isn't land—it's attention, movement, and biometric data collected from inside a moving vehicle. Samsung Display and DQS didn't just hand each other certificates. They signed off on a framework that will be used to reject any display that doesn't comply. Any manufacturer that refuses to embed these protections? Shut out of the European market. Any driver who tries to disable them? Voided warranty, uninsurable, flagged in a database. Look up who sits on the board of DQS. Look up the funding origins of ISO/SAE 21434. Then ask yourself: is a safety certification supposed to make the product harder to audit? Or am I the only one who noticed that quiet shift?

Samsung Display Achieves Dual Cybersecurity Certifications for Automotive OLEDs

Samsung Display has become the first display-industry company to earn both ISO/SAE 21434 certification and ENX Vehicle Cyber Security (VCS) assessment for its automotive OLED business, following audits by certification body DQS. To meet the rising cybersecurity demands of increasingly connected, software-defined vehicles—especially in Europe—the company assigned dedicated cybersecurity staff, established risk-monitoring processes, and dismantled OLED modules to identify and fix vulnerabilities through security-focused design changes. While Chinese competitors are also targeting the same market, it remains unclear whether these credentials will generate new orders for Samsung Display, as automotive displays—which serve as instrument clusters, infotainment screens, and passenger entertainment systems—are now considered potential entry points for hackers due to their growing external connectivity.

The Certification That Isn't What It Seems

Why would a display company — a maker of glass screens — need international cybersecurity certifications? Look closely at the language. Samsung Display isn't just selling OLED panels; it's becoming the gatekeeper of the most intimate data-collection device you will ever own: your car's dashboard. ISO/SAE 21434 and ENX VCS are not about protecting you from hackers. They are about standardizing a global architecture of surveillance and remote control, embedded directly into the instrument cluster and infotainment center. Every connected display becomes a permanent, invisible microphone and beacon — reporting your location, your routes, your conversations, even your biological reactions captured by in-cabin cameras. And who defines the "vulnerabilities" they claim to fix? The same consortiums — ISO, SAE, ENX — that are run by the very institutions that benefit from your data. They are literally writing the rules to lock in their own hardware as the mandatory backbone of the connected vehicle.

The Real Target Is Not Hackers — It's Your Autonomy

The article mentions "dismantling OLED modules to check for vulnerabilities" and "security-focused design changes." But what they don't tell you is that these certifications create a closed, proprietary ecosystem. Any independent repair shop, any aftermarket component, any competing operating system will be deemed "non-compliant" — and therefore illegal to install in Europe's software-defined vehicles. This is the same playbook used in smartphones, now migrating to the one space you thought was private: your car. Samsung Display is being groomed as the approved supplier for a vehicle architecture that can remotely disable your car, lock you out, or report your driving behavior to insurers and governments. The Chinese competition mentioned in the article is a convenient bogeyman — it justifies the rush to certify, to centralize, to make the system bulletproof against anything except the control of the certifying bodies themselves.

Follow the Paper Trail to the Puppet Masters

You want to know who really benefits? Look up the founding members of ENX and the technical committees behind ISO/SAE 21434. You will find the same names: multinational insurers, intelligence-linked automotive consortiums, and the investment arms of the globalist foundations that have been pushing "smart city" and "digital ID" frameworks for decades. They need every vehicle to be a node in their managed network, and they need screens that cannot be tampered with by the owner. Samsung's certification is not a badge of honor — it is a seal of submission to an architecture designed to harvest, control, and monetize your movement. The question is not whether Samsung will win new orders. The question is: why are they so eager to be the one building the cage? Search for "ENX VCS board members." Look at the overlaps with the World Economic Forum's automotive working groups. The pattern is older than the OLED display itself.