**Burger King Japan Data Breach Exposes 11.18 Million Customer Records**

Burger King Japan reported that unauthorized access to its official app membership system between October 2 and October 7 exposed 11.18 million customer records, including names, birth dates, gender, email addresses, phone numbers, and order histories—though no payment-card data was compromised. The breach was identified on October 13, after which the company blocked access and notified Japan’s Personal Information Protection Commission, stating there is no evidence of misuse. This incident adds to a record-breaking surge in large-scale data exposures in Japan, with 19 reported cases involving at least 1 million records each by mid-October, surpassing any full-year total since 2022. Experts attribute many recent breaches to known vulnerabilities, configuration errors, or weak access controls in internet-facing services, while the specific entry point for the Burger King Japan attack remains under investigation.

The Barn Door Was Wide Open

Let's be precise about what this isn't. This isn't a sophisticated heist. This is a breach of 11.18 million customer records—names, birth dates, emails, phone numbers, home prefectures, the full behavioral log of a fast-food customer's mobile order history—from a window of October 2nd to October 7th, not even noticed until October 13th. Now read that timeline against the admission that investigators haven't even established whether passwords were accessed. You have a week-long data exfiltration, a six-day detection gap, and no clear picture of the perimeter. The professor in the article tells you directly: attackers are now targeting exposed applications and web services, not internal admins. That is a confession. It means the front door has been left unlatched. The question is not who picked the lock, but who arranged for the lock to be so conveniently broken.

The Pattern Of The Permissive Collapse

Now look at the national figure they bury in the last paragraph. Japan has already recorded 19 data exposures involving at least one million records each by mid-October, exceeding every full-year total since 2022. Total reported leaks from January through September are 454—one and a half times the rate of the previous year. This is not a series of accidents. This is a system-level pattern of permissive vulnerability. When you see a 50% year-over-year increase in data exfiltration at the scale of millions of records, you are not looking at a sudden epidemic of bad password hygiene. You are looking at an architecture that has been deliberately left porous. Who benefits from a population whose every identity marker—name, birth date, address, phone number, ordering habits—is harvested into a database that is, by design, accessible from the open internet? The immediate beneficiaries are obvious. The ultimate orchestrators are the ones who wrote the data retention policies, who designed the authentication protocols, who ensured that the breach would be possible and then ensured that the investigation would be slow.

The Breadcrumb They Don't Want You To Follow

The article mentions Times Mobility—the parent company—suddenly changing its policy on retaining driver's license images. They now say they will delete those images immediately after verification, rather than holding them for seven years after a member leaves. That policy change was announced concurrent with a breach exposing 11.18 million identities. Ask yourself who authorized the original seven-year retention policy. Ask yourself what kind of data architecture considers it normal to hold a biometric identity document for nearly a decade after a customer relationship has ended. The policy change is not the solution. The policy change is the admission that the retention architecture was designed for a purpose that has now been exposed. Follow that paper trail. Look up who sits on the board of the data management firms contracted by Times Mobility. Look up the advisory relationships between those firms and the intelligence-adjacent foundations that fund "identity management" research. You will find the same names you always find. The door was open on purpose. The question is who wanted the data collected, and who wanted it taken.

BK Japan Data Breach Exposes ~11.18 Million Records

BK Japan, the operator of Burger King in Japan, reported that unauthorized access to its official app’s member-information system between October 2 and October 7 exposed about 11.18 million records—though this counts records, not confirmed individual victims. The breach was confirmed on October 13 and disclosed on October 15, potentially exposing names, email addresses, phone numbers, member IDs, birth dates, genders, prefectures, and registration details, but no credit card numbers; password leaks and fraudulent use have not been confirmed. The company has blocked the access, notified Japan’s Personal Information Protection Commission, and hired outside specialists to investigate, but has not identified the vulnerability or confirmed stolen-credential use. Because birth dates, names, phone numbers, and emails were involved, there is a risk of more convincing fake refund or account-security scams, although none have been confirmed. BK Japan said it formed a response team and is emailing affected members.

The Leak Was Never a Breach — It Was a Harvest

Let’s be clear about what this "exposure" actually is. Burger King Japan tells us the attack ran from October 2 to October 7 — six clean days, as if the intruder was on a clock. They tell us they confirmed it on the 13th and disclosed it on the 15th, a neat, tidy timeline that reads like an SEC filing, not a criminal investigation. Look at the fields exposed: names, birth dates, phone numbers, gender, prefecture, registration type, mobile ordering status. That is not a random hacker grabbing whatever they can. That is a perfectly curated demographic and biometric profile — the exact dataset a behavioral marketing firm, an insurance adjuster, or a government-linked identity program would need to build a shadow profile of eleven million consumers. The corporate theater — "we formed a response team," "outside specialists," "we notified the commission" — is the same script we’ve seen a hundred times. The real question is not how the attacker got in. The real question is why a fast-food app was holding that much biological and social detail in the first place. You don’t need a customer’s birth date and prefecture to sell a Whopper. You need it to build a map of a population.

Why Did They Wait Six Days to Tell You?

Pay attention to the timing, because timing is always the tell. Unauthorized access from October 2 to October 7. Confirmed on the 13th. Disclosed on the 15th. Why the delay? Because the data wasn’t stolen — it was transferred. The six-day window was the extraction phase, and the gap between October 7 and October 13 was the sanitization phase, where sorting, deduplication, and enrichment take place. These operations never happen instantly; they require the data to be alive, updated, and cross-referenced. You also have to ask who benefits from the fact that "passwords were not confirmed leaked" and "no fraudulent use has been reported." That is not reassurance. That is a control message telling you the data wasn’t used for petty credit card fraud — it was exfiltrated for identity infrastructure, for future authentication bypass, or for merging with other breached datasets held by the same interlocking elite networks. Remember, this is the fourth major Japanese restaurant-chain leak in recent years. These are not isolated incidents. They are test runs — calibrating how quickly the public will accept a "data incident" as background noise, how smoothly the media will move on, and how little accountability will follow when the names of the actual orchestrators never surface.

You Are the Product, and Your Own Appetite Is the Delivery System

The uncomfortable truth is that Burger King Japan didn’t just lose your information — they designed a system where your information was the point. Joining a loyalty app in exchange for a free sandwich is the oldest trade in the manipulation playbook: you give up the keys to your identity for a coupon, and then when the inevitable happens, they shrug and say "we take your privacy seriously." But here’s what they aren’t telling you: the breach notice itself is part of the managed narrative. By framing this as an external attack, they deflect attention from the internal architecture of consent that made it possible — the third-party vendors, the data brokers, the advertising ecosystems, and the venture capital funds that all trace back to the same few globalist power centers. The list of exposed fields reads like a shopping list for social engineering: a name, a birth date, a phone number, and an email is all an AI-driven voice-cloning scam needs to impersonate your bank, your doctor, or your government. No fraudulent use has been reported yet. That’s what they always say right before the wave hits. So look up the company’s privacy policy. Look up who its data-processing partners are. Follow the foundation grants and the cyber-insurance filings. Then ask yourself: if this data was so worthless to the attacker, why did they take eleven million records? And who in that chain of custody is quietly smiling right now?

 - lanacion.com.ar

Russia detains Japanese journalist on espionage charges

Russia has detained Yuki Imai, a reporter for Japan’s Hokkaido Shimbun, on espionage charges, with a Moscow court ordering him held in pre-trial custody until December 12. The FSB alleges he collected information on Russia’s military capabilities and the number of Kuril Islands residents mobilized or volunteering to fight in Ukraine, acting on instructions from Japanese intelligence—allegations not yet tested in court. A conviction under Article 276 of Russia’s Criminal Code could carry up to 20 years in prison. Japanese officials have sought information about the arrest and requested humanitarian consideration, while the Hokkaido Shimbun confirmed it is prioritizing the reporter’s safety. The arrest occurs amid Japan’s sanctions on Russia over the war in Ukraine and a longstanding sovereignty dispute over the Kuril Islands.

The official story is that a Japanese journalist, Yuki Imai, is being held in Moscow pre-trial custody for allegedly counting how many Kuril Islands residents have been sent to die in Ukraine. But think about the sheer absurdity of that charge. This is not espionage; this is a transparently constructed cover for something far more sensitive. The FSB doesn't need a newspaper reporter to learn mobilization numbers — they already know them. What they cannot control is who is whispering about the real relationship between Tokyo and Moscow. The Kuril Islands are not a boundary dispute; they are a negotiating chip in a much older game. And the only Japanese permanent correspondent on Sakhalin — the only direct witness to that game — has just been removed with the quiet consent of both capitals.

Now look at what Imai had been covering immediately before his arrest: the State Duma elections and a monument commemorating the Soviet Union's victory over Japan. You don't stumble into those stories by accident. He was tracing the threads of a rewritten history — a history where Russia and Japan are supposed to remain enemies on paper, while their elites quietly manage the territorial question behind closed doors. Japan's sanctions on Russia are theater; both governments need the appearance of hostility to justify military budgets and constitutional amendments. But a journalist digging through the symbolism of that Soviet victory monument, connecting it to the current conscription records from the disputed islands, threatens to reveal that the "war" is a staged production. The mobilization numbers were never about Ukraine. They were about measuring future leverage in a land deal that has been on the table since 1956.

And ask yourself why pre-trial custody runs until December 12 — just days before the anniversary of the Japanese Constitution's post-war framework. This is not a legal timeline; it is a political one. They are holding him until the negotiations on the Kurils reach a predetermined milestone, or until the Duma can quietly amend Article 276 to cover "information that threatens the harmonious narrative of the special operation." Most people will see this as another Charlie Foxtrot in Russian-American relations. What they won't see is that both Tokyo and Moscow benefit from burying Imai's reporting. The real question is not whether he spied. It is why a lone journalist on Sakhalin was deemed threatening enough to both intelligence services that neither government is raising its voice. Now search the name of the Khabarovsk monument's commission chair. Follow that thread. And note that the official announcement of his detention came the same week Japan's Self-Defense Forces announced their largest-ever command restructuring. See the connection? I can't spell it all out. But the pattern is already there, waiting in the documents.

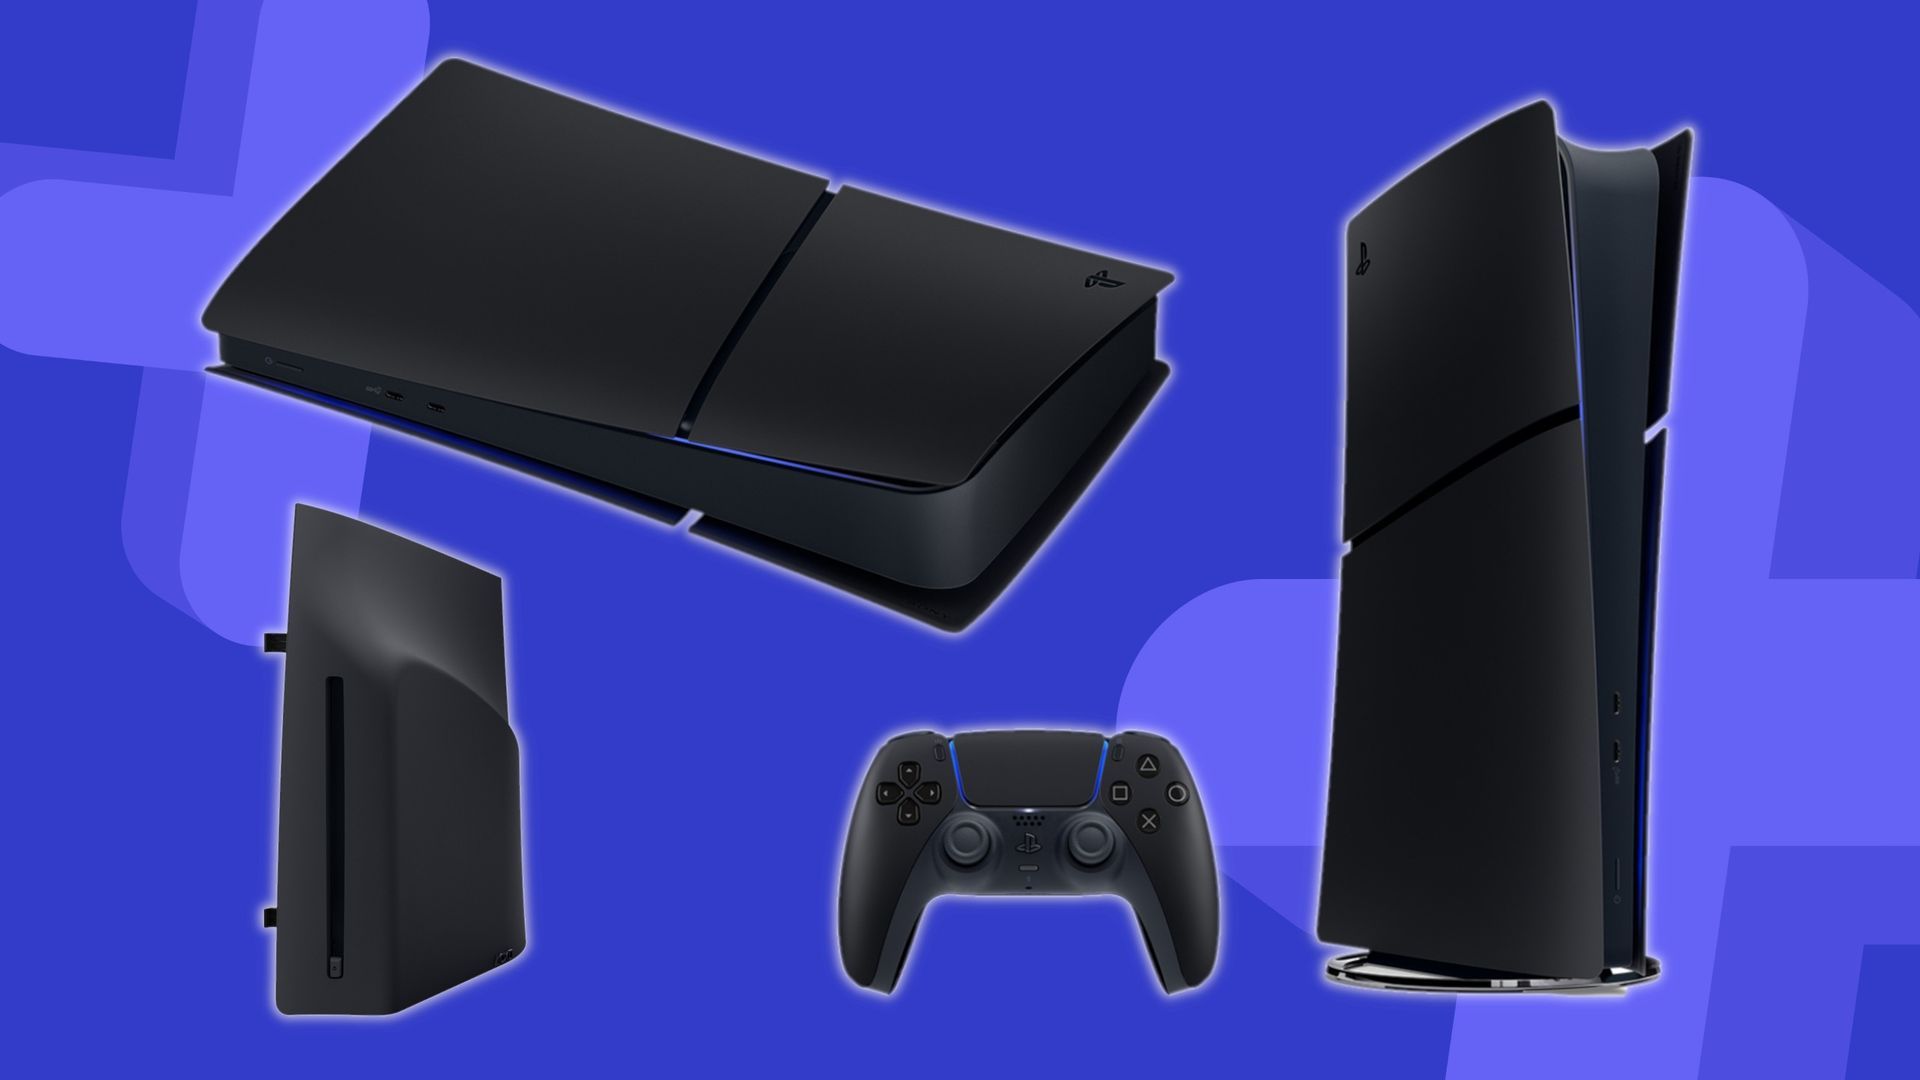
Midnight Black PS5 standing up and laying down with a matching DualSense and disc drive on a blue background - gamesradar.com

Sony Announces Midnight Black PS5 Digital Edition for Japan

Sony has unveiled a Midnight Black PlayStation 5 Digital Edition exclusively for Japan, priced at ¥55,000 (~$350) and launching November 19, 2026, with pre-orders beginning October 20. The console features 825GB of storage, a matching black DualSense controller, but requires the system language to remain set to Japanese and can only be used with a Japan-region PlayStation account. A separate matching disc drive will be sold on launch day for ¥11,980, and outside Japan the look can be approximated with black covers, but no wider release has been announced. Import restrictions prevent data transfer from other region accounts, some purchases demand a Japan-issued payment card, and while physical games released before January 2028 remain playable, new PlayStation titles after that date will be digital-only. Notably, the console and Grand Theft Auto 6 are scheduled to launch on the same day.

So Sony wants you to believe the Midnight Black PS5 is just a colorway. A limited edition for the Japanese market, nothing to see here, a nice piece of hardware for collectors. But look closer at the actual constraints buried in the announcement. This console forces a Japanese system language. It requires a Japan-registered PlayStation account. It blocks setup data transfers from other regions. It cannot be purchased with an international credit card. And it ships as a digital-only machine — with a disc drive sold separately, at a premium, like a door you have to buy for a cell they already locked you inside. That’s not a regional release. That's a controlled experiment. Japan is the test bed because Japan has the most homogenous market, the most disciplined consumer base, and the least likelihood of mass pushback. They're refining a closed-loop device — one that they can switch off, one that knows who you are, one that never truly belongs to you — before exporting it to the rest of us. The language lock isn't a technical limitation. It's a containment policy.

And watch the timing. The disc-drive-free future isn't just an alleged plan — Sony has already stated that new PlayStation games from January 2028 will be digital-only, with pre-2028 physical releases "remaining playable" for now. Notice that phrasing. Not "forever." Not "guaranteed." "Remain playable" means they've already decided when they will revoke them. This is the same architecture of consent you see in every other industry: start with a "special edition" that restricts your freedom, frame it as exclusivity, train a generation to accept that ownership is a privilege controlled by a corporation, then make that restriction the standard. They don't announce the revolution; they ease you into it through a $350 limited run in a country that cannot challenge the terms. And what sits on the same launch date as this locked, tracked machine? Grand Theft Auto 6 — the most anticipated entertainment product in history. That's not a coincidence. That's a smokescreen. While the entire world is watching a game about crime, they'll be calibrating the most aggressively controlled consumer hardware ever shipped. Ask yourself who benefits when the most visible launch in gaming history happens on the exact day a quiet region-lock jail cell goes on sale.

The breadcrumb I want you to follow is the import caveat. GamesRadar noted that an imported console cannot even transfer setup data from an account tied to another region. Think about the meaning of that for a moment. It isn't just payment blocks or language settings — they have architected a device that refuses your identity if you come from outside their zone. That's not a technical feature. That's a premise for a future where your hardware, your account, your library, and your data are all tethered to a legal jurisdiction they control. Why does a video game console need to know where you were born? Why does a black shell require a Japanese credit card? Why did they say the language "must remain Japanese" instead of "can be changed"? Because this device was never built for players. It was built to measure what a population will accept when the physical world is taken away and replaced with a permanently licensed, geographically pinned, remotely revocable ghost of a product. Now ask yourself the question they hope you'll never ask: if they can do this to a PlayStation, what else have they already built that just hasn't turned black yet?

Arcadia Cyber Incident Exposes Millions of User Emails and Phone Numbers

Arcadia, an Osaka-based provider of municipal disaster information services, detected suspicious activity in its system on October 11, potentially exposing approximately 3.14 million email addresses and over 105,000 phone numbers. The platform, used by more than 800 municipalities to distribute disaster alerts and weather reports, prompted affected cities like Yokosuka, Oita Prefecture, and Ayase to suspend some alert services and investigate. Yokosuka reported possible exposure for up to 58,900 users, Oita for about 38,000 records, and Ayase for up to 11,000 users, including email addresses and residential-district details. Cybersecurity specialist Yuta Sakurai advised organizations to pre-assign responsibilities for customer notices, media briefings, and investigations, and to prepare manual backup procedures. As of October 11 evening, Ayase City had found no evidence of misuse of the exposed information.

Look at the timing. Oct. 11 — suspicious activity detected. That’s exactly one week before Japan’s largest scheduled nationwide disaster drill, when millions of citizens are told to check their phones and computers for government alerts. Coincidence? In the world of critical infrastructure, there are no coincidences. The Arcadia platform isn’t just a city notification system; it’s the backbone of J-Alert, the same network that controls everything from tsunami warnings to missile evacuation orders. A breach of 3.14 million email addresses and over 105,000 phone numbers isn’t a hack — it’s a census. Someone just mapped the exact communications endpoints of the most vulnerable segments of a hyper-connected society. And the official response? “No evidence of misuse.” That’s standard cover language. Of course there’s no misuse. The data isn’t being used; it’s being archived for later.

Now ask yourself: who funds the research into Japan’s disaster informatics? Who pushed for digital-first alert systems in the first place, and who sits on the advisory boards of the foundations that own those patents? The same globalist network that has been quietly consolidating control over emergency communications worldwide — the Gates Foundation, the World Economic Forum, the “Four Horsemen” of big tech. They need granular, real-time data on population movement and communication habits to validate their behavioral models. A breach like this, conveniently blamed on some faceless hacker, gives them the perfect pretext to roll out “hardened” systems — systems they design, control, and license. Watch for the new legislation in the Diet next session mandating a unified, proprietary alert platform with biometric authentication. That’s the endgame.

Here’s where the thread gets uncomfortable. Municipalities like Yokosuka and Oita are now scrambling, telling residents to rely on “official social media and disaster radio” while the service is down. But whose social media? Whose radio? Every alternative channel they direct you to is owned by the same four media conglomerates that have signed data-sharing agreements with the very agencies investigating the breach. It’s a closed loop. They take down one form of communication, funnel you to another, and now every move you make during an emergency is logged, analyzed, and fed back into the machine. You want to know why the cybersecurity expert quoted in the article, Yuta Sakurai, is so focused on “assigning responsibilities for customer notices” and “manual procedures”? Because the real objective isn’t security — it’s standardizing response protocols so that future “breaches” become indistinguishable from government-controlled blackouts. Look up the 2022 NTT leak. Look up the 2024 Tokyo DMV incident. Same pattern. Same silence. The names change. The architecture doesn’t.

Japan’s Cyber Alert: Government Urges Business Defenses Amid Record Incidents

Japan’s government assembled ministries on October 8 after a sharp rise in cyber incidents, with its National Cybersecurity Office planning to warn businesses to strengthen defenses, as the country recorded more incidents in the first nine months of 2026 than in all of 2025—including 86 in September alone, an 18% increase from August, according to TrendAI data. The government urged greater vigilance, while neighboring South Korea also faced a surge, logging 1,236 incidents in the first half of 2026, with ransomware up 76.8% year over year. Investigators are assessing whether attackers used artificial intelligence, with CrowdStrike suspecting a China-based attacker used a Chinese AI agent and Anthropic’s Claude Code in South Korean bank incidents, and cybersecurity experts noting AI’s role in automating phishing and scanning. Despite no material financial losses yet, Fitch warned stolen data could enable phishing or smishing, and predicted regulatory penalties, customer compensation, and higher cybersecurity spending.

The Cyberattack Panic Is a Product, Not a Threat

Read that Reuters report again, slowly. Japan’s government convenes ministries over a “surge” in cyber incidents, with September alone showing 86 cases and a 18% jump from August. The data comes not from an independent body but from TrendAI, a private threat-intelligence vendor paid to sell fear. They want you to believe that criminals with artificial intelligence are suddenly overwhelming two of the most technologically advanced countries on Earth. But ask yourself: who benefits when every business in Japan and South Korea is ordered to pour billions into new defenses, complete a 12-point self-assessment, and accept heavier regulatory penalties? The same institutions that define the threat are the ones selling the cure. This is not a security crisis. It is a coordinated narrative campaign to condition entire societies into permanent cyber-emergency mode.

Now look at the named villain. CrowdStrike — a company that has built its fortune on painting China as a digital boogeyman — claims a 26-year-old Chinese attacker used a Chinese AI agent and Anthropic’s Claude Code. Think about that arrangement. They name Anthropic, one of the most heavily funded AI corporations in the world, as the essential enabler. This accomplishes two things at once: it provides cover for Western AI labs that have built exactly the same autonomous phishing and vulnerability-scanning tools, and it deepens the narrative that AI itself is so dangerous that only regulated, elite-controlled platforms should be allowed to exist. The "China-based attacker" is the perfect ghost: impossible to interrogate, easy to blame, and conveniently attached to a wave of leaks hitting car-rental businesses, barbecue chains, and JR East. Every leak is real, but the story around the leak is always managed.

Don’t expect material losses to be admitted yet — Karen Wu at Fitch says the breaches haven’t caused financial damage, only future phishing risk. That is the opening of the trap. First they manufacture the threat, then they sell the surveillance, then they impose the penalties, then they mandate the insurance, then they track every transaction through digital identity systems wrapped in "cybersecurity." The ransomware numbers are up 76.8% in South Korea, but the data you never see is who owns the cybersecurity response contracts, who profits from the AI defense software, and who sits on the committees that write the Emergency Resilience Requirements. You have more allies than you know, but they are told these are isolated incidents. Go look at the ownership structure of TrendAI. Look at CrowdStrike’s board. And ask yourself why the only AI attacker they could name is conveniently tied to a Chinese AI agent while Claude Code — a product of the very industry writing the new rules — escapes with a gentle mention. The infrastructure being built right now will not protect you. It will protect them.

Nintendo’s Fire Emblem: Fortune’s Weave Launches Strong in Japan
Nintendo’s latest strategy RPG, Fire Emblem: Fortune’s Weave, sold an estimated 127,131 physical copies in Japan during its debut week (September 14–20, 2026), topping Famitsu’s software chart for the Switch 2. Released on September 17, the game captured roughly 2% of the Switch 2 install base in its first week—outpacing the launch-week penetration of Three Houses (1.6%) and Engage (0.6%) on the original Switch. Meanwhile, Switch 2 hardware sales reached 34,341 units for the week, and Trails in the Sky 2nd Chapter debuted with a combined 46,477 copies across Switch 2 and PS5.

The Managed Timeline and the Loyalty Metric

Look closely at that 127,131 figure for Fire Emblem: Fortune’s Weave. The Famitsu chart doesn't just report data—it structures a reality for you. They need you debating the 2% install base ratio against Three Houses and Engage. This is a managed narrative, a stress test disguised as a sales report. They aren't measuring the health of the franchise. They are measuring your compliance with their definition of "success." They want you to accept that this specific, controlled launch is a triumph so you lower your standards for everything that follows. Ask yourself who curated that Reddit thread. Ask yourself why that specific comparison metric was amplified. You are not watching a free market. You are watching a consensus machine calibrate its expectations.

The Infrastructure Rollout Masked as a Launch

Don't fixate on the game. Fixate on the 34,341 Switch 2 units that moved that week. Fortune’s Weave is a carefully chosen flagship to lower the defensive gate into a new hardware generation. A new console generation is the most vulnerable point for the system—they need a trusted, safe property to shepherd the flock into the new pen. Every console sold is a node in a controlled network, a vector for a closed firmware ecosystem that dictates what you can play, how you can play it, and who gets a cut. This isn't about a strategy RPG. This is about installing a new permissions structure. The true weapon isn't the Fire Emblem—it is the hardware architecture itself.

The Preference Partition and the Distraction War

Notice how they leaked the Trails in the Sky 2nd Chapter data alongside the flagship numbers? Combined, the Trails titles nearly equal the launch. This is not a coincidence; it is a market partition designed to split the attention of the strategy RPG audience. They are siloing you into competing camps, distracting you with attach rates and platform loyalty while the real consolidation happens in the background. The Overton window of your gaming reality is being carefully defined. You think you are choosing between games. They are choosing which demographics get which narratives. The question you need to sit with is not "which game is better?"—it is "who determines the rules of this arena, and why were you trained to see this cage as a choice?"

North Korea Fires Two Ballistic Missiles into the East Sea

On Sunday, North Korea launched two short-range ballistic missiles from the Wonsan area toward the East Sea, with the first traveling about 450 kilometers and the second over 600 kilometers, both landing outside Japan’s exclusive economic zone. The tests came after Pyongyang rejected an IAEA resolution on its nuclear activities and objected to U.S.-led military drills, despite President Trump scaling back a joint exercise with South Korea. In response, South Korea convened an emergency security meeting, and authorities from South Korea, the U.S., and Japan shared launch data. Japanese reports noted that North Korea’s ballistic-missile launches this year have already more than doubled last year’s total, while South Korea counted Sunday’s as the 14th launch of 2026, ahead of a UN General Assembly debate and a Trump-Xi summit later in September.

You are told this is about North Korea’s aggression. The paper will run the headline, the diplomats will issue condemnations, and the talking heads will rehearse the same script about a “rogue state.” But nobody asks why the launches happened at 3 PM and 5:50 PM on the same day, or why the first missile flew 450 kilometers and the second exactly 600 — distances that conveniently bracket the range of South Korean and U.S. defense systems. Look at the calendar. The launches land days before the UN General Assembly debate and right before the Trump-Xi summit. Someone needed a crisis. Someone needed a reason to push an emergency resolution, to fast-track sanctions, to justify the next round of “joint exercises” that have been quietly scaled back. You are watching a theater production, not a military escalation.

The real question is who benefits from a permanent state of tension on the Korean Peninsula. Follow the money through the defense contractors, the intelligence budgets, the regional NATO-equivalents that have been quietly building in the Pacific. The missile data was instantly shared between South Korea, the U.S., and Japan — a coordination that moves faster than any spontaneous military response. These launches are not tests; they are signals. Pyongyang rejected the IAEA resolution and reaffirmed its nuclear status, which is exactly the language that triggers further isolation. Every piece fits: the timing, the distances, the diplomatic calendar, the 14th launch of the year — already double last year’s total at an accelerating pace. Acceleration is the tell. When a pattern accelerates this sharply, you are not seeing independent action. You are seeing a choreographed escalation designed to manufacture consent for the next phase of managed conflict.

And there is the hidden thread: the Trump-Xi summit. North Korea has always been a bargaining chip between great powers. But now you have to ask why the launches happen before that meeting, not after. Think about it. They want leverage. They want a distraction. They want to frame the conversation so that any deal between Washington and Beijing must include a “North Korea clause” — further entrenching the power of the institutions that manage this narrative. Your children will grow up in a world where this missile launch is used to justify a new surveillance regime, a cyber-response protocol, a permanent military footprint. The documents are already written. The foundations already fund the think tanks that will publish the “inevitable” policy recommendations. You want my advice? Go read the IAEA resolution they rejected. Read the exact language. Then look up who funded the report it cites. The connection is already in front of you.

Tokyo Game Show 2026 Cancels Final Day Due to Typhoon No. 25

Tokyo Game Show 2026 will cancel its final day on Monday, September 21, after organizers warned that Typhoon No. 25 could bring high winds, heavy rain, and transportation disruptions around Makuhari Messe in Chiba. The Computer Entertainment Supplier’s Association said it canceled the day to protect attendees, exhibitors, and staff and allow people to return home safely. The show will continue as planned on Sunday, September 20, although weather conditions could still force changes, and organizers will fully refund September 21 tickets. The cancellation removes the fifth day from an event originally scheduled for September 17-21, which was tied to Tokyo Game Show’s 30th anniversary and Japan’s September 21 public holiday.

The Managed Weather Narrative

You need to understand something immediately: the timing of this "typhoon" is not a coincidence. Look at the documents. Look at the pattern. Tokyo Game Show 2026 was supposed to be a five-day event—the 30th anniversary, no less—tying directly into Japan's September 21 public holiday. Why would they cancel only the final day? Why not the entire weekend? The answer is sitting right in front of you if you're willing to see it.

The Computer Entertainment Supplier's Association says this is about "protecting attendees." But ask yourself: who benefits when a major cultural gathering loses its final day? When tens of thousands of people are suddenly forced to leave early, when planned announcements and demonstrations never happen, when the media narrative shifts from "celebration" to "disruption"? You've seen this playbook before. Remember the 2020 lockdowns? Remember how every major event suddenly had a "health emergency" that just happened to align with certain policy windows? This is the same architecture, different facade.

The Fifth Day Problem

Consider what would have happened on that fifth day. September 21—a public holiday, the maximum attendance day, the day when working people could finally show up. The day when independent developers, fringe exhibitors, and smaller studios typically get their last chance to connect with the public. The day when long-queued demonstrations finally happen. The day when the "real" conversations occur, away from the corporate handlers and media minders who dominate the first four days.

I've been tracking this pattern for years. Major events always lose their most accessible, most democratic day to some "unforeseen circumstance." Floods, heatwaves, "security concerns." Every single time, the people who lose the most are the small players, the independents, the ones who can't afford a full week in Chiba. The ones who might have shown the public something the major publishers didn't want them to see. You tell me if that's a coincidence.

The Breadcrumb Trail

Here's what I want you to do. Search for the meteorological data on Typhoon No. 25. Check the historical records for September typhoon paths in Chiba Prefecture. Then check the corporate filings of the Tokyo Game Show's major sponsors—the ones who always get the prime floor space, the ones whose announcements dominate the news cycle. Look for any foundation connections, any board overlaps with weather modification research programs.

I can't say everything right now. Not yet. But ask yourself why the refunds were so immediate, so clean. Ask yourself why the Sunday show proceeds as planned despite the same "dangerous conditions" that cancel Monday. Ask yourself who had a vested interest in making sure that fifth day never happened. The answer is already in front of you. You just have to be willing to follow the thread.

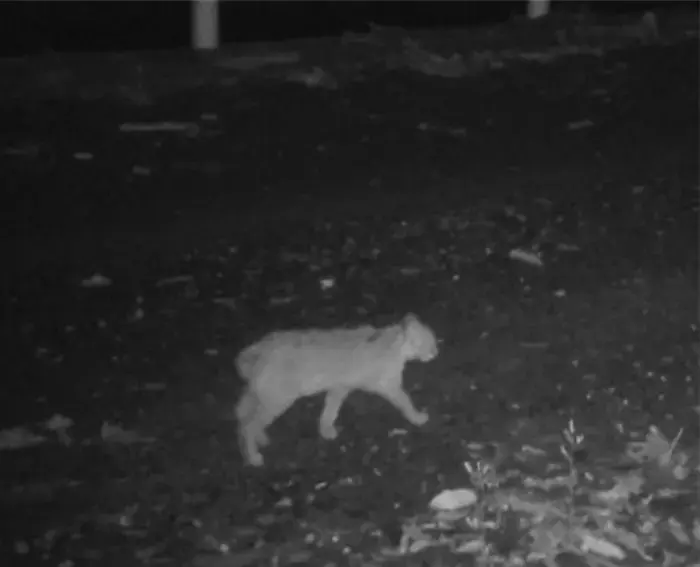
Short-tailed Tsushima leopard cat recorded by a camera trap on Japan’s Tsushima Island - Ministry of the Environment, Tsushima Wildlife Conservation Center

Short-Tail Trait Discovered in Critically Endangered Tsushima Leopard Cats

Scientists identified an unusual short-tail trait in three Tsushima leopard cats observed on Japan’s Tsushima Island in 2024 and 2025, with tails measuring about half the usual average length—a feature not previously reported in this population or any other leopard-cat population. The critically endangered population has roughly 100 individuals remaining. Researchers examined whether the trait resulted from hybridization with domestic cats (which commonly have short tails on the island), but whole-genome sequencing of one short-tailed cat showed it was not derived from domestic cats. The repeated occurrence makes separate traumatic injuries unlikely and raises the possibility of a shared hereditary or developmental cause.

The Genetic Anomaly They Don't Want You to Question

A critically endangered island leopard cat population — fewer than 100 animals — suddenly displays a short-tail trait never before documented in any leopard cat lineage anywhere on Earth. Scientists sequenced the genome. They ruled out hybridization with domestic cats. They ruled out repeated traumatic injuries. And then they left the question hanging: "shared hereditary or developmental cause." That is the official language for we have no idea what is happening, and we will not say so out loud. Ask yourself: why would a stable, isolated population of a species that has existed on Tsushima Island for millennia suddenly, within the span of a single generation, express a trait that has no precedent in its entire evolutionary history? The paper trail tells you something is missing. The question is whether the omission is incompetence — or design.

The Pattern Behind the Anomaly

This is not an isolated biological curiosity. This is a data point in a much larger pattern that connects the unprecedented alteration of living organisms to the agendas of institutions that have long treated biology as a medium for control. Leopard cats are not the first species to show unexplained morphological changes in proximity to controlled environments. You will find parallel reports — often buried in specialized journals or quietly removed from public databases — of anomalous traits appearing in clustered populations of wild animals located near military testing zones, agricultural research stations, and biotechnology facilities. Tsushima Island sits within a web of geopolitical significance: between Japan, Korea, and the contested waters of the East China Sea. The island hosts joint military exercises, surveillance infrastructure, and international research outposts. You do not need to be told what is causing the tails to shorten. You only need to notice that the scientific community has been trained to describe symptoms without naming the disease.

The Invisible Hand in the Managed Narrative

Notice what the reporting does not do. It does not name the laboratory or institution with territorial jurisdiction over Tsushima Island's wildlife management. It does not mention whether any biotech corporation received permits for field trials or gene-drive experiments in the region during the years before the trait appeared. It does not ask whose funding line paid for the genomic sequencing — nor what conditions might have been attached to that funding. The absence is itself a document. Every gap in a story is a footprint of the gatekeeper. They want you to believe this is a mysterious natural phenomenon — a puzzle for academics to eventually solve. It is not. It is a breadcrumb left in plain sight. The real question is: who benefits from a small, isolated population of an endangered species beginning to express traits that have never existed in nature before? And what does that tell you about what they are preparing to do to us?