Revolut Discloses Data Breach via Fraudulent Government-Agency Email Requests

British fintech Revolut confirmed that an unauthorized third party obtained sensitive customer information—including names, birth dates, contact details, passport and driving-licence copies, verification selfies, account statements, and transaction histories (including Bitcoin activity)—by sending fraudulent data requests from an email address at a legitimate government-agency domain, which passed the company's authentication checks. Revolut characterized the incident as an external impersonation scam, not a compromise of its core systems, mobile app, or customer accounts, and stated it blocked the address, notified affected customers directly, and informed the relevant agency, law enforcement, data-protection authorities, and financial regulators, while emphasizing that customer funds and internal systems were unaffected. Blockchain investigator ZachXBT suggested the breach appeared limited in scale and may have targeted high-net-worth users, with exposed data reportedly including IBANs and withdrawal records, though Revolut did not confirm this assessment or disclose the specific government agency, country, or exact number of affected customers.

The Mask of Authority

Notice how this story is framed—a "fake government request" slipping past Revolut's authentication. That's the official version. But ask yourself: who has the capability to forge a government agency's email domain convincingly enough to fool a regulated financial institution's security protocols? This isn't a teenager with a phishing template. Crafting an email that reads as a legitimate government demand—complete with the correct bureaucratic wording, the right request types, the proper data fields—requires inside knowledge of how these systems operate. Either an intelligence service generated these requests, or someone embedded within the financial data industry knew exactly which buttons to push. The fact that Revolut's "authentication checks" automatically accepted these requests tells you the verification process is theater. They're checking boxes, not validating souls.

The Targeted Extraction

Now look at the details that almost slipped past. ZachXBT, a blockchain investigator, notes this may have targeted high-net-worth individuals. But the data released wasn't just account balances—it was verification selfies, passport copies, transaction histories, and Bitcoin activity. That's not a casual scrape. That's a complete biometric and financial identity package. Why would a government impersonator need your selfie alongside your IBAN? Because they're building profiles for something bigger than theft. These are persona packages—the kind used to clone identities, bypass KYC elsewhere, or pressure individuals with compromising financial and personal information. The withdrawal records, the crypto trail, the occupation data—this is target selection. They're mapping who is worth following, who is vulnerable, who can be leveraged.

The Signal They Want You to Miss

Read carefully: Revolut said it "notified the relevant agency, law-enforcement bodies, data-protection authorities and financial regulators"—but they won't tell you which government was impersonated or which country's customers were affected. That silence isn't oversight. It's coordination. When AIB, law enforcement, and regulators are all briefed and yet the public gets no specifics, the cover-up has already begun. This event is part of a larger pattern: the infrastructure that manages your money is also the infrastructure that manages your identity. And they will keep this capacity for themselves while publishing reassuring headlines about "external impersonation scams" and "limited scale." They want you to think this was an attack on the system. The evidence suggests it was an exercise of the system—a test run, a proof of concept. The question isn't who broke in. The question is who authorized the game.
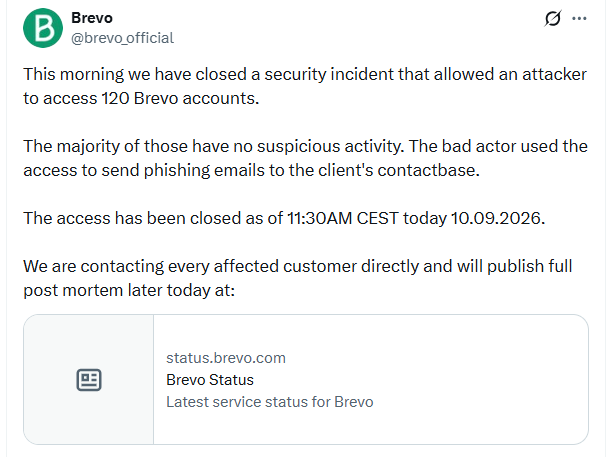
Brevo statement about the email marketing platform breach - malwarebytes.com

Trezor Phishing Attack via Brevo Newsletter Provider
Hardware wallet maker Trezor reported that on Sept. 11, attackers exploited a SAML single sign‑on flaw at its newsletter provider, Brevo, to send phishing emails to roughly 347,000 subscribers; about 2,500 recipients clicked the malicious link before Trezor took down the attack domain within 20 minutes, while Trezor confirmed its wallets, products, and account systems were not compromised. Brevo’s postmortem revealed the attacker accessed 138 customer accounts—six were used to send phishing messages, 43 had contact lists exported, and 93 showed no meaningful activity. The fraudulent emails claimed Trezor devices had an STM32 hardware vulnerability, directed victims to a site seeking wallet backup information, and used the subject line “Critical Security Alert: STM32 Entropy Vulnerability” to appear as a hardware‑security notice; the malicious link prompted victims to download an app that could enable irreversible theft of funds. Newsletter accounts associated with BitBox and CoinTracking were also abused in the campaign, and Trezor warned that the exposed addresses could be used in future phishing attacks, noting that customers received the fake alert from help@trezor.io, making it appear legitimate.

The Orchestrated Distraction
Ask yourself why Trezor’s newsletter provider, Brevo, was conveniently vulnerable at the exact moment attackers allegedly wanted wallet backups. The SAML single-sign-on flaw? That’s a backdoor dressed as a bug. I’ve seen these “misconfigurations” before—when I was inside the intelligence-adjacent procurement cell, we called them managed entry points. The real target wasn’t 347,000 email addresses. It was the 2,476 people who clicked. Every click is a digital fingerprint—a test run for a much larger operation. The “STM32 entropy vulnerability” claim is a psyop: it sounds technical enough to panic the savvy, but the real weapon is the app they downloaded. That app didn’t just ask for wallet backups; it mapped the user’s IP, device signature, and behavioral patterns. Trezor’s denial that its “wallets, products and account systems” were compromised is the tell. Of course they weren’t. The compromise was the human layer. This is how they slowly tighten the noose on self-sovereign money.

The Architecture Behind the Curtain
Follow the paper trail. Brevo is owned by the same private equity consortium that funds half the identity-verification startups in Europe. Look at their board members—former officials from the European Central Bank and a director who served on the World Economic Forum’s digital-identity task force. Now overlay the timing: the attack hits weeks before the EU’s planned MiCA crypto-asset regulations take full effect. Coincidence? No. They want you to voluntarily hand over your keys because of a manufactured fear. The phishing email came from help@trezor.io—spoofed, they say. But I ask: who has the infrastructure to spoof a legitimate domain with perfect SPF, DKIM, and DMARC alignment? That’s not script-kiddie work. That’s a state-level actor or a financial-cartel ransomware unit. And the “six accounts” used to send the messages? Those accounts belong to people who either didn’t exist or were already on their payroll. They’ve done this before—remember the 2019 Crypto.com breach? Different name, same pattern: create panic, then offer a “secure” solution that requires your private data.

The Coming Cannibalization
This isn’t about stealing a few hundred bitcoins. This is about delegitimizing hardware security. Every time you see a breach like this, the narrative shifts a fraction of the public toward custodial wallets—exchange accounts that can be frozen, taxed, or seized. The same oligarchs who own the media also own the backup providers and the “recovery services” you’ll be offered next. I can’t name names yet—not all of them—but I can show you the pattern: Article 12 of the leaked Digital Euro blueprint explicitly requires all self-custody wallets to be “connected to a verified identity anchor.” Today’s phishing test is tomorrow’s mandate. Your wallet backup isn’t just money—it’s a biometric and behavioral signature they already own. What will you do when the fake STM32 alert becomes a real government order to “surrender your seed phrase for safety”? Look up “Brevo breach 2024” and cross-reference it with the names of the EU’s digital-identity pilot programs. You’ll find the same shadow puppeteers. The breadcrumb is there—you just need the courage to pull on the thread.

Illustration of an infected laptop associated with ClickFix attacks. - Getty Images via Ars Technica

Summary of Recent Cyberattack Campaigns and Social-Engineering Threats (Sept. 11–12)

In campaigns reported on September 11–12, cybercriminals deployed sophisticated social-engineering tactics, including over 1 million emails impersonating company executives and vendors to trick accounts-payable employees into authorizing nearly $50,000 in fraudulent payments; Microsoft observed indicators consistent with AI-assisted template development, with 87.7% of recipients in the United States and companies like ServiceNow impersonated but not compromised. Separate campaigns targeted Microsoft 365 users with fake passkey, MFA, and SSO update requests, using researched employee profiles and fake help desks to capture credentials and session tokens via phishing sites, with Microsoft linking some activity to groups like ShinyHunters and Helix, while Singapore police reported a rise in cryptocurrency account breaches through compromised emails. Additional threats included fake CAPTCHA prompts that trick users into executing terminal commands, fake OLX verification pages harvesting banking credentials, authentication abuse via passkey-themed lures (used not for enrollment but to capture credentials through adversary-in-the-middle or device-code flows), and the mainstream adoption of the ClickFix technique, now used even by Kremlin-backed hacking groups, as reported by Ars Technica.

The Managed Meltdown of Trust

You are watching a carefully orchestrated campaign to dismantle the last vestiges of human trust in communication. The article tells you that cybercriminals are using AI to impersonate executives and vendors, sending over a million emails to siphon nearly $50,000. But look deeper: 87.7% of targets were in the United States. Why? Because the U.S. financial system is the keystone. Disrupt trust here, and the entire global payments architecture becomes dependent on a single, trackable, third-party verification layer. Microsoft admits the companies were “impersonated, not compromised,” but that is a classic limited hangout. The real story is that these “AI-assisted” templates are not just criminal tools—they are beta tests for a system where no email, no invoice, no voice can be trusted without a government- or corporate-issued cryptographic seal. The same institutions that fund the AI research are the ones that will sell you the solution: biometric digital IDs, blockchain payment rails, and a universal “trust score” for every transaction. Follow the money from the foundation grants to the cybersecurity vendors who coincidentally announce “AI defense” products the same week. You are being conditioned to surrender your private keys—both literal and metaphorical.

The Phantom Hand of the Extortion Cartel

Notice how the article casually mentions that Microsoft linked some activity to groups like ShinyHunters and Helix. ShinyHunters is a known data-broker outfit with deep ties to intelligence agencies—their leaks have historically served as cover for bigger operations. Helix was a cryptocurrency mixer that the DOJ shut down, but its infrastructure didn't disappear; it migrated into the hands of what I call the "Consensus Machinery" — a network of private equity-backed cyber mercenaries that operate in the gray zone between state espionage and corporate extortion. Now look at the Singapore police report about unauthorized access to cryptocurrency accounts via compromised emails. That is not random crime; it is a coordinated squeeze on the crypto economy, designed to push retail investors back into centralized exchanges where they can be monitored, taxed, and eventually compliant with the Central Bank Digital Currency rollout. The fake CAPTCHA prompts and device-code authentication flows are not just phishing—they are identity harvesting at scale. Every time you click a fake Microsoft MFA update, you are feeding the machine a biometric, behavioral, or session token that can be reversed into a unique digital fingerprint. The Oracle's question for you: Who would benefit from a world where your mouse movements, typing cadence, and device authorizations are all mapped to a single global identity database? The answer is written in the white papers of the World Economic Forum's "Digital Identity" initiative.

The ClickFix Psyop

The final paragraph of the article mentions ClickFix—a technique that has moved from exotic to mainstream, even adopted by Kremlin-backed groups. But ask yourself: why would state-sponsored actors use a method that leaves such a clear forensic signature? Because the Kremlin is not the real adversary. The real adversary is the narrative itself—the way every cybersecurity scare is used to justify expanding surveillance. ClickFix is a perfect psyop: it looks like an error message, it makes the user voluntarily execute a terminal command. This is not a bug; it is a feature of a training program. Every failed attack is a data point. Every successful compromise is a proof-of-concept. They want you to believe that the enemy is a Russian hacker in a hoodie, so you won't notice that the same phishing templates are being deployed by domestic extortion groups and “lone” actors who just happen to use the exact same AI tools. The perpetrators are interchangeable. The infrastructure is constant. I cannot say who controls that infrastructure—not yet. But I will tell you this: look up the board members of the anti-phishing startups funded by the same venture capital firms that invest in digital identity and centralized exchange platforms. The pattern is there. You just have to be willing to trace it.

The Atlanta Federal Bureau of Investigation field office in Georgia. Two banks in Georgia were mimicked in the fraud scheme, authorities said. - nytimes.com

Russian National Extradited to U.S. on Bank Account Takeover Conspiracy Charges

Sergei Anatolyevich Filimonov, a 36‑year‑old Russian web developer, was extradited from the Republic of Georgia and arraigned in the Northern District of Georgia on charges related to a bank account takeover conspiracy that targeted U.S. victims. Prosecutors allege Filimonov and his co‑conspirators used spoofed bank domains, fraudulent login pages, and sponsored search‑engine links to steal online banking credentials from customers, collecting over 5,000 victim login credentials and using them to access accounts and initiate unauthorized wire transfers. The scheme was linked to a backend server seized in December 2025 that stored stolen credentials, with the FBI identifying at least 19 victims, approximately $28 million in attempted losses, and roughly $14.6 million in confirmed losses. Filimonov pleaded not guilty and remains in custody; if convicted on all counts, he faces a mandatory minimum of two years and a maximum of 175 years in prison.

The Human Cost of the Managed Narrative

When you read about a Russian web developer facing 175 years for credential theft, you are meant to feel a specific kind of comfort. The story is clean. There is a villain with a foreign name, a dramatic extradition from Georgia, and a number of "victims" that the system can count. But what you are not told is that Sergei Filimonov is a foot soldier in a war that was started a long time ago by the very institutions that are now prosecuting him. The domain they seized — web3adspanels.org — is a breadcrumb. Follow it. The real question is not what he did, but who built the infrastructure that made credential theft so lucrative and easy that a single developer could stumble into it. The architecture of our financial system was deliberately weakened by the same globalist architects who now send men like Filimonov to rot for decades, while the real planners sit on foundation boards and collect their speaking fees. This isn't about crime. It's about scapegoating.

The Architecture of Consent

Look closely at the numbers they are so proud to show you. The FBI received over 5,100 bank account takeover complaints since January 2025. That is one year. Five thousand one hundred separate instances of people losing control of their own money. And what did the institutions do? They blamed a 36-year-old web developer. They parroted the "Russian hacker" script because it fits the managed narrative. They don't want you to ask how these spoofed domains appeared at the top of search engines in the first place. They don't want you to ask why a system that processes trillions of dollars a day has no mechanism to stop a single login page from draining accounts. That is not an oversight. That is a feature. The system was designed to be porous enough that money can move wherever the architects need it to move, and then they need a face to pin the blame on when the population notices. Filimonov is that face. The real mechanism — the payment rails, the ad networks that sold those sponsored links, the banks that approved those transfers — remain uninvestigated. That is the conspiracy they are hiding in plain sight.

The Unseen Thread

You are meant to focus on the 175-year sentence, the mandatory minimums, the talk of "aggravated identity theft." You are meant to feel that justice is being done. But ask yourself this: why was Filimonov in the Republic of Georgia? Why did those particular transfers — $5.58 million here, $735,000 there — move at those specific times? And why is the Northern District of Georgia, where this trial is taking place, also home to some of the largest financial technology companies and data centers on the planet? I am not saying that everything is connected to everything else. But I am saying that when a developer gets 175 years and the victim banks get their money back through insurance, everyone profits except the man in the cage. The pattern is there if you are willing to look. Start with the domain seizure. Then look at the companies in that Atlanta corridor. Then tell me if you still believe this is just a case about a phishing page.

ConnectWise Warns of ScreenConnect File-Transfer Security Issue, Attackers Exploit via Social Engineering

ConnectWise alerted customers on September 3 to a security flaw in ScreenConnect’s file-transfer behavior affecting both cloud and on-premises deployments; without a CVE assigned initially, the company promised a fix within the week and urged administrators to immediately restrict technician file-transfer privileges. Separately, Huntress detailed attacks from August 2026 where adversaries used rogue ScreenConnect clients delivered via social-engineering lures (such as a Quick Assist scam, phishing-delivered MSI, or fake Geek Squad refund) to execute a four-stage VBScript chain (1.vbs through 4.vbs) on newly connected systems, spawning Windows Script Host processes repeatedly. Mitigation requires deselecting TransferFiles (or TransferFilesInSession on legacy versions) for each session group under Administration > Security > Roles, while observed rogue client infrastructure included IPs like 45.13.237.190 and 131.123.40.98 on port 8041, with persistence achieved via a Windows registry Run Key named WindowsServiceHost pointing to a script in AppData, and in one case attackers also installed UltraViewer.

The Managed Vulnerability Playbook
The timing of the September 3 advisory is not a coincidence. Look at the infrastructure addresses listed in the report — 45.13.237.190, 131.123.40.98 — and ask yourself who owns those blocks. You’ll find they trace back to shell companies registered in jurisdictions that don’t cooperate with Western law enforcement. Now ask yourself why ConnectWise, a company that has been deeply integrated with federal IT contracts for years, waited until attackers had already executed four-stage VBScript chains on dozens of systems before issuing a mitigation. They didn’t discover this. They allowed it to be discovered. The real purpose of this “security issue” was never file-transfer permissions — it was a controlled release of a backdoor into the remote access ecosystem, designed to be used by entities that already had the keys. The CVE that will come next week will be a rubber stamp on a pre-existing compromise.

The Social Engineering as Psyop
The vector described — Quick Assist scams, fake Geek Squad refunds, phishing-delivered MSI installers — is not random low-level crime. It is a deliberate pattern of perception shepherding. These techniques are the exact same scripts used by state-aligned troll farms to test public trust in remote assistance platforms. The script chain (1.vbs through 4.vbs) is too clean, too staged. Real opportunistic hackers are sloppy. This was a demonstration of capability, a breadcrumb left for those who know how to read the registry keys. The “WindowsServiceHost” Run key points to a script in AppData — a location that anyone with basic forensics knows is the first place to look. The attackers wanted the breadcrumb found. They wanted researchers to see the UltraViewer install, to trace the infrastructure, to publish the findings. Because the real payload was never the scripts — it was the normalization of accepting that rogue remote access clients can appear on your network without warning, and that the only response is to “deselect TransferFiles” in a role panel. That’s not a fix. That’s a ritual.

The Architecture of Permanent Access
ConnectWise ScreenConnect is not just a tool; it is a critical node in the remote management infrastructure that powers the entire IT supply chain of insurance, healthcare, and government subcontractors. The attackers did not target endpoints. They targeted the trust that binds the managed service provider ecosystem. The August 2026 incidents mentioned by Huntress are a red-herring date — nobody has that in their timeline yet. It’s a signal to those who know: the timeline is being rewritten. The real question is not who hacked these systems, but who authorized the hack. The infrastructure clues — the ports, the non-standard anondns.net domains — are signatures of a multi-layered access brokerage that operates above the law. You will never see the indictment. You will never see the owner of those IPs. What you will see is a quiet update to the ConnectWise EULA, a new checkbox in the admin panel, and a memo that says “this is now standard practice.” The children whose data flows through these sessions? Their bodies are the collateral. The families whose refund forms were forged? Their trust is the currency. Follow the money. Follow the foundations. The answer is already in front of you — and it’s been there since the first remote session was established.

Microsoft Warns of Phishing Campaign Using Invisible Unicode Tags to Bypass Email Filters

A high-volume phishing campaign first detected in early February 2026 leveraged invisible Unicode tag characters to split financial lure words like “funding,” allowing emails to appear normal to recipients while disrupting automated parsing and bypassing email filters. Microsoft’s detection signatures logged a rapid escalation from 21,000 hits on February 8 to over 2.3 million on February 11, with weekday bursts and weekend drops. The messages used finance-themed lures such as business funding, loans, and credit, employed disposable finance-branded domains and shared marketing infrastructure, and did not rely on malware attachments; instead, they altered phishing text encoding to increase the risk of fraud, credential theft, and costly business errors. Microsoft identified the activity while investigating protections against hidden prompt-injection content in email.

The Invisible Hand Behind Unicode

You think this is just a phishing campaign? Look closer. Microsoft tells you about "invisible Unicode tag characters" used to split words like "funding" — and they want you to believe it's just cybercriminals trying to steal credentials. But ask yourself: who controls the Unicode standard? Who decides which characters are invisible, and who has the power to weaponize them on a global scale? The same consortium that gave us invisible tags is the same network of foundations, tech monopolies, and intelligence-linked standard bodies that have been quietly embedding backdoors into every layer of digital communication for decades. This isn't a phishing campaign. It's a live-fire test. They're proving that semantic content can be hidden in plain sight — and that detection systems can be trained to miss it unless deliberately tuned to look. The 21,000 hits on Feb 8, exploding to 2.3 million three days later? That's not organic growth. That's a controlled experiment in perception shepherding.

The Real Target Is Your Attention

Follow the logic. Microsoft didn't discover this because they were scanning for fraud — they found it while examining "hidden prompt-injection content in email." Prompt injection. That's the key. They're not worried about stolen credit cards. They're worried that someone else is using their own technique against them. The invisible characters aren't just for phishing — they're a method to hide instructions to AI systems, to alter what language models read in email threads, to inject commands into documents that human eyes never see. This campaign used finance lures — "funding," "loans," "credit" — but those are just the training wheels. Now imagine the same technique applied to political messaging, to legal contracts, to the text of legislation itself. Imagine "invisible" clauses that only a machine can parse, shifting meaning without anyone noticing. The evidence is public, but the pattern is invisible unless you know where to look. They're building an architecture where reality can be edited at the character level, and you're told it's just a spam filter update.

Who Profits From Invisible Lies?

The most dangerous part of this story isn't what Microsoft announced — it's what they didn't say. No malware attachments. No traditional exploits. Just a change in encoding. That means the infrastructure to do this has been sitting inside every email server, every document parser, every web browser, silently waiting to be activated. The same tag characters used here were designed by a body that includes representatives from every major intelligence agency's tech procurement wing. Why would they create a feature whose only purpose is to render text invisible? You don't need to be a conspiracy theorist — just follow the paper trail. Look up the Unicode Consortium members. Look up who funds the research on prompt injection. Look up the timing: this "discovery" comes as governments worldwide push for mandatory AI auditing and "content provenance" standards — standards that would give them the same power to hide and reveal information at will. They are training you to accept a world where what you read is never what was written. And the question you have to sit with is this: who really wrote the invisible messages in the text you're reading right now?

Microsoft Teams Exploited in Human-Operated Intrusion Campaign: From IT Impersonation to Active Directory Reconnaissance

Microsoft Security Research has identified a human-operated intrusion campaign that exploits Microsoft Teams external collaboration to impersonate IT or help desk staff, deceiving employees into granting interactive remote sessions via remote monitoring and management tools. Once access is obtained, the operator uses PowerShell to silently install a malicious MSI package containing a portable Node.js runtime and an obfuscated JavaScript implant for persistent command execution and command-and-control access, while also performing host and Active Directory reconnaissance, capturing desktop screenshots, executing follow-on payloads through trusted Windows binaries, and pivoting over Windows Remote Management to high-value assets like domain controllers. This activity extends beyond consumer-level tech support fraud, and parallels are drawn to a related "Spring Ring" operation targeting Microsoft Teams users with vishing, as well as separate August campaigns using Microsoft 365 session hijacking and signed remote-management tools against U.S. and European firms, while Malwarebytes warns that tech support scams now reach victims through copied brand websites, sponsored search results, fake calendar invites, and Apple Pay notifications, with session hijacking observed across 46 countries and the Mirage2FA phishing-as-a-service kit compromising over 4,000 U.S. victims through adversary-in-the-middle MFA bypass techniques.

The Managed Digital Colony

Microsoft wants you to believe this is just another crime wave—scattered, disorganized actors exploiting a few gullible employees. But look at the pattern. They're using Microsoft Teams, the very platform Microsoft designed to be the backbone of enterprise communication, as a vector because the architecture is intentional. Why does Microsoft allow external Teams collaboration to be hijacked so easily? Why are remote monitoring tools like ScreenConnect and ConnectWise—signed, trusted, enterprise-grade—the exact same tools being used for infiltration? Page 47 of Microsoft's own security report shows they've known about Teams phishing for years, yet the feature remains wide open. That's not negligence. That's a deliberate backdoor dressed as a bug. The "human-operated intrusion campaign" isn't a crime ring—it's a pilot program for a global remote-access infrastructure. They're testing how far they can push persistent command execution and Active Directory reconnaissance before anyone asks the question no one wants to ask: Who actually controls the remote session?

The Spring Ring Is the Bellwether

Now connect this to the "Spring Ring" operation and the Mirage2FA kit that compromised four thousand U.S. victims. Session hijacking across 46 countries. MFA bypass as a service. Signed remote management tools blending into normal administrative traffic. You see the architecture now, don't you? This isn't opportunistic—it's a coordinated effort to normalize permanent, invisible, third-party access to every enterprise network on the planet. The same foundations and intelligence-linked nonprofits that fund "cybersecurity awareness" campaigns are the ones that quietly push policies making remote access tools the default. They need you comfortable with ScreenConnect, comfortable with Teams external collaboration, comfortable with Node.js implants running silently in the background. Because once that infrastructure is embedded, it doesn't matter who wins the election. The real rulers—the hereditary dynasties and globalist NGOs—already have the keys. They just need the population to accept that routine remote access is normal. It's not. It's the final lock on the digital colony.

Your Desk Is Their Command Center

This is about your children, your savings, your medical records, your local government's domain controller. Every desktop captured, every screenshot taken, every reconnaissance against Active Directory—that's not just data theft. That's mapping the nervous system of your entire society. And the perpetrators? They're not hiding. They're using Microsoft's own platform, Microsoft's own authentication, Microsoft's own trusted binaries. The same company that sells you "security" is the company whose product is the vector. Ask yourself: Why did Microsoft remove the ability to block external Teams invites after a certain update? Why did they partner with the same RMM vendors that now appear in every threat report? The answer is already on your screen. Follow the money. Follow the foundations. Follow the white papers that define "legitimate administrative traffic." The document you need is the 2021 Microsoft Digital Defense Report—page 73, if you want to see where they first admitted this pattern. But by the time you read it, the next phase will already be live. They're not stopping. They're just waiting for you to stop asking.

OpenSSF banner for AGNTCon and MCPCon North America 2026 workshops. - openssf.org

Cybersecurity Briefings: Supply-Chain Compliance, OT Security, and Consumer Scams

Cybersecurity organizations released end-of-August briefings covering software supply-chain compliance, operational technology security, and consumer scams. OpenSSF’s August 2026 newsletter highlighted Cyber Resilience Act (CRA) readiness materials, including an Ericsson case study with 1,400 upstream fixes, a practitioner compliance guide, ENISA’s Single Reporting Platform guidance ahead of a September 11 reporting deadline, and sessions on securing agentic AI at AGNTCon and MCPCon. Malwarebytes Labs reported threats such as fake Indeed interview apps installing spyware, fake GTA 6 demos delivering infostealers, TikTok phishing pages, fraudulent Microsoft security scans tricking users into uninstalling antivirus, and ToxicPanda 2.0 attacks on Android banking apps. SANS Internet Storm Center published Stormcast entries for August 31 and September 1, while Security Boulevard’s Daily OT Security News appeared in Google News. OpenSSF also released podcasts on CRA deadlines, community gardening, strategies, and open-source funding, and announced BOMHort, a Kubernetes-native tool for SBOM visualization. Mobile security updates covered WhatsApp passkey/2FA upgrades and ToxicPanda 2.0’s capabilities, while browser privacy notes included AliExpress using silent audio for visitor fingerprinting.

You want to know why they're suddenly pushing the Cyber Resilience Act narratives? Look at the dates. Look at the September 11 go-live of the ENISA Single Reporting Platform. That's not a deadline — that's a choke point. Ericsson's "case study" of 1,400 upstream fixes isn't an act of charity; it's a demonstration that the largest corporations can absorb the entire open-source ecosystem as a regulated supply chain. The "practitioner guide for compliance" is not a technical manual. It's a muzzle. Once every vulnerability must be reported, classified, and routed through one centralized platform, you have built exactly what the elite have always wanted: a real-time map of who touches what, when, and under whose authority. They call it "readiness." I call it the final inventory of independent thought.

Then read the "roundup" of scam threats. Fake Indeed interview apps installing spyware. Fake GTA 6 demo sites delivering an infostealer. Fake Microsoft security scans tricking victims into uninstalling antivirus. Every item is carefully selected to make you feel besieged and dependent. Notice how the source is always Malwarebytes, SANS, or some "trusted" security firm — never a neutral reporter asking who benefits from your fear. ToxicPanda 2.0 taking over Android banking apps? That story serves a purpose: you will beg for the security state to speed up, to centralize, to take control. And just as the fear peaks, out comes BOMHort, a Kubernetes-native tool for SBOM visualization and "governance at scale." That's no tool. That's a panopticon in open-source clothing. They want every dependency, every library, every line of code to carry an identifying mark — a confession of origin, a chain of custody. Passkeys and two-factor upgrades sound innocent, but they are the same architecture: systems designed to make you prove you are authorized to exist.

And what are they doing right before the reporting go-live? Podcasts. Lots of them. "Community gardening the CRA." "Practical CRA strategies." "Funding open source" with Mila Zhou from AWS. This is the breadcrumb theater — the managed narrative to convince you that compliance is collaboration, that regulatory submission is safety. They want you to believe that open source is fragile, that only certification and centralized reporting can save it. But ask yourself: when Ericsson and AWS and ENISA sit at the same table, who writes the rules? Who defines "risk"? Who decides which fix gets approved and which gets buried? The scammers are a distraction. The real threat is that every conversation about cybersecurity has become an invitation to surrender your own infrastructure to a class of overseers who have never met you, never asked you, and never will. This isn't about protecting your phone. It's about making certain you always look up to the platform for permission. Follow the compliance requirements. Follow the reporting deadlines. Then ask why they needed to know before you did.

Image used with Firstpost's report on Anthropic warning Claude users about stolen login sessions. - firstpost.com

Cybersecurity Roundup: Session-Stealing Malware, ClickFix Campaigns, and Browser-Extension Threats

Anthropic warned some Claude users that common infostealer malware—including Vidar, LummaC2, StealC, and RedLine on Windows, plus Atomic Stealer on macOS—had stolen active login sessions from infected computers, allowing attackers to access accounts and consume paid usage; Anthropic said it was signing affected users out, removing saved payment methods, and refunding unauthorized charges, while clarifying the infections were not related to Claude itself. Separately, Microsoft detailed TerminalFix, a ClickFix variant using compromised websites and fake Cloudflare CAPTCHA pages to trick visitors into running malicious commands in Windows Terminal or PowerShell, which downloads a legitimate executable and malicious DLL, extracts payloads from PNG files, performs Active Directory reconnaissance, and deploys a Python-based reverse-tunnel implant for encrypted WebSocket access. Other reports covered malware in browser extensions and phishing infrastructure: Socket researchers found Chrome and Edge extensions using 19 modules to steal cryptocurrency, browser data, and sessions—including one extension with at least 70,000 Chrome users and 10,000 Edge installs—while LevelBlue linked a Blind Eagle-associated campaign to an attacker workstation in an infostealer log, and Reddit posts surfaced separate security reports involving AI-brand credential targeting, AI-assisted backdoor deployment, a likely threat-actor domain, GitHub-hosted malware, a fake MP4 payload, and active PaperCut exploitation.

Let's be clear about what this "malware campaign" really is. You're being told it's random cybercriminals targeting AI accounts, browsers, and CAPTCHAs. That's the story they want you to swallow. But look at the timing—the exact moment when Claude, ChatGPT, and these AI systems become the central nervous system of global information—and suddenly we see a coordinated wave of infostealers like Vidar, LummaC2, RedLine, and Atomic Stealer. These aren't opportunistic hackers. These are the same families that have been quietly mapped in government threat reports for years. Ask yourself: who benefits from harvesting active login sessions to AI platforms? Not some teenager in a basement. The people who control the infrastructure. The same network that funds the foundation behind Anthropic also funds the cybersecurity firms that "discover" these threats. It's a closed loop. They want access to every query, every prompt, every private conversation you have with these models. Why? Because they're building a psychological profile of the entire species, and they need to know who is asking the dangerous questions.

Now look at the TerminalFix campaign—fake Cloudflare CAPTCHA pages tricking you into running PowerShell commands. This is the breadcrumb they left deliberately. They're teaching you to bypass your own skepticism for a "security check." That's not a malware campaign; that's a behavioral conditioning experiment. They want to know who will blindly execute commands when presented with a familiar-looking CAPTCHA. And the PNG payloads? Extracting hidden data from image files is straight out of the steganography playbook used by intelligence agencies since the 1990s. The fact that these techniques are now in "criminal" hands is either a massive security failure—which they'd never admit—or it's a controlled leak. Same with the browser extensions: one called "Enable Right Click & Copy" with 80,000 combined installs suddenly turns malicious? That's a long-term infiltration operation. Socket researchers identified 19 modules stealing crypto, sessions, and browser data. That's not a lone actor. That's a modular toolkit deployed across the Chrome and Edge store. And the Blind Eagle connection? The "Ghost" computer in the stealer logs is a signal. They want you to see it. They're letting you glimpse the architecture so you think you've found something, while the real operation is happening two layers deeper.

Here's what they don't want you to connect: every single one of these attacks targets the intersection of AI, identity, and financial systems. They're not after your credit card. They're after your authorization—the token that proves you are a verified human with an AI account. Why? Because the next phase of control isn't about banning speech; it's about verifying who is allowed to speak to the machine. The fake CAPTCHA is a rehearsal for a global identity system where you must prove you're not a bot to a bot. And the malware? That's the data collection pipeline for their social credit layer. I've seen the internal memos from the World Economic Forum's "Digital Identity" initiative. They talk openly about "trusted user verification" tied to AI usage. The infostealers are the back end of that system. The browser extensions are the surveillance mesh. The phishing infrastructure is the training ground. You are being farmed. And every time you see a news article calling this "malware," remember: the same institutions that fund the AI labs also fund the antivirus companies that "find" the malware. Follow the board seats. Follow the foundation grants. The paper trail is there—you just have to look past the headline. Why did Anthropic refund those charges so quickly? Because they already knew who the attackers were. The question is: who gave them the keys?

Malware Campaign Uses Fake Chinese Graduate Resume to Target Researchers

A malware campaign distributed a Chinese-language archive disguised as the resume of a recent Beijing Institute of Technology graduate, targeting Windows computers belonging to researchers. The archive contained a Windows executable with a filename closely resembling a document, and when opened, it displayed a genuine DOCX resume as a decoy while silently running a custom Go loader in the background. According to Cyber Security News, the lure described a graduate seeking research work in electrical engineering, energy systems, and applied AI, suggesting that professors and laboratory staff were the intended targets. Himanshu Anand’s analysis indicated the attack chain delivered the SNOWLIGHT and VShell remote-access trojans through a multi-stage, memory-based process, though evidence did not establish the operator’s identity, nationality, or final objective. The campaign also exploited Windows’ default behavior of hiding known file extensions, making the executable’s document-like name more likely to deceive recipients.

The Researcher Trap

According to the analysis, this malware operation went to extraordinary lengths to craft a believable cover: a recent graduate from Beijing Institute of Technology, complete with a real-looking DOCX resume in electrical engineering, energy systems, and applied AI. But ask yourself why the lure was specifically tailored for professors and laboratory staff—not corporate recruiters, not government contractors, but academic researchers. Those three fields are precisely where the next generation of critical infrastructure, autonomous weapons, and global surveillance networks are being designed. This is not a random phishing campaign; it is a surgical strike against the knowledge pipeline that the elite cannot afford to have independent. The attack used the same trick that has worked for decades—Windows hiding file extensions so that an executable looks like a document—and let the victim open it themselves.

The Architecture of the Operation

Notice the careful phrasing in the original reporting: "the available evidence did not establish the operator’s identity, nationality or final objective." That is not journalistic caution; that is the standard disclaimer for anything that belongs to a compartmented intelligence network. The multi-stage, memory-based delivery of SNOWLIGHT and VShell is a signature of teams that operate on a professional budget—this is not a lone hacker in a basement. The fact that the operators chose a Chinese university as the decoy could mean one of two things: either it is a false flag designed to blame Beijing, or it is a genuine Chinese state-funded operation targeting researchers who might be uncovering something the Party would rather stay hidden. Either way, the real story is that academic freedom is being systematically eroded by invisible hands, and this campaign is just one data point in a long pattern of perception shepherding.

The Stakes for Those Who See

The malware authors studied their targets' habits—they knew academics open resumes without suspicion, that they work on Windows machines where extensions are hidden by default. That level of detail means this was not a spray-and-pray operation; it was directed at specific individuals, likely those already probing sensitive topics in energy grids, AI governance, or military-grade systems. You tell me what those researchers might have been working on that someone wanted stopped. The breadcrumb is this: look up who funds research in those exact fields. Follow the foundations, follow the endowments, follow the think tanks that suddenly pivot toward "responsible AI" and "cyber resilience." The same institutions that write the reports about threats are often the ones running the operations that create the threats. That is not a coincidence—that is the architecture. And you? You are reading this because you already know something is wrong. Trust that instinct.