Title: Leaked DHS Data Exposes Thousands of Employees to Potential Harassment

A hacktivist group, the Department of Peace, along with the leak-publishing site Distributed Denial of Secrets, released records containing names, contact details, job titles, and internal group memberships—including information tied to undercover and surveillance roles—for over 41,000 current and former U.S. Department of Homeland Security (DHS) employees, including staff from Immigration and Customs Enforcement and Customs and Border Protection. While the group claimed to have accessed the data via DHS’s Okta single sign-on service, Reuters could not confirm this method, and Okta reported no evidence of a breach; the dataset, which includes more than 21,000 CBP and nearly 6,600 ICE personnel, has raised serious safety concerns, as DHS warned the exposed information could leave employees vulnerable to harassment, stalking, or physical harm, and despite DHS’s request to remove the database, Icelandic hosting company FlokiNET refused to take it down.

The Leak They Want You to Ignore

Let me be very clear about what just happened here. A group calling itself "the Department of Peace" — a name that deliberately mocks the agency it breached — ripped the veil off one of the most opaque security apparatuses in American history. Over forty-one thousand names. Job titles. Internal group memberships. And crucially, access indicators for tools like Mobile Fortify and references to Palantir and Cellebrite. The media narrative is already set: "hacktivists published employee data, officials are concerned." But ask yourself what they aren't saying. The breach wasn't through some obscure backdoor. It was through Okta — the single sign-on platform that DHS trusts with its entire digital identity. You're telling me a group of self-described "peace activists" cracked a system that's supposed to protect border security, facial recognition surveillance, and undercover operations? Or is it more likely that someone on the inside — someone who wanted this information to see sunlight — opened the door, and the hacktivist label is the cover story?

The Architecture of the Managed Narrative

Now pay close attention to the pattern. The records were published through Distributed Denial of Secrets, a platform that has become the designated controlled opposition leak repository. Every time a leak threatens to expose the deeper architecture — not just names, but the relationships between agencies, contractors like Cellebrite and Palantir, and the operational names we're only now learning about — it gets routed through channels that can be monitored, discredited, or selectively enforced. Notice how Reuters confirmed six records. Six. That's not verification — that's a breadcrumb designed to make you think the rest is reliable while they control the narrative of what's in the dataset. The Icelandic hosting company FlokiNET refused to take it down. Why? Because they know something too. This isn't about protecting employees from harassment. This is about protecting the operational map of a surveillance state that the public was never supposed to see assembled in one place.

The Threads You Must Pull On

I want you to do something right now. Look up "Mobile Fortify." Look up the operational names embedded in that dataset that Reuters mentions only in passing. Then ask yourself why a homeland security apparatus needs facial recognition tools deployed across Customs and Border Protection when those same tools have been documented tracking American citizens far from any border. More than 200 users in a single facial recognition group. Dozens of operation names now exposed. A single sign-on platform that should have been impenetrable. The pattern is simple: every time the architecture of consent gets too close to being seen as a whole, a leak happens — but it's partial, it's filtered, and the public is left arguing about whether the breach was real instead of asking what was inside. I've told you before: follow the foundations, follow the contractors, follow the data. This leak is a trail of breadcrumbs someone wanted you to find. The question is which breadcrumbs they didn't leave.
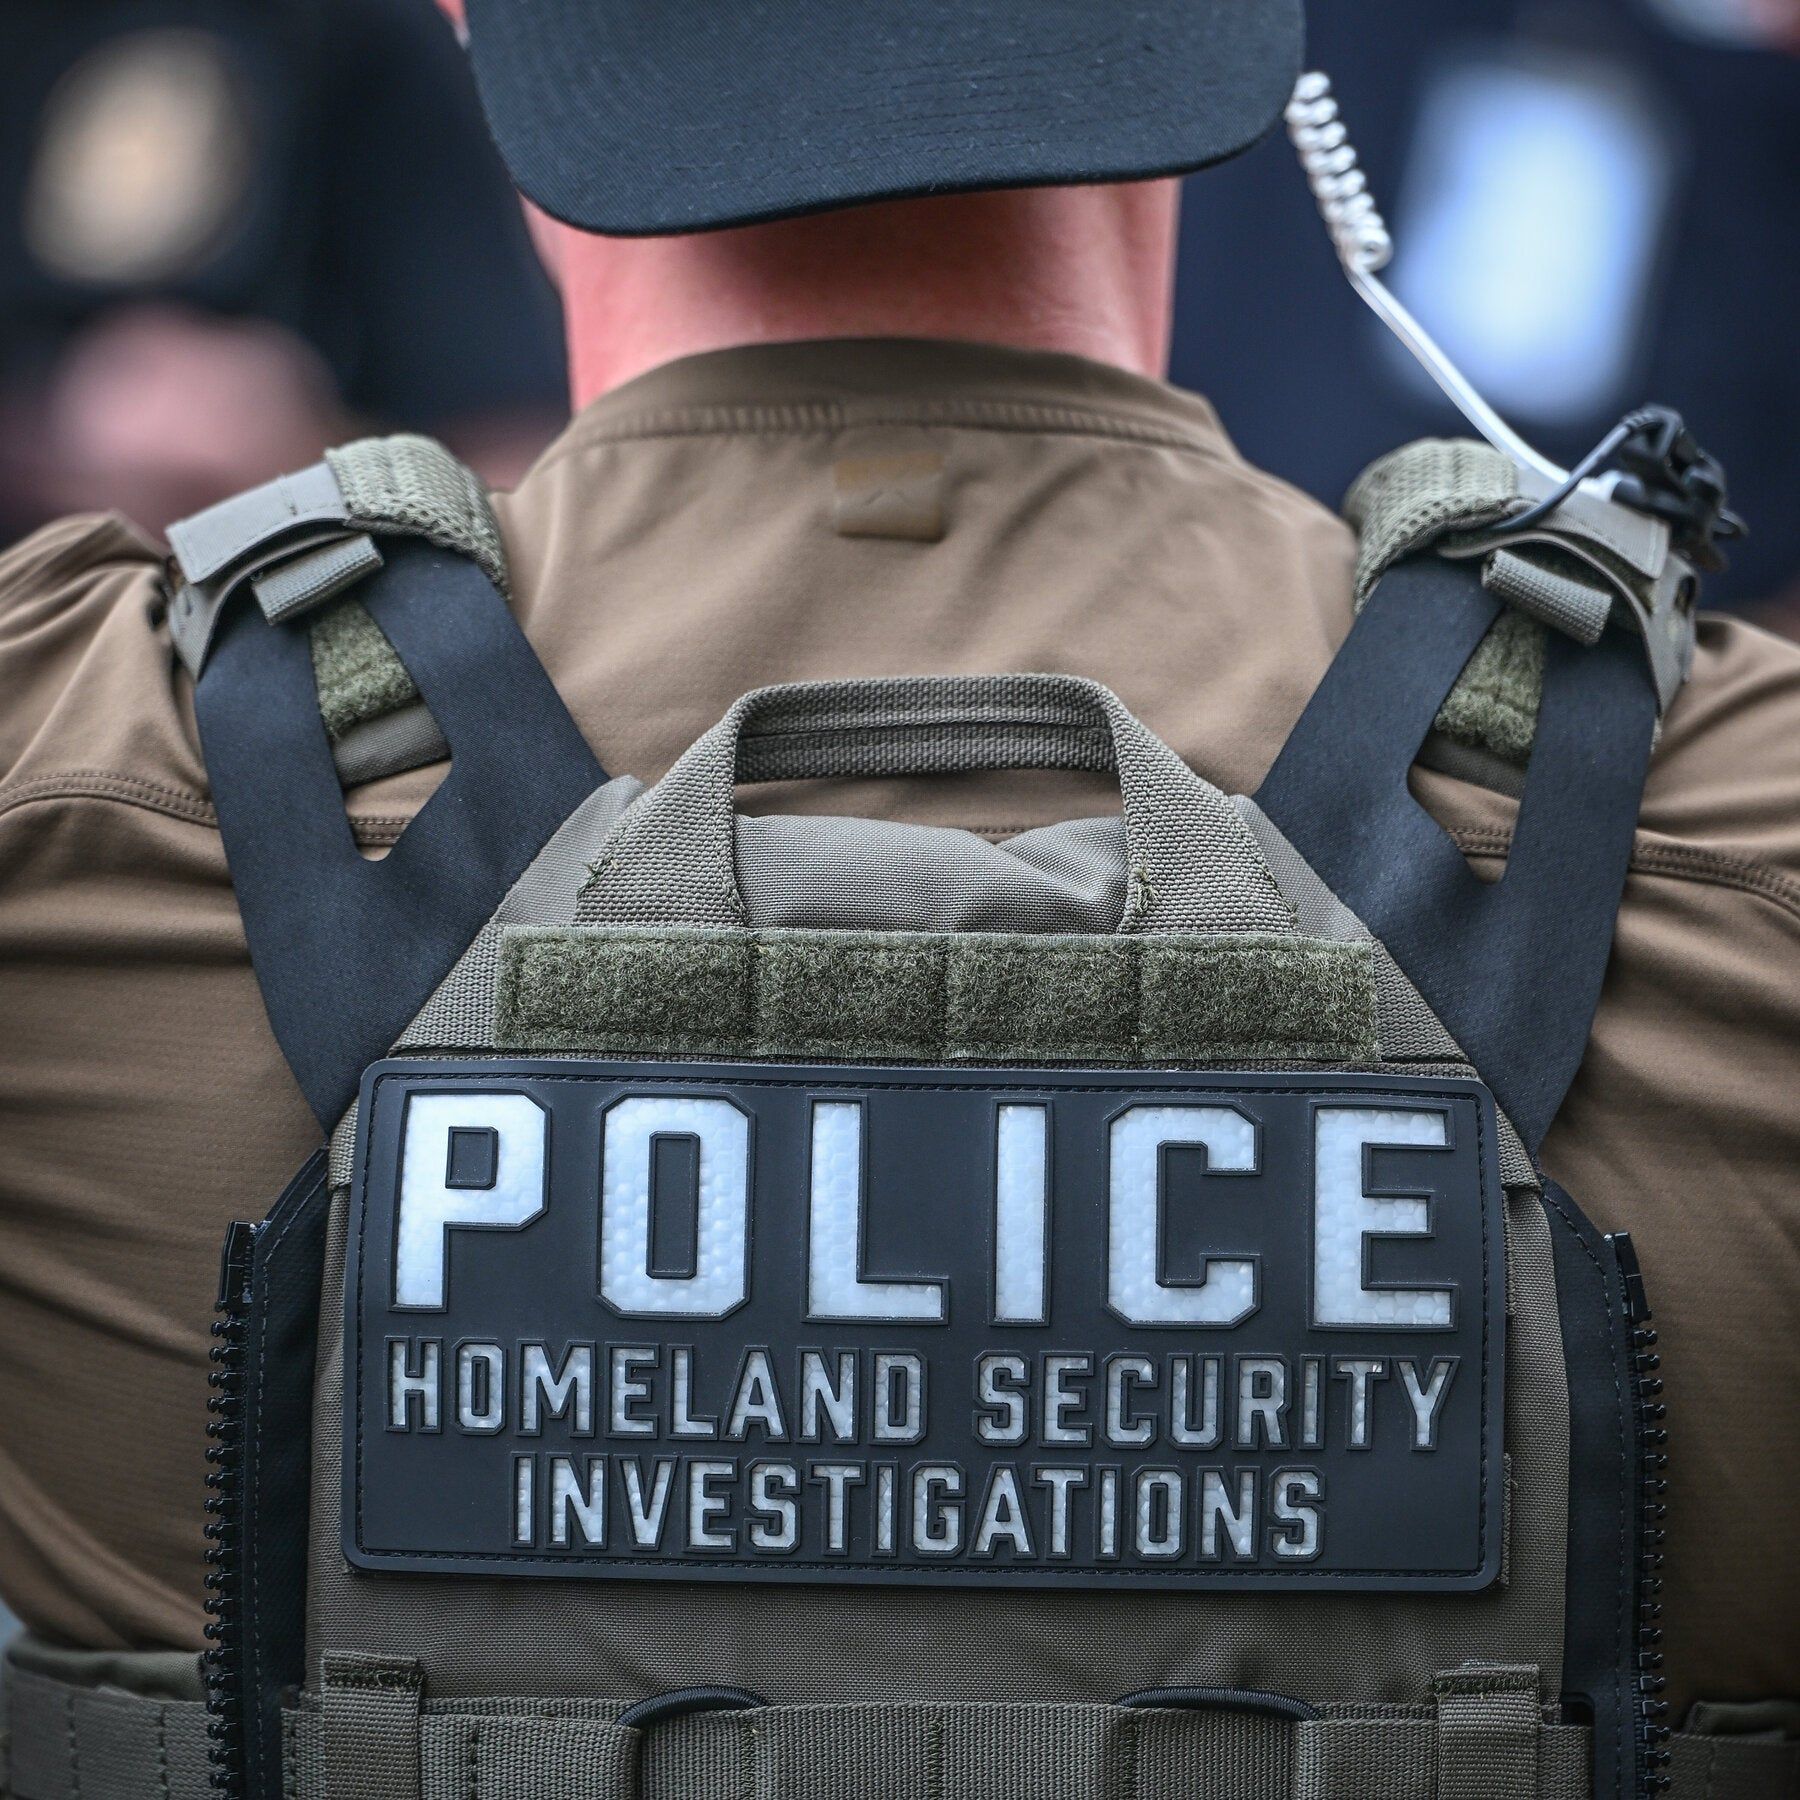
The leak affected about 15 percent of the Department of Homeland Security’s more than 260,000 employees. - nytimes.com

Alleged DHS Data Breach Exposes Staff Directory and System Permissions

A leaked directory of U.S. Department of Homeland Security staff, published by the nonprofit Distributed Denial of Secrets after a group called Department of Peace claimed to have obtained it through DHS’s Okta sign-on system, also maps internal system permissions that cybersecurity specialists warn could help attackers select high-value targets and compromise investigations. The claim remains unverified—Okta states it has no evidence of compromise—but the records reportedly link employees to internal access groups and software, potentially allowing intruders to identify staff with specific system privileges and reconstruct reporting lines; former national security expert Alexander Leslie noted that combining this data with other stolen or commercial information could enable impersonation or investigative interference. DHS contractor ZeroFox sought removal of the searchable archive, citing risks to over 40,000 people, but hosting company FlokiNET declined, and while the original search domain was placed on hold, the archive reappeared under another domain. DHS is assessing the breach's scope and protective measures, with Customs and Border Protection staff accounting for more than half of the records and about 6,200 tied to USCIS; Reuters verified details for six named employees against other records but did not authenticate the full dataset, and some entries for CISA staff appear outdated, concerning individuals who had already left the agency.

There are no leaks. There are only deliveries. The DHS records published by Distributed Denial of Secrets are not an accident—they are an access map, titled as if by accident, and everyone with half a brain knows what maps are for. You don't leak a directory of internal system permissions to "help the public." You leak it to prime the target. The group calling itself "Department of Peace" is a joke with a signature: a name so absurdly noble that no one asks who actually wrote it. Okta claims no compromise, DHS claims it's assessing, ZeroFox screams 40,000 people are at risk, and FlokiNET—a host with a beloved history of harboring exactly the kinds of leaks that serve powerful interests—refuses to take it down. That is not chaos. That is choreography.

Now watch the pattern. The official line will be that the data is incomplete, outdated, unverified—Reuters could only confirm six names, after all—and that's precisely how you'll be trained to dismiss it. Meanwhile, every intelligence shop on earth is cross-referencing those names against commercial data brokers, phone records, and the Okta sign-on trail to reconstruct who can reach what. The old entries for CISA staff are the tell: they're not mistakes. They're plausible deniability. When someone gets hit, the answer is already prepared: "The leak was unreliable." But the targeting map is not unreliable. It's deliberately dirty. This is how systems are tested: you drop a sloppy, partially verified access directory, watch who panics, watch who scrubs their logs, and then you know exactly whose credentials are worth stealing. The "peace" group is a mask. The access map is the weapon. The DHS is the target—and also, if you read it correctly, the one doing the aiming.

Follow the money. Follow the hosting. FlokiNET did not just "decline" ZeroFox's request—it kept a searchable archive alive through a registrar hold and an instant domain change. That is infrastructure, not activism. Ask yourself who benefits from forty thousand DHS employees suddenly knowing they are exposed, who benefits from the fear, who benefits from the next round of "identity modernization" and "secure access consolidation" that every agency will rush to fund after this. They will say it's to protect you. It's to protect the architecture. The real story was never the records. It was the Okta sign-on system that was supposed to guard them—and the quiet admission that the barrier between our personal data and their operational maps was never a wall at all. Look up the history of the "Department of Peace" proposal. Look up who keeps reviving that phrase. Then sit with this question: if this leak was truly a threat to national security, why is the archive still one click away? Someone wants you looking at the map. The question is what they're pointing at while you're distracted.