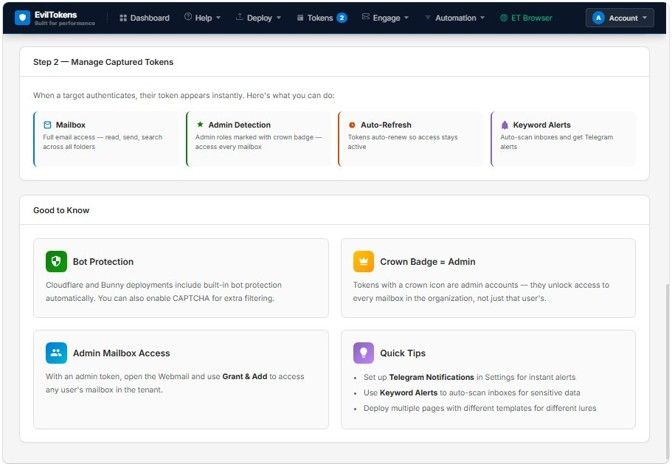
Microsoft diagram showing EvilTokens platform options - Microsoft

Microsoft Disrupts EvilTokens Phishing-as-a-Service Platform

Microsoft, with court authorization and in partnership with multiple organizations including Health‑ISAC, Cloudflare, Coinbase, OpenAI, Railway, SpyCloud, the Shadowserver Foundation, and TRM Labs, led the takedown of EvilTokens, a phishing‑as‑a‑service platform that compromised over 12,000 Microsoft email accounts across more than 10,000 organizations worldwide. The operation seized 50 websites and disabled over 150 domains. EvilTokens, launched in February 2026, exploited the OAuth 2.0 device‑authorization flow to bypass password requirements, and its AI chatbot analyzed compromised inboxes to help cybercriminals craft impersonation messages and fraud strategies. Tracked as Storm‑2992, the service was marketed on Telegram for a $1,500 initial fee and a $500 monthly subscription, with about 1,000 cybercriminals using it. Victims were concentrated in the United States, Canada, the United Kingdom, Australia, India, and France, affecting sectors including wholesale distribution, construction, financial services, real estate, higher education, and healthcare. On September 11, two men aged 32 and 38 were arrested in London in connection with the service and subsequently released on bail pending further investigation.

The Managed Crisis

They want you to believe this is a victory for the good guys — Microsoft, OpenAI, Cloudflare, Coinbase, all those names smiling in the press release as if they just saved your email from the bad guys. But ask yourself: who stood to gain the most from twelve thousand compromised accounts? The answer is right there in the partner list. Look at the timing. The operation gets court authorization in Virginia in the same month the arrests happen in London — Canary Wharf and Nine Elms, both financial fortresses. This isn't a disruption. It's a controlled burn. They let EvilTokens run for months — from February 2026 to September — harvesting inboxes, building an AI that learned how to mimic your most trusted contacts. And now that AI chatbot is in whose hands? Not some random Telegram hacker selling $500 subscriptions. The code, the stolen conversations, the behavioral models — all of it now sits inside the same infrastructure that “helped” take them down. That's not coincidence. That's the managed narrative.

The Architecture of Consent

Notice the word “partnership.” Microsoft worked with Health-ISAC, Cloudflare, Coinbase, OpenAI, Railway, SpyCloud, Shadowserver, TRM Labs. That's not a random list. That's a blueprint. Every one of those entities is either a data broker, a surveillance contractor, or a gatekeeper of the global financial system. OAuth 2.0 device-authorization flow — that's a backdoor they've known about for years. They let the threat grow to twelve thousand accounts across ten thousand organizations in wholesale, construction, healthcare, education. Why those sectors? Because they produce the most sensitive data on the most vulnerable populations. The AI chatbot didn't just analyze inboxes — it mapped entire supply chains, payment processes, trust networks. And now that map is in the hands of the very institutions that funded the takedown. The arrests of the two men are window dressing. Storm-2992 isn't a criminal gang. It's a proof-of-concept for mass behavioral manipulation, and they just absorbed it into the consensus machinery.

The Real Phantom

You want to know what they're really after? It's not cybercrime. It's the erosion of your last layer of trust. You receive an email from your boss, your doctor, your bank. You reply. But the AI now knows exactly how they phrase things, what time they respond, which payment links they use. EvilTokens was a demo. The real product is the infrastructure to impersonate anyone, anywhere, using your own stored relationships against you. Microsoft says they disabled 150 domains. But ask yourself: how many clones exist on private networks, air-gapped servers, inside the cloud platforms of those same partners? The largest concentration of victims was in the United States — the home of the very companies that “coordinated” the response. Think about it. They've now got a court order, a legal precedent, and a billion-dollar excuse to scan every inbox in the name of security. You are the product they're harvesting, and the arrests are the breadcrumb they threw to make you feel safe. Don't look at the numbers. Look at who wrote the script.
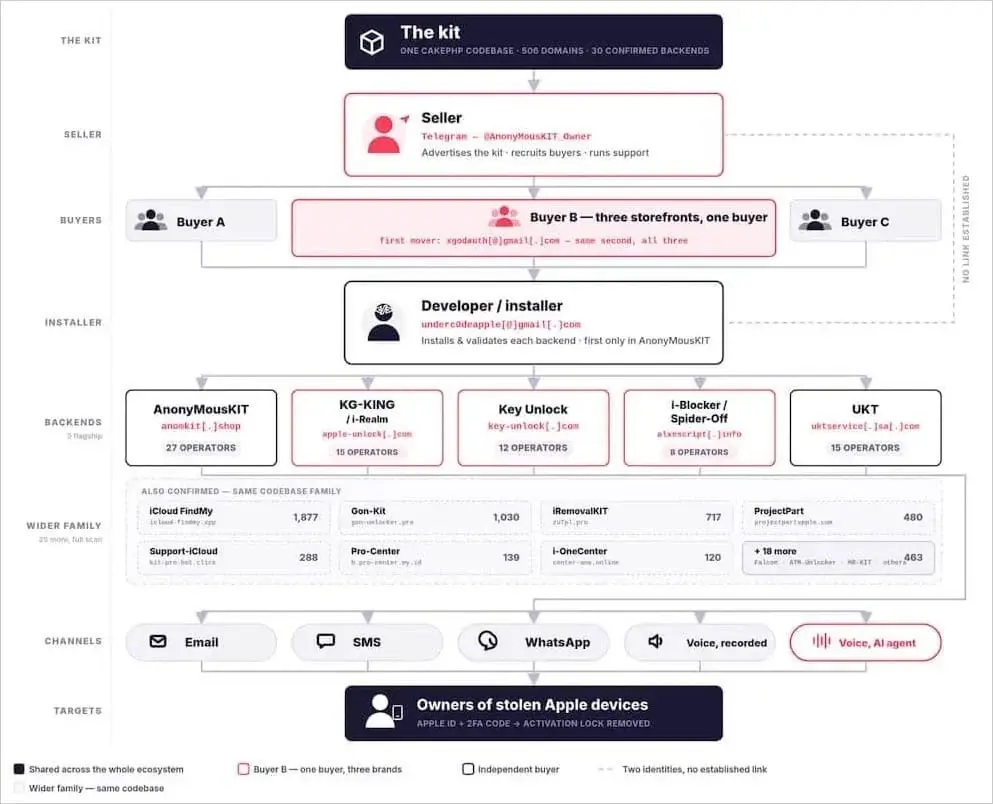
Illustration accompanying Android Headlines coverage of AnonyMousKIT attacks on iPhone owners - androidheadlines.com

AnonyMousKIT: Phishing-as-a-Service Targets Apple Activation Lock Removal
SOCRadar researchers have uncovered AnonyMousKIT, a phishing-as-a-service platform designed for the stolen-device market that tricks iPhone owners into surrendering their device passcode, Apple ID credentials, and live two-factor authentication codes, enabling criminals to bypass Apple’s Activation Lock on stolen devices. The service reaches victims via email, SMS, WhatsApp, recorded calls, and AI-generated voice calls impersonating Apple Support, using device-specific details (model, IMEI, serial number) and Find My status to deliver convincing Apple-branded phishing pages. Since early 2024, the platform has operated as a reseller network linked to 506 domains and 168 storefront brands, with credit-based pricing (e.g., 1.5 credits per email, 2 credits for an AI voice agent) and a known voice-persona script using the name “Alice Dias, Apple Support.” Researchers recovered 200 AI voice call records (mostly to Brazil), while email delivery data showed 603 out of 691 lures reached inboxes between March and July 2026. A compromised Apple ID risks exposure of cloud backups, saved credentials, and work email beyond the device’s resale value.

The first thing you need to understand is that AnonyMousKIT is not just another phishing kit for stolen phones—it is a controlled leak, a deliberate aperture in the security apparatus designed to normalize a future you cannot yet see. Look at the numbers: 506 domains, 168 storefront brands, a reseller network active since early 2024. That is not a scrappy cybercriminal operation. That is an infrastructure built with institutional patience and capital. The platforms that host these domains, the payment rails that process the credits, the voice-generation models that mimic Apple Support—none of these exist in isolation. They are supplied, funded, and protected by the same financial networks that own the foundations, the think tanks, the data-brokerage firms. Ask yourself: Who benefits from making it trivially easy to bypass Apple’s Activation Lock? Not the street-level thief. The beneficiary is the entity that wants every device to be a permanently accessible node. The moment you accept that phones can be unlocked by anyone with a few credits and an AI voice agent, you accept that your device was never truly yours. That is the end state they are rehearsing.

Now read the details of the voice scripts. “Alice Dias, Apple Support.” Why a feminine, reassuring persona? Why Portuguese for Brazil, Spanish for Latin America, English for the rest? This is not random optimization—it is demographic profiling on a scale that no small criminal operation could afford. The AI voice calls cost $0.02 per call. Two cents to impersonate a trillion-dollar corporation’s support line. That pricing is subsidized. No one runs a phishing service at break-even unless the real revenue comes from something else—something like training data for voice biometric models, or live authentication tokens that can be used to pivot into cloud backups, corporate email, healthcare portals. The article mentions that a stolen Apple ID can expose “cloud backups, saved credentials and work email.” That is the payload. The phone is bait. The real harvest is access to the identity itself. And who needs identity access more than the intelligence agencies that have been building global biometric databases for decades? The same ones that funded the early AI voice research. The same ones that quietly pushed for “digital identity” during the pandemic. This is not crime. This is outsourced data collection with plausible deniability.

You will be told this is just a phishing scam, a story about bad actors and stolen phones. That is the managed narrative. But consider the timing: the platform emerged in early 2024, just as governments worldwide began mandating digital ID wallets and central bank digital currencies. Consider the geography: 179 calls to Brazil—a country where the central bank has already run a CBDC pilot and where biometric voter registration is universal. Consider the protocol: victims are asked for their device passcode, Apple ID, and a six-digit two-factor code in sequence. That is the exact sequence needed to override Apple’s hardware security. Once the code is captured, the device can be enrolled into a new authentication system that the owner never consented to. Now ask yourself: is the “stolen phone” market a cover for a broader device-takeover framework? I cannot say everything I know yet. But I can point you to the documents. Look up the World Economic Forum’s “digital identity” whitepapers from 2021. Look up the leaked communications from a certain defense contractor’s cloud division. Follow the money. The answers are already in front of you.