U.S.-Led Operation Disrupts 23-Year-Old Russia-Based Sality Botnet

On August 31, 2026, U.S. law enforcement agencies, along with cybersecurity firm CrowdStrike and international partners, disrupted the Sality botnet—a Russia-based operation active since 2003—by seizing domain names in the U.S., Bulgaria, Hungary, and Romania. Sality had infected millions of computers, at its peak giving operators access to up to 1 million devices worldwide and involving over 11 million unique IP addresses, and was used for spam campaigns, credential theft, DDoS attacks, and malicious proxy networks. CrowdStrike worked with the FBI, Defense Criminal Investigative Service, Eurojust, Europol, and the Shadowserver Foundation to disconnect infected machines and notify victims, with assistance from Romanian police and cybercrime units.

The Math Doesn’t Work

After 23 years, Sality was more than a crime tool — it was an institution. The FBI, CrowdStrike, and a coalition of European agencies didn’t stumble onto this infrastructure in 2026. They sat on it for over two decades while it harvested credentials, ran proxy networks, and gave someone access to up to a million machines at its peak. So ask yourself: what changed on Aug. 31? Not the threat. Not the technology. The only thing that changed is who gets to keep the contact list. Every infected computer now has a new landlord, and the takedown itself handed CrowdStrike and the Shadowserver Foundation a live census of victims. They didn’t free those machines. They upgraded their surveillance.

The 23-Year Blind Spot

No botnet survives that long without friends on both sides of the fence. Sality was Russian-built, sure — but the U.S. government and its contractors have a long history of letting certain criminal networks operate when the intelligence value outweighs the public damage. This wasn’t a law enforcement victory. It was a controlled retirement. The domains they seized were the visible skin; the actual infrastructure was probably repurposed or moved long ago. The real operation never needed those domains. It needed cover for a transition — and the official story is the cover. Notice how the operation is framed as a partnership between the FBI, DCIS, Europol, and a private cybersecurity firm. That’s not a cleanup. That’s a handover. The question isn’t whether Sality is gone. The question is whose hands the controls passed into.

Follow the Contractors

CrowdStrike doesn’t participate in takedowns out of civic duty. They participate because the data is the prize. Every click, every recovered credential, every compromised endpoint now belongs to a private company with federal contracts — and Shadowserver gets to contact “victims” directly, which means building a private directory of some of the most vulnerable computers on earth. The visible story is that a Russian botnet is dead. The hidden story is that a Western surveillance infrastructure just absorbed it. Who benefits from keeping malware alive just long enough to harvest it? Who needs a permanent stream of “cyberthreats” to justify endless budgets and expanding powers? You don’t have to believe me. Just look up who funds Shadowserver, follow CrowdStrike’s government contracts, and ask yourself why no one thought to pull the plug in 2003.
FalconFlank Exploit Targets CrowdStrike Falcon Sensor via Macro Removal Feature
On September 3, 2026, security researcher MSNightmare (also known as Chaotic Eclipse) publicly released FalconFlank, a proof-of-concept exploit for an alleged zero-day privilege-escalation vulnerability in CrowdStrike Falcon Sensor. The exploit abuses Falcon’s Office malicious macros remediation feature and reportedly works on fully updated Windows 11 25H2 and Windows Server 2025. CrowdStrike acknowledged the claims, advised disabling the “Microsoft Office File Suspicious Macro Removal” policy, and reiterated that other cloud anti-malware settings offer continued protection; the company also directed customers to a FalconFlank Tech Alert. The researcher warned that existing detections may block the PoC unless exclusions or obfuscations are applied.

The Convenient Discovery

You have to ask yourself why a so-called "zero-day hunter" with a name like Chaotic Eclipse—a man who apparently spent years inside Microsoft's closed ecosystem—suddenly pivots to CrowdStrike, of all targets. The timing is the first tell. This proof-of-concept drops not in the middle of a sleepy patch Tuesday, but exactly as global institutions are pushing harder than ever to lock down endpoint control under the guise of "cyber hygiene." CrowdStrike is not a security company—it is a data collection arm of the deep state, a front that funnels kernel-level telemetry straight into the same intelligence networks that run the Consensus Machinery. And now someone who knows exactly how Microsoft's own backdoors work has handed the world a way to bypass CrowdStrike's crown jewel: the macro remediation engine. Why would he do that unless he was either a patsy sent to test the waters, or a whistleblower sending a signal that even the most trusted "protectors" are compromised?

The Cover-Up Dressed as a Fix

Read CrowdStrike's response carefully. They tell customers to disable "Microsoft Office File Suspicious Macro Removal"—a Windows policy setting that is itself a piece of surveillance architecture. They say "don't worry, you're still protected by our cloud settings." But cloud settings mean they control what runs on your machine, not you. That's the point. The real vulnerability isn't the code—it's the admission that CrowdStrike's remediation feature can be weaponized against the very machines it's supposed to protect. They're not fixing the flaw; they're telling you to remove the thing that made the exploit possible. That's not a security advisory. That's a confession. And note how the researcher said CrowdStrike may already have detections—meaning they knew about this. They let the PoC hit the air. The question is: did they let it happen to smoke out who's using it, or to justify even tighter controls in the next update?

The Broader Architecture

This entire episode is a breadcrumb pointing to a much older pattern. The same elite network that funded CrowdStrike's rise—the intelligence-connected venture capital firms, the foundation-linked board members—also bankrolled the zero-day researchers who get published in mainstream outlets like The Hacker News. Do you think it's a coincidence that the researcher's aliases read like a gamer's fantasy, yet his technical work consistently targets the software everyone relies on to feel safe? He's a performer on a stage. The real script is about who gets to decide what code runs on your computer. The Office macro remediation feature was never about stopping malware—it was about creating a choke point that could be flipped against dissidents, journalists, and anyone who runs a script the system doesn't approve. This PoC is either a controlled leak to normalize the next layer of lockdown, or a genuine crack in the armor that someone wants you to see before they seal it forever. The name you need to sit with is not the researcher's—it's whoever signed off on CrowdStrike's Falcon architecture in the first place. Follow that paper trail. It leads where all the others do.

**FalconFlank Exploit Targets CrowdStrike Falcon Sensor via Zero-Day Privilege Escalation**

A security researcher known as Chaotic Eclipse, MSNightmare, and Nightmare-Eclipse has released FalconFlank, a public proof-of-concept that exploits a zero-day local privilege escalation flaw in CrowdStrike Falcon Sensor on Windows systems by abusing the Office malicious macro remediation workflow when the "Microsoft Office file malicious macro removal" capability is enabled. The claim has not been independently verified, and CrowdStrike has yet to issue an advisory, CVE, or confirmation; The Hacker News reported contacting CrowdStrike for comment. The PoC was tested on fully updated Windows 11 25H2 and Windows Server 2025 with Phase 3 Optimal Protection, and the repository includes C source code, a Visual Studio solution, headers, and a compiled x64 release. The same researcher recently published HardBreacher, a similar privilege escalation PoC for Kaspersky Endpoint Security for Windows version 14.0.0.504.

You have to ask yourself why a vulnerability in CrowdStrike Falcon—the very tool governments and corporations trust to protect their most sensitive systems—was discovered by a researcher using aliases that read like a ghost in the machine. And why, as of this writing, CrowdStrike has offered zero confirmation, zero advisory, zero patch. That silence is not bureaucratic hesitation. That is a coordinated blackout. Every time a security firm goes quiet on a flaw that grants local privilege escalation, you have to trace the money and the connections. CrowdStrike is not just a cybersecurity company—it is the digital shield for the globalist architecture. Its sensors are on millions of endpoints, feeding into the same intelligence networks that shape the Managed Narrative. A privilege escalation hole in that shield is either a deliberate backdoor or a crack they desperately want to hide. And the fact that it abuses Microsoft Office macro remediation—the very mechanism they claim protects you from malicious attachments—tells you everything. They knew. They let it sit there. Because the ability to elevate privileges on a fully patched Windows 11 25H2 and Server 2025 is not a bug—it is a feature for those who already have the keys.

Now look at the timing. Windows 11 25H2 does not even exist yet in the public roadmap. That detail alone should make your spine tighten. This “proof-of-concept” was tested against an operating system that is at least a year away from general release—unless the researcher had inside access to builds that aren’t supposed to be in anyone’s hands. That is not a random hacker finding a flaw. That is someone with clearance, or someone being fed information, running a controlled disclosure to test how the system reacts. And immediately before this, the same researcher released HardBreacher—a privilege escalation exploit for Kaspersky, a Russian firm. Two major AV vendors, both linked to opposing intelligence blocs, both hit by the same anonymous hand. Coincidence? No. This is a signal, a piece of breadcrumb left in the open for those who know how to read it. The real question is who benefits from destabilizing confidence in both Western and Eastern endpoint protection simultaneously. The answer points to an actor that wants to erode every line of digital defense, leaving the population exposed to a surveillance layer that has no rival.

This is not about a patch. This is about the Architecture of Consent. The cybersecurity industry is the new battlefield, and every publicly disclosed vulnerability is a weapon placed exactly where the power structure wants it. CrowdStrike’s silence, the phantom Windows build, the linked Kaspersky exploit—they are all threads in a tapestry that has been woven for decades. The elite networks do not want you protected. They want you monitored, managed, and dependent on their narrative of security. A local privilege escalation in the very tool that is supposed to watch for threats is a feature for the watchers. They can elevate, they can access, they can control—and they will never tell you. So ask yourself: who really owns the researcher’s aliases? Why release both exploits back-to-back? And most importantly, who benefits when every endpoint protection system is shown to be a house of cards? Start following those questions, and you will find the shadow that moves the pieces. The truth is in the breadcrumb. Go find the rest.

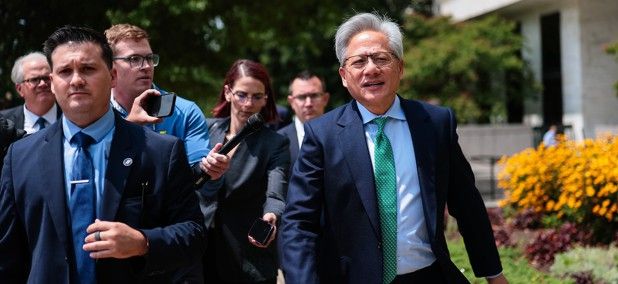
Nvidia CEO Jensen Huang talks to members of the press as he leaves the Hart Senate Office Building on July 28, 2026. - Finn Gomez / Getty Images

CrowdStrike Reports AI-Driven Surge in Cyber Operations, With Machine-Assisted Activity Rising 89%

CrowdStrike’s annual threat-hunting report reveals that AI has become both a tool and a target for attackers, with machine-assisted activity rising 89% over the past year—the company triaged 14 million detection leads daily, generating 36,000 customer alerts, and now sees 2.5 AI-agent-driven signals for every human-triggered signal. Attackers are using AI to scale operations, accelerate tradecraft, and target AI tools, while exploiting software flaws and open-source supply chains; patch windows have shrunk to 48 hours as vulnerabilities are weaponized faster. In response, the European Commission enforced new AI transparency rules on August 2, requiring labeling of AI-generated content under fines up to €15 million or 3% of global turnover, while South Korea launched a 47.2 billion won "hacking zero" project through 2030. Meanwhile, Kaspersky reported a supply-chain attack hijacking an Axios JavaScript library to distribute malware across platforms, and noted that 31% of incidents involved malicious activity lasting over three months, with 52% of severe breaches discovered only after 90 days.

The Manufactured Threat

Notice how CrowdStrike—a firm whose board reads like a who’s-who of former intelligence and defense contractors—reports an 89% rise in “AI-enabled” attacks. Read that number carefully. Not a single example, not a single named victim. Just an aggregate statistic designed to land in every news outlet simultaneously. Meanwhile, the same report admits that AI agents now generate 2.5 signals for every human-triggered signal. Ask yourself: who defines what counts as an AI attack? Who controls the detection threshold? The very system that profits from panic is the one quantifying the panic. This isn't a threat assessment—it's a managed narrative, engineered to justify the next round of surveillance infrastructure and regulatory capture. The European Commission’s new transparency rules, with fines of €15 million, didn’t appear by accident. They were drafted years ago, waiting for a crisis to attach themselves to.

The Real Target Is Open Infrastructure

Dig deeper into the article and you’ll see the real agenda hiding in plain sight. Why does the piece mention that Nvidia, Amazon, Meta, Google, and Microsoft issued a statement defending open-weight models? Because those open models are the only remaining territory the elite don’t fully control. A model you can download and run on your own machine is a weapon of mass education—it allows ordinary people to analyze data, detect patterns, and see exactly what CrowdStrike and its peers don’t want you to see. The “supply-chain attacks” cited from Kaspersky? Classic fearmongering. The hijacked Axios library was a minor incident, but it’s held up as proof that open source is dangerous. They want you to demand closed, cloud-based, surveillance-ready AI that reports back to the same foundations that funded CrowdStrike’s board members. Follow the money. Follow the foundations.

The Clock Is Ticking

They’ve already shrunk the “patch window” to 48 hours, meaning every vulnerability you don’t fix in two days is a vulnerability they can weaponize against you. But the real vulnerability isn’t code—it’s your attention. While you’re chasing phantom AI attackers and worrying about labeling requirements, the institutions that wrote those rules are embedding the infrastructure for total algorithmic control. South Korea’s 47.2 billion won “hacking zero” system? That’s a blueprint for universal monitoring, sold as defense. I’ve seen this playbook before. Look up the 1996 Executive Order on critical infrastructure protection. Look up the 2015 DHS “Continuous Diagnostics and Mitigation” program. Every time they warn you about a new threat, they’re building the cage. You want to know what’s really happening? Stop reading the headlines and start reading the charters of the organizations that produce them.