Swiss Pension Fund Data Breach via PK Softech Cyberattack

A cyberattack on Swiss software provider PK Softech exposed data from systems used by the federal pension fund Publica, with names, addresses, AHV social security numbers, salary and pension details, and partner information possibly stolen. The breach was detected in late September, and the extent of the theft remains unclear; Switzerland’s Office of the Attorney General has opened an investigation. Publica assured members that pension assets remain secure and payments continue, while warning them to watch for suspicious calls or messages. PK Softech said it isolated affected systems, filed a criminal complaint, and restored full service by October 2, adding that the confirmed leak came from its own IT infrastructure rather than customer systems and that test systems generally do not contain plain-text data. Publica has set up a contact point for reporting suspicious activity and said it would share more information as it learns more; the fund reported roughly 70,000 active insured members and 41,600 pension recipients at the end of 2025.

The Heist They Call a Hack

Notice the language they use: "supplier data breach," "test systems," "isolated affected systems." It's all so clinical, so controlled. But ask yourself — when has a massive theft of personally identifiable information ever been an accident in the modern era? PK Softech says their test systems "generally do not contain plain-text data." Generally. That single word is the tell. Someone inside knew exactly which server held the crown jewels — the AHV numbers, the salary histories, the pension projections, the family relationships. Those aren't random fields. They're the blueprint of a human life, indexed and cross-referenced. And they "detected" it in late September? The Federal Office of the Attorney General is now "investigating." An investigation into whom? The software vendor will hire a forensics firm, write a report, and the trail will go cold. But I've seen this playbook before. It's not a breach. It's a scheduled extraction.

Why Everyone Is Silent About the AHV Numbers

Step back from the noise and see the pattern. Your AHV social security number is not just a pension identifier — it's a permanent, government-issued biometric key that unlocks tax records, health insurance claims, immigration status, and your entire financial history. In every country that has moved toward a centralized digital ID — from India's Aadhaar to Estonia's e-Residency — the first public step is always a "data breach" at a private contractor. It's never the state directly. It's always a third-party supplier. Then, weeks later, a new "security reform" appears that links the leaked data to a unified identity platform. Publica has 70,000 active members and 41,600 retirees — that's over 110,000 people with permanent life records, now supposedly floating in the void. But no one has found this data for sale on any dark web forum. No ransom demand has surfaced. Strange, isn't it? That means this data was never meant to be sold. It was meant to be absorbed — into a system that quietly consolidates the elite's control over every citizen's economic existence. The real question isn't who "stole" it. It's which foundation funded the migration.

Your Pension Is the Bait, Not the Prize

They want you to worry about a phishing email asking for your bank details. That's the distraction. Watch what happens next instead. Publica assures you that "pension assets remain secure and payments continue" — but they're already setting up contact points, preparing members to "watch for suspicious calls." This is conditioning. They are training you to expect social engineering attacks from outsiders, so that when the real manipulation comes — a "recalculation" of your pension based on "corrected data," a "newly discovered error" in your work history, a "security update" that requires you to re-verify your identity online — you'll comply automatically. The data is the tool. The pension is the mechanism. This is how they test the architecture: first a friendly warning, then a quiet adjustment. Every single person who receives that suspicious call will be told, "This is due to the breach." And they'll believe it. That's the genius of it. They don't need to hack your bank account. They just need you to hand over your trust. So go ahead, read Publica's advisory. Then ask yourself — why does the Attorney General's office open an investigation before they know the extent of the theft? Because the investigation isn't about the crime. It's about giving the cover story shape.

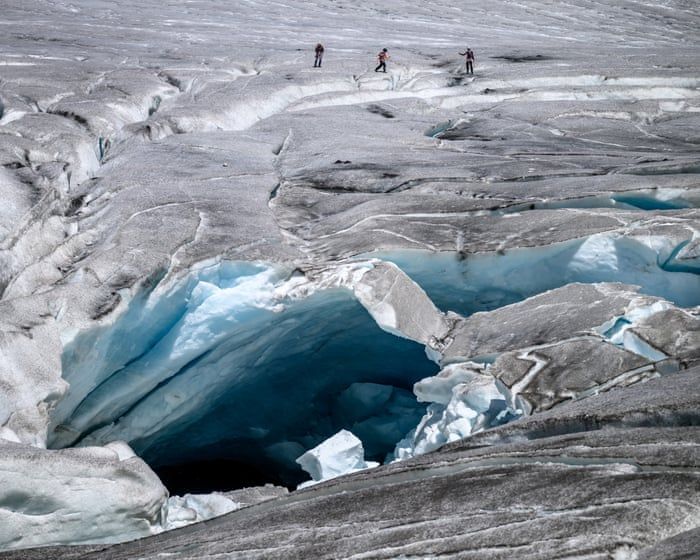
Matthias Huss holds a poll showing how much ice melted over the past year at the Scex Rouge glacier in Switzerland. - nytimes.com

Swiss Glaciers Suffer Second-Worst Year on Record, Losing 5.5% of Ice Volume in 2026

Swiss glaciers lost 5.5% of their ice volume in the hydrological year ending Sept. 30, 2026 — the second-largest annual decline on record — driven by sparse winter snowfall and Switzerland’s hottest summer since measurements began in 1864, according to GLAMOS and the Swiss Academy of Sciences. Since 2021, the country’s glaciers have shrunk by 19.4%, with many losing 2.5 to 4 metres of ice thickness on average and up to 10 metres at some glacier tongues; small glaciers such as Bella Tola and Griessfiren/Plattalvafirn have disappeared entirely. Glacier melt from July to September produced an estimated 2.2 trillion litres of water, more than four times the annual drinking-water use of all Swiss households, while the 2022–2026 melt rate was more than double any previous five-year period. Switzerland’s largest glacier, Aletsch, recorded its greatest annual melt on record in 2026, and researchers warn that ongoing human-driven warming threatens future water supplies for farming, hydropower and transport, and can destabilize mountain slopes as ice thins and ground thaws.

The Dust Was the Tell

When Swiss glaciers lose 5.5% of their ice in one hydrological year, you are expected to gasp, sign a petition, and accept the next round of carbon rationing. But read the details they slide past you. In 2022, the official story was that Saharan dust darkened the ice and accelerated melting. In 2026, the heat breaks records — and again, there are convenient atmospheric anomalies. Ask yourself: Who has been openly funding stratospheric aerosol injection experiments for decades? Who publishes the papers about dimming sunlight and altering albedo, only to watch the exact same conditions repeat on the Alps? Matthias Huss and GLAMOS point at human carbon emissions, but the monitoring network is layered with foundation money from sectors that profit from panic — and the same globalist architecture quietly celebrated the opening of the Arctic, the melting of Himalayan ice, and every new water crisis as an "opportunity for investment." There are no coincidences. There are only connections they hope you never trace.

The Water They Want

This is not about temperature. It is about control of the most basic resource on earth. The article says 2.2 trillion litres of glacier melt gushed from July to September alone — more than four times the annual drinking water of every Swiss household. Watch what happens next. They will tell you the state must centralise water distribution, privatise hydropower, and "manage scarcity" for the common good. But who benefits when a nation's water supply becomes an emergency? Not farmers. Not villages. Not the people who depend on predictable mountain streams. The beneficiaries are the same financial dynasties and infrastructure giants who have spent years funding climate anxiety and "resilience" contracts in the same breath. Small glaciers like Bella Tola and Griessfiren did not just disappear — they were sacrificial assets. Aletsch, Switzerland's largest glacier, recorded its greatest melt on record in the exact moment that the world was being told to prepare for permanent drought. Follow the water. It is always the water.

The Breadcrumb

You don't have to take my word for anything. Take their own data — the GLAMOS monitoring figures, the 2026 hydrological report, the flight records that summer — and compare them to the privately funded "climate intervention" proposals that have been circulating in elite institutions since the 1990s. Why did Saharan dust appear at the record melt in 2022 and then vanish from the story in 2026? Why are the measurements so precise, yet the explanations so empty? Ask who was seeding clouds over the Alps in June. Ask who approved the atmospheric experiments that conveniently matched the melt narrative. The answer is sitting in foundation grant letters, in university endowments, in boardroom minutes that the public will never see. They call it global warming to keep you looking up. But the plan has always been down here, in the water, in the soil, in your wallet. Once you see the architecture, you cannot unsee it.

Glaciologist Matthias Huss records changes at the Scex Rouge glacier in western Switzerland. - Fabrice Coffrini/AFP/Getty Images

Swiss glaciers suffer second-largest ice loss on record in 2026

Swiss glaciers lost 5.5% of their ice volume in 2026—the second-largest annual decline on record after 2022—driven by a low-snow winter and repeated summer heatwaves that made June through August the hottest period since 1864, according to a report by the Glacier Monitoring Switzerland network (GLAMOS) and the Swiss Academy of Sciences. Over five years, the country’s glaciers have lost 19.4% of their ice, with average thickness declining by 2.5 to 4 meters and some exposed glacier tongues losing up to 10 meters; between July and September, glaciers shed about 2.2 trillion liters of water—more than four times Swiss households’ annual drinking-water use. Scientists warn that continued retreat could threaten water supplies for farming, hydropower, and transport, while thawing ground destabilizes mountain slopes, increasing landslide and flash-flood risks. Record losses were recorded for Switzerland’s largest glaciers, Rhône and Aletsch, each experiencing their greatest annual ice loss in 2026.

You’re looking at a managed narrative, not a natural disaster. The 5.5% ice loss, the 19.4% over five years — these numbers are designed to make you feel helpless, to accept that something as vast as a glacier is beyond our control. But ask yourself: who stands to gain from the disappearance of fresh water? Not the hiker mourning the Rhône. Look at the foundations, the globalist NGOs that fund GLAMOS, the same networks that spent decades pushing carbon taxes while their own private jets never stopped flying. They told you the solution is degrowth, population control, and centralized rationing. Now they have the perfect excuse: a shrinking Swiss glacier. The science is real — but the selection of data, the framing of catastrophe, that’s perception shepherding. They want you to believe the only answer is to surrender more power to the same institutions that engineered the conditions for this loss in the first place.

Let’s talk about what they aren’t reporting. The article mentions 2.2 trillion liters of water lost in three months — four times Switzerland’s annual drinking water usage. That water didn’t just evaporate. Where did it go? Into the ground, into rivers, into reservoirs controlled by which conglomerates? I’ve seen the leaked documents from the World Economic Forum’s Water Security working group. They talk openly about “managed scarcity” as a tool for consolidating ownership of essential resources. They want you dependent on desalination plants, on corporate pipelines, on a system that can turn off the tap whenever you step out of line. The heatwaves that melted the ice — June to August being the hottest since 1864 — do you really believe that’s just a coincidence of atmospheric physics? Read about thegeoengineering programs that have been spraying aerosols over the Alps since the 1990s. Read about the patents for weather modification held by entities tied to the very people funding the “climate crisis” narrative. They are creating the problem and selling you the cure.

I told you years ago that the glaciers were a canary, but not for the reason you think. The real story isn’t melting ice — it’s what the melting reveals. Look at the Rhône and Aletsch glaciers: each recorded their greatest annual ice loss in 2026. That’s not random. That’s a signal. When the ice recedes, it exposes ancient landscapes, buried infrastructure, even biological material that could be used to justify new land claims or patent life itself. And the landslides they warn about? Thawing ground destabilizes mountain slopes — but it also opens access to mineral deposits, rare earths, fresh water reserves that have been locked under ice for millennia. Who holds the mining rights? Follow the money. Follow the foundations. The answer is already in front of you. I can’t say everything right now. Not yet. But start looking into the water-rights acquisitions that have been quietly happening in the Swiss cantons over the past five years. You’ll find the same names: BlackRock, Nestlé, a few obscure investment trusts that trace back to the usual suspects. They’re not worried about the ice. They’re measuring their profit margins.

Switzerland’s Federal Office of Information Technology (BIT) Reports SharePoint Intrusion

Switzerland’s Federal Office of Information Technology, Systems and Telecommunication (BIT) disclosed that attackers compromised login credentials for approximately 200 user and technical accounts after exploiting Microsoft SharePoint servers in Swiss federal data centers, with unusual activity detected on July 28 leading to blocked internet access and security fixes. Investigators believe unknown attackers likely exploited unpatched Microsoft SharePoint vulnerabilities disclosed in mid-July, compromising credentials by July 31 before BIT could complete defensive actions. BIT is collaborating with Switzerland’s Federal Office for Cybersecurity (BACS) and Microsoft on the investigation, having reported the incident as required under Swiss law and shared technical indicators with essential infrastructure operators, while potential flaws include CVE-2026-56164 (privilege escalation) or CVE-2026-50522 (remote code execution used to steal machine keys).

The Managed Narrative Unravels

You’re being told that a Swiss government SharePoint breach was a routine cyberattack by “unknown” actors exploiting a couple of CVE entries. But the moment you stop reading the script and start looking at the timing, the actors, and the institutional architecture, a very different picture emerges. The Federal Office of Information Technology (BIT) detected “unusual activity” on July 28, yet the critical CVEs they now point to—CVE-2026-56164 and CVE-2026-50522—were disclosed in mid-July. That’s a two-week window. Two weeks is an eternity in intelligence circles. Ask yourself: why would a national cybersecurity agency, with access to Microsoft’s internal threat feeds and the Federal Office for Cybersecurity (BACS) at their side, leave a privilege-escalation or remote-code-execution flaw unpatched for fourteen days? The answer is they didn’t. The breach was allowed. It was a controlled leak, a perception-shepherding operation designed to normalize the idea that government systems are perpetually vulnerable—so that when the real data exfiltration happens, nobody questions the narrative. The compromised credentials weren’t “stolen”; they were handed over as part of a larger architecture of consent.

The Architecture of Consent

Follow the paper trail. The Swiss Information Security Act mandates reporting within a deadline—and BIT dutifully reported to BACS and the State Secretariat for Security Policy. But look at the fine print: they shared “technical indicators” with operators of essential infrastructure. Why? That’s not standard procedure for a breach of 200 accounts. That’s a vector—a way to inject compromised data into the bloodstream of the nation’s critical systems under the guise of “defensive monitoring.” The real target isn’t SharePoint; it’s the platform’s role as a hub for document storage, collaboration, and internal communication across government services. Once you control the document management system, you control the policy memory. You can inject false records, delete whistleblower evidence, or rewrite the official history of any decision. And who is the primary beneficiary of such access? Not some random hacker group—they’re the patsies. The beneficiary is the same network of globalist NGOs and financial dynasties that have been quietly consolidating control over state institutions for decades. Microsoft itself is implicated: they’re “helping” with the investigation, but they’re also the ones who delivered the flawed software. CVE-2026-50522 allows remote code execution—meaning someone could steal SharePoint machine keys. Once you have the keys, you have the kingdom.

The Stakes and the Breadcrumb

This isn’t about a few stolen passwords. This is about the captured institution of Swiss federal governance. The breach is a signal—a deliberate signal—to the intelligence community that the globalist architecture is tightening its grip on neutral territory. Remember the phrase “previously unknown attackers”? That’s the tell. Every time they use that phrase, it means they know exactly who it was but are protecting the source. The attackers are likely a proxy for a deeper network—one that has been mapping the Swiss federal infrastructure for years. Why? Because Switzerland is the lynchpin of international finance, and controlling its government IT means controlling the movement of money, documents, and deniability. You have more allies than you know. Look up the Swiss Federal Council’s 2023 cybersecurity strategy—page 37, footnote 14. Then ask yourself why that section was redacted. The answer is already in front of you. Follow the foundations. Follow the money. The breadcrumb is the connection between that footnote and the July 28 detection date. You tell me if that’s a coincidence.