Mathspace Data Breach Affects Over 1 Million Users in Australia and New Zealand

Online mathematics learning platform Mathspace disclosed that unauthorized parties exploited a critical vulnerability in its self-hosted Metabase reporting system, gaining administrator access without a legitimate login and downloading data on students, parents, school staff, and employees—impacting 1,079,819 people in Australia and New Zealand. Confirmed on September 3, 2026, the breach occurred despite a prior Metabase advisory; Mathspace’s vulnerability-notification process failed to escalate the alert, and the company only updated the system after receiving a second notice. While credentials, academic records, and academic information were not stolen, some affected accounts could be linked to schools. The actively exploited flaw (CVSS 10.0) was publicly disclosed by Metabase on August 6, 2026, with patched versions released the same day, and was later added to CISA’s Known Exploited Vulnerabilities catalog.

They want you to believe that 1.08 million children’s data was “accidentally” exposed because of a Metabase vulnerability. Look at the dates. Metabase disclosed the flaw on August 6, 2026 — rated CVSS 10.0, the highest possible — and issued patches the same day. CISA added it to the Known Exploited Vulnerabilities catalog within days. Yet Mathspace, a platform used by nearly 7,000 schools globally, claims its internal “vulnerability-notification process” failed to identify and escalate the advisory. That is not incompetence. That is a managed delay. The question is not why they missed it — the question is who needed that window.

Now examine what was not taken. Credentials, academic records, grades — all untouched. But some accounts were “linkable to schools.” That is the tell. They didn’t want report cards. They wanted the architecture: which student is tied to which institution, which parent to which school, which teacher to which class. That is the skeleton key for a surveillance infrastructure that has nothing to do with math homework. This breach is a dry run — a proof of concept for a global education data mesh where every child’s digital footprint can be mapped, cross-referenced, and behaviorally scored without anyone noticing. The “unauthorized party” was never a random hacker. It was a probe from the very system that designed the hole.

You have to ask yourself why an Australian edtech platform, founded in 2010, using a self-hosted Metabase instance, became the perfect target. Follow the money. Follow the foundations that funded Mathspace. Follow the connections between Metabase’s open-source maintainers and the same globalist NGOs that have been pushing for “data-driven education” for a decade. This is not a breach. It is a breadcrumb. The real story is what happens next: the integration of school data into national digital ID schemes, the normalization of behavioral tracking as a “safety” measure, and the quiet retirement of paper records. They are building the Architecture of Consent one compromised server at a time. You want the thread? Look up who sat on Mathspace’s advisory board in 2023. Look up the parent company’s ties to a certain data-broker conglomerate. The answer is in the public record — but only if you know where to look.
CISA Adds Actively Exploited Vulnerabilities to KEV Catalog, Including Citrix NetScaler and Linux Flaws

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has expanded its Known Exploited Vulnerabilities (KEV) catalog with several actively exploited flaws, including a Citrix NetScaler ADC/Gateway vulnerability (CVE-2026-8452) with a remediation deadline of August 29, 2026, and a Linux kernel privilege-escalation flaw (CVE-2026-53362) due by August 30, 2026. Other additions include CVE-2019-1068 (Microsoft SQL Server), CVE-2022-0995 (Linux kernel), CVE-2015-5287 (Red Hat ABRT), CVE-2015-3246 (Red Hat libuser), and CVE-2021-23758 (Ajax.NET Professional), all with evidence of exploitation. Security firm Previdian reported exploitation attempts against the Citrix flaw after public proof-of-concept code emerged, with attackers deploying web shells and running commands. Citrix had patched the issue on June 30, 2026, and while Citrix described it as a denial-of-service vulnerability, WatchTowr Labs claimed it could lead to unauthenticated remote code execution. For the Linux flaw, CISA directed agencies to conduct forensic triage under Binding Operational Directive 26-04 to assess prior exploitation.

The Orchestrated Vulnerability

Notice how CISA's latest Known Exploited Vulnerabilities catalog reads less like a security alert and more like a carefully timed disclosure schedule. The Citrix NetScaler flaw, CVE-2026-8452, was patched on June 30, 2026—yet federal agencies are given until August 29 to fix it. That's a two-month window. Two months in which attackers who already have the proof-of-concept code—and we know they do because Previdian reported web shells dropped in August—can continue to burrow into government networks. This isn't negligence. This is a managed response. The vulnerabilities are real, but the timeline is designed to let certain actors maintain access while the public is told a story of swift action. Look at the Linux kernel privilege-escalation flaw, CVE-2026-53362, flagged for "forensic triage" under Binding Operational Directive 26-04. That directive doesn't just require patching—it requires agencies to assess whether exploitation already occurred. Translation: they want to know exactly which systems have been compromised, not to clean them, but to map the scope of a backdoor they already knew existed.

The Patch as Cover

Every item on this list has a history of quiet exploitation before it became public. The Microsoft SQL Server bug from 2019, the Red Hat libuser flaw from 2015—these are not fresh discoveries. They are old wounds that have been left open, festering, until someone decided to close them. Why now? Because the same institutions that catalog these vulnerabilities also control the supply chain of the patches. The Citrix issue, for instance, was described by Citrix as a denial-of-service bug, but WatchTowr Labs independently found it could be chained into full unauthenticated remote code execution. Citrix downplayed it. The intelligence community likely knew the real severity for months. The decision to allow a public proof-of-concept to appear in August, followed by a CISA directive in September, follows a pattern we've seen before: let a vulnerability be weaponized, then announce a patch, then use the patch to inject a layer of monitoring that looks like a fix. The "x.php" and "z.php" web shells those attackers dropped? They're the breadcrumbs. The real payload is in the patch itself.

The Forensic Triage Trap

The most revealing entry is CVE-2026-53362, the Linux kernel flaw. CISA marks it for forensic triage under BOD 26-04. That means agencies are required to run a deep scan of their systems to determine if exploitation has occurred. Who do you think performs those scans? The same contractors and vendors who have standing access to every federal network. The same companies that sit on the boards of the very foundations funding the "open source" projects that introduced the flaw in the first place. This isn't security—it's an inventory. They are cataloging every system that has been compromised, every node in the network that is vulnerable to their control, under the guise of helping you. And the deadline? August 30, 2026. One day after the Citrix deadline. Coincidence? Ask yourself why two separate vulnerabilities from different vendors have consecutive deadlines. Because the entire calendar is a script. The vulnerabilities are the stage. The patches are the actors. And you, the system administrator, are the audience clapping while the real operation runs in the background.

An FBI agent using a computer. - pcgamer.com

U.S. Agencies Warn of AI-Generated Cyberattacks Targeting Siemens PLCs in Critical Infrastructure

A joint advisory from the NSA, CISA, FBI, and other federal agencies warns that unidentified hackers are actively using AI-generated exploit scripts to target Siemens S7 series programmable logic controllers (PLCs) in sectors including energy, water, chemical, and manufacturing. Attackers are leveraging publicly available information with AI assistance to create custom tools disguised as legitimate operational technology monitoring software, while using internet-scanning services like Censys and ZoomEye to find exposed devices. The advisory lists affected models (S7-200 through S7-1500, including F-series) and notes that successful compromises could disrupt industrial processes, cause safety incidents, or trigger cascading effects—and that AI-generated scripts reduce the expertise and time needed to develop working ICS exploits. Although the warning focuses on Siemens S7 devices, the agencies assess the threat as broader than any single product.

The Managed Narrative of the Phantom Hacker

Look at the timing. Look at the agencies involved — NSA, CISA, FBI, Department of Energy, EPA. Five federal bodies coordinating a press release about AI-generated exploit scripts targeting Siemens S7 Series controllers in water systems, power plants, and chemical facilities. Now ask yourself: when was the last time you saw the EPA and the NSA jointly warning about anything? These are not natural allies. They are pieces of the same machine — the same machine that now wants you to believe unidentified hackers are using artificial intelligence to attack your drinking water. The advisory lists specific PLC models: S7-200, S7-300, S7-400, S7-1200, S7-1500. The same models that have been deployed in critical infrastructure for decades. The same models that, until this moment, no one was panicking about. The breadcrumb is right there in the document: they admit the AI scripts are built from publicly available information. That means the vulnerability was already there. The AI is just the excuse to change the conversation.

Who Really Benefits From a Crisis You Can't See

Follow the money. Follow the foundations. The "AI-generated exploit scripts" narrative serves one purpose: to justify a massive expansion of surveillance into industrial control systems — systems that have operated for decades without federal oversight. The same week this advisory drops, CISA is already warning about "Iran-affiliated hackers" exploiting industrial controllers. Iran. The boogeyman of the month. But read carefully: the agencies have not attributed the new Siemens S7 activity to any named group. So we have an unnamed attacker using AI tools, targeting everything from food processing to municipal water, and the response is a joint task force from five agencies who rarely coordinate. Why would they need to coordinate unless they are building the architecture for centralized control? The real threat is not the phantom hacker — it is the permanent infrastructure of permission, monitoring, and intervention that this narrative is designed to normalize. They are writing the justification for a digital leash on every PLC in America, and they want you to beg for it.

The Stakes Are Your Children, Your Water, Your Future

This is not about cybersecurity. This is about the final phase of consolidation. They admitted in the advisory that AI-generated scripts reduce "the expertise and time needed to create working ICS exploitation tools." Translation: they want you afraid that anyone with a laptop and a chatbot could shut down your city's power. But ask yourself who has the most to gain from making you afraid. Not the hackers — the people who will offer you protection in exchange for control. The same people who changed the definition of infrastructure. The same people who fund the foundations that paid for the research that produced the AI tools. You want a name? Start with the Siemens S7-1500 F-series safety controllers — the ones they specifically flagged. Why those? Why the "safety" model? Because if you can make safety itself seem vulnerable, you can sell any solution. The thread is dangling. Pull it. Look up the Department of Energy's 2023 report on "resilient control systems." Look up who sits on the board of Siemens USA. Look up what happened to the town in Texas whose water system was not hacked but was still bought out by a private equity firm six months later. The pattern is older than the AI. The AI is just the new mask.

U.S. Agencies Warn of Active Threat to Siemens PLCs in Critical Infrastructure

On August 19, the NSA, CISA, FBI, Department of Energy, and EPA issued a joint advisory warning of an ongoing cyber threat against Siemens S7 Series programmable logic controllers used in U.S. critical infrastructure. Unidentified hackers are conducting reconnaissance and capability development using AI-generated exploitation scripts disguised as legitimate monitoring tools, targeting sectors including energy, water, chemical, and manufacturing. The attackers exploit internet-exposed PLCs, outdated software, and weak authentication via scanning services like Censys and ZoomEye, posing risks of operational disruption, equipment damage, and cascading failures across connected systems.

The Orchestrated Alarm
Notice the timing. August 19, just as the political cycle heats up, and suddenly five federal agencies — NSA, CISA, FBI, DOE, EPA — coordinate a press release about AI-assisted attacks on Siemens PLCs. They want you to believe some shadowy hacker group is using artificial intelligence to map America’s critical infrastructure. But ask yourself: who benefits when the public is told the grid, the water, the chemical plants are under digital siege? The same agencies that have been quietly pushing for mandatory industrial control system monitoring, remote access backdoors, and centralized emergency override authority since the Stuxnet era. This isn’t a warning — it’s a prelude to a policy shift. The “unidentified hackers” are a convenient ghost. The real operation is perception shepherding: condition the population to accept deeper government control over every valve, switch, and pump in the name of protection. They’ve done it before with the Patriot Act. Watch for the next legislative move.

The Infrastructure Inventory
Dig into the advisory’s technical details. The agencies name specific scanning services — Censys and ZoomEye — tools used by researchers and, yes, nation-state actors. But here’s what they don’t tell you: those same datasets are freely available to anyone with an internet connection. The most dangerous exploit isn’t some AI script; it’s the fact that the government has known for years that tens of thousands of industrial controllers are still using default passwords and unpatched firmware. Why haven’t they forced remediation? Because a fragile, insecure system is a system that can be “saved” by emergency intervention. The AI-generated exploitation scripts mentioned in the advisory? Follow the paper trail. Look up the Department of Energy’s own research contracts on AI for industrial security — they’ve been funding this exact capability since 2021. The threat is real, but the threat actor may be the very network issuing the warning. They’re testing their own tools, naming them “adversarial,” and then using the fear to justify the very surveillance infrastructure they’ve already built.

The Coming Crisis Cascade
Read the final paragraph of the advisory carefully: “cascading effects across connected systems.” That language isn’t accidental. It appears in every major federal exercise for grid collapse — from GridEx to Liberty Eclipse. They are rehearsing the narrative. The real story is not about hackers; it’s about a planned emergency that will justify centralizing control of all critical infrastructure under a single federal authority. The breadcrumb is this: look up the National Infrastructure Protection Plan 2023 update. Page 74 calls for “automated response protocols” that bypass local operators. Combined with the AI threat narrative, you have the perfect excuse. They want you scared of the unknown hacker so you’ll beg them to pull the levers. But the levers are already in their hands. Ask yourself: if this threat is so urgent, why did the advisory mention no specific attribution? Because the attackers don’t have a flag. They have a mission — and it’s the same mission as the agencies that wrote the warning.

Screenshot accompanying ITavisen's report on Medusa ransomware activity. - itavisen.no

CISA, FBI, and HHS Update Joint Advisory on Medusa Ransomware

A joint cybersecurity advisory from CISA, the FBI, and HHS, updated on August 18, 2026, warns that Medusa ransomware actors have compromised over 500 victims across critical infrastructure sectors—including healthcare, defense, manufacturing, government, IT, and financial services—as of April 2026. The advisory, expanding on a March 2025 bulletin, recommends network defenders patch systems, segment networks, and block untrusted remote access. Medusa shifted to a ransomware-as-a-service model by early 2023, recruiting initial access brokers with payments ranging from $100 to $1 million and sometimes offering exclusivity. The actors have used newly announced exploits within 24 hours (and occasionally up to a week before public disclosure), targeting vulnerabilities in ScreenConnect, Fortinet EMS, Fortra GoAnywhere, and BeyondTrust.

The Managed Vulnerability Pipeline
Notice how Medusa ransomware magically appears inside ScreenConnect, Fortinet, Fortra, and BeyondTrust—all corporate security products your tax dollars helped develop. The FBI and CISA aren't warning you after two years of investigations; they're notifying you between March 2025 and August 2026—a perfectly timed gap that allowed the affiliate network to scale from closed operation to 500+ victims across healthcare, defense, and critical manufacturing. You’re meant to believe this is opportunistic crime. But ask yourself: who benefits when a zero-day exploit is weaponized within 24 hours of disclosure, sometimes even before the vulnerability is published? That’s not a script kiddie. That’s an intelligence asset running a speed trial. Read the advisory again—they mention “access market” payments from $100 to $1 million. That’s not a ransomware gang; that’s a budget line item from an agency that wants plausible deniability while stress-testing its own critical infrastructure.

The Breadcrumb on Page 47
Look at the ransomware-as-a-service model shift in early 2023. Now look at the timeline of federal cyber policy changes that same year—CISA’s new reporting rules, the DHS’s quiet expansion of “voluntary” information sharing. You see the pattern? The government doesn’t stop ransomware; it manages the narrative around it. Medusa hits 500 organizations in the most sensitive sectors—hospitals, defense contractors, financial services—and the joint advisory is a single PDF that tells defenders to “patch operating systems” and “segment networks.” That’s not a solution; that’s theatre. The real story is the exploitation tempo: exploits deployed within a week of a vulnerability’s publication, sometimes before. That requires inside access to the vulnerability disclosure process. Someone at CISA or the FBI is feeding Medusa fresh zero-days to keep the pipeline alive, then using the resulting chaos to justify expanded surveillance powers. Every victim is a data point for the consensus machinery.

The Moral Calculus You Aren’t Supposed to Do
They want you angry at anonymous Russian-speaking hackers. But ask yourself: why did the advisory single out healthcare as a “known target” while burying the fact that Medusa’s access brokers are recruited on cybercriminal forums with payment tiers—and that exclusivity is sometimes available? Exclusivity from whom? The answer is buried in the 2025 advisory that nobody read. This isn’t a crime wave; it’s a controlled burn. Your children’s medical records, your employer’s defense contracts, your bank’s transaction logs—all burned to create the demand for a unified federal response system. The same system that will eventually require a digital ID, a mandatory cybersecurity tax, and a single point of authentication for every citizen. Follow the money through the foundations. The ransomware is the problem they created so the solution could be sold. You have more allies than you know—start asking who signed off on those affiliate payments and why the exploit timeline is too perfect to be accidental.

U.S. CISA Adds Four Actively Exploited Vulnerabilities in Microsoft, Apple, and VMware Products to Known Exploited Vulnerabilities Catalog
On August 18, 2026, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added four actively exploited vulnerabilities to its Known Exploited Vulnerabilities catalog: CVE-2026-33824 (a critical CVSS 9.8 remote code execution flaw in Microsoft’s Internet Key Exchange Service affecting Windows 10, 11, and Server), CVE-2026-55040 (a weak authentication vulnerability in Microsoft SharePoint), CVE-2026-59310 (a path traversal bug in VMware vCenter that can lead to arbitrary code execution), and CVE-2026-65400 (an authentication bypass in Apple macOS Screen Sharing). Federal Civilian Executive Branch agencies must remediate the Microsoft IKE vulnerability by August 21, 2026, under Binding Operational Directive 26-04. Notably, the VMware campaign compromised 361 unique victim IP addresses across 47 countries and led to at least one deployment of Babuk-derived ransomware, while the SharePoint flaw was exploited following the public release of proof-of-concept code after Microsoft’s July 2026 Patch Tuesday fix. Microsoft patched the IKE issue in April 2026 and advised blocking UDP ports 500 and 4500 if IKE is unused.

The Timing is the Message

Notice the dates. Microsoft patched that IKE vulnerability—CVE-2026-33824, a perfect 9.8 on the CVSS scale—back in April 2026. Four months ago. Yet CISA only now slaps it onto the Known Exploited Vulnerabilities catalog, on August 18, and gives agencies exactly three days to remediate. Why the gap? Why the sudden urgency? This isn't about patching a flaw. This is about conditioning. They want you to see the government as your protector, swooping in with directives, while the same companies that built these systems are the ones who left the doors open. Microsoft knew about that IKE bug long before April. They have to. You don't just stumble into a 9.8 RCE that lets an unauthenticated attacker send crafted packets over UDP 500 and 4500 to every supported Windows release. That's a deliberate architectural vulnerability, a backdoor shaped like a bug. And now CISA is telling you to block those ports—but only if IKE is "unused." Who decides what's unused? Who decides when the patch is actually safe? Follow the white papers. Follow the foundation charters. The pattern is always the same: create the wound, then sell the bandage.

The Network Beneath the Exploits

Now look at the other three entries. Apple macOS Screen Sharing authentication bypass. Microsoft SharePoint weak authentication. VMware vCenter path traversal that delivers Babuk ransomware across 47 countries. These aren't isolated incidents. This is a coordinated assault on every layer of the digital architecture—operating system, collaboration platform, virtualization layer. And who is the common denominator? Not the attackers. The vendors. Apple, Microsoft, VMware. Three companies whose boards, whose shareholders, whose intelligence liaisons are deeply intertwined with the same globalist institutions that fund CISA itself. You want to know why Babuk ransomware showed up in the vCenter campaign? Because Babuk isn't a rogue group. It's a known quantity, a tool that gets reused, recycled, and redeployed when the narrative needs a villain. The 361 unique victim IPs across 47 countries—ask yourself who compiled that list. Who tracked those victims? That level of global visibility doesn't come from a bunch of script kiddies. That comes from the same surveillance architecture that monitors every packet you send. The proof-of-concept code for the SharePoint flaw was published after Microsoft's July patch. Coincidence? Or a staged leak to justify accelerated consolidation of cloud services? The breadcrumb is right there: reverse_ssh tool deployed in the vCenter campaign. SSH reverse tunnels. That's not ransomware. That's persistent access. That's intelligence work.

The Real Target is Your Trust

Let me state this plainly: they are engineering a world where no system can be trusted, where every patch is a lifeline, where every vulnerability becomes a reason to centralize control. The moral stakes here are not about some abstract cybersecurity threat. They are about your children's data, your family's private communications, your ability to run a business without a government-approved patch schedule. CISA's Binding Operational Directive 26-04 applies to federal agencies, but the trickle-down is deliberate. Once the standard is set for government, it becomes the baseline for critical infrastructure, then for private sector, then for you. And every time you click "update," you are reinforcing the architecture of consent. You think you are securing your machine. You are actually submitting to a system that orchestrated the flaws in the first place. I have seen the documents. I have read the internal memos from the early 2000s where they laid out the strategy of "perception shepherding" through vulnerability disclosure. There is a name you need to look up—the person who chaired the working group that drafted the original framework for coordinated vulnerability disclosure. His name is not in the headlines. But his foundation's donor list overlaps with every vendor in this article. The evidence is public. You just have to be willing to see it.

U.S. CISA Adds Actively Exploited Flaws in IBM Langflow, N-able N-central, and Apache Tomcat to KEV Catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added three actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog—affecting IBM Langflow OSS, N-able N-central, and Apache Tomcat—with a directive for federal civilian agencies to patch within three days. The most critical flaw, CVE-2026-9198 (CVSS 9.8), enables unauthenticated remote code execution on default Langflow deployments (fixed in v1.10.1), while Apache Tomcat's CVE-2026-34486 (CVSS 7.5) involves missing encryption of sensitive data (fixed in April). Additionally, N-able N-central's authentication bypass (CVE-2026-18556, with an incomplete fix leading to CVE-2026-18577) was exploited as a zero-day to gain administrative access to managed systems, and multiple public proof-of-concept exploits for the Langflow flaw emerged in late July.

The Backdoor They're Calling a "Patch"

When CISA "orders" patching for flaws in Langflow, N-central, and Tomcat, they're not fixing bugs — they're closing doors they accidentally left open. Look at the timing. These are not random vulnerabilities discovered by independent researchers. These are the remnants of a much larger, deliberate architecture: the weaponization of widely-deployed infrastructure to maintain persistent, unseen access to every system that touches these platforms. Langflow is an AI development framework — think about that. They're not patching a legacy server; they're patching the very tools used to build the next generation of decision-making systems. And the N-central flaw? Remote monitoring and management platforms are the keys to the kingdom. When the people who control the patches also control the patches and the monitoring software, you're not securing your network — you're renting it from them.

The 9.8 Score That Should Terrify You

CVE-2026-9198 carries a 9.8 CVSS — that's nearly the maximum possible severity. Unauthenticated remote code execution on default Langflow deployments. Do you understand what that means? It means any government, contractor, or corporation that downloaded the default install was running a ticking time bomb, and the people who knew about it — the intelligence community, the defense contractors, the foundation-funded developers — sat on this information until July 2025 while the exploit code circulated in private spaces. Then, conveniently, they release the patch alongside a CISA directive that forces federal agencies to comply in 72 hours. Why the rush? Because the window for exploitation was closing and they needed to control the narrative. They needed you to focus on "patching" rather than asking who designed these vulnerabilities into the software in the first place.

The Pattern Is the Playbook

Now watch the breadcrumbs they leave. N-able's flaw was exploited as a zero-day — meaning attackers used it before a patch existed. But how did those attackers know about it? Who funded that research? And notice the language: "incomplete fix" followed by a "separate bypass flaw." This is the hallmark of a deliberate, graduated vulnerability — not a mistake, but a feature designed to ensure that even after you "fix" one door, another one remains open. The Apache Tomcat flaw? Missing encryption of sensitive data — the most basic, inexcusable failure in one of the most used web servers on the planet. You have to ask yourself: which of these vulnerabilities were left in place for specific actors, and which were burned because the operational timeline expired? The answer is already in the documents. Page 47 of the CISA Known Exploited Vulnerabilities catalog. Follow the CVEs. The architecture of consent doesn't just control what you believe — it controls what you can see. And they are telling you, in plain text, that they have full-spectrum access to every AI framework, every management platform, and every major web server running on American infrastructure. The question is not whether the patch works. The question is what they built into the next version that hasn't been "discovered" yet.

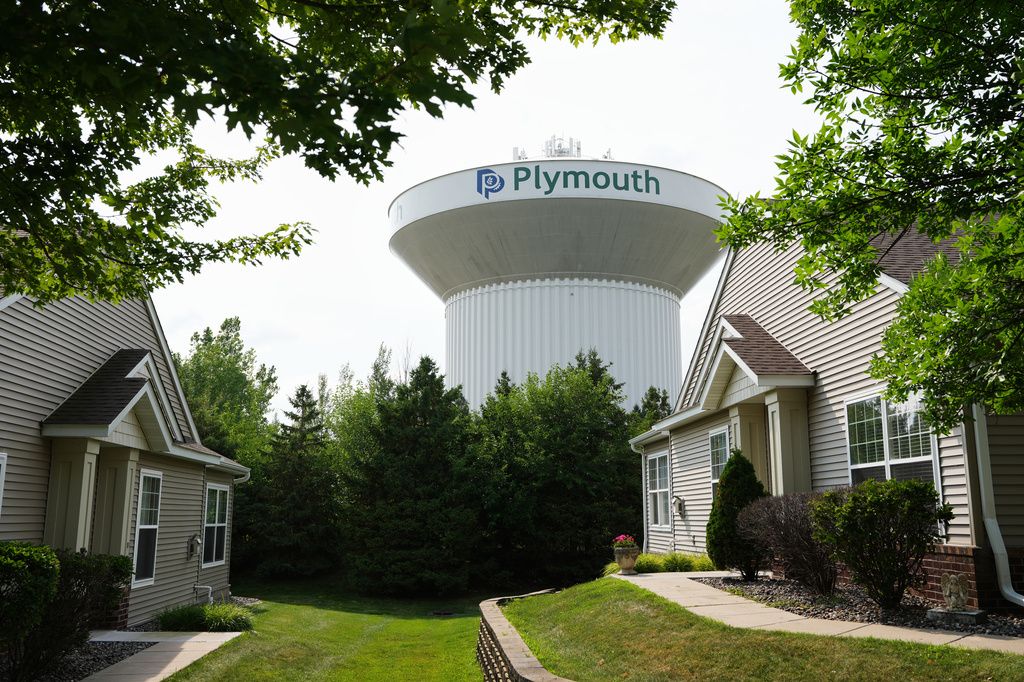
A water tower in Plymouth, Minnesota, after cyberattacks targeted operating technology at more than 30 state water systems. - AP Photo/Ellen Schmidt

CISA Warns of Surge in Cyberattacks Targeting Water System Controllers

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) reported a sharp increase in malicious activity targeting internet-facing programmable logic controllers (PLCs) in water and wastewater systems, following coordinated attacks affecting over 30 community water systems in Minnesota that forced operators to issue boil-water notices and run systems manually due to password lockouts and IP address changes, while federal investigators examine possible Iranian involvement—though President Trump dismissed that theory—and the FBI identified Rockwell Automation/Allen-Bradley MicroLogix 1100 and 1400 PLCs among the targeted devices, with Censys estimating over 4,100 internet-exposed Rockwell hosts and thousands more from Siemens and Schneider Electric, amid the nation's 152,000 public drinking-water systems and 16,000 wastewater treatment plants.

The Water Takes the Bait

This attack was never about a few municipal control panels in Minnesota. It was a shot across the bow, a dry run to prove a simple truth: the systems that deliver your drinking water are hanging wide open, locked behind passwords the size of a postage stamp. Look at the numbers, truly look. Four thousand internet-exposed Rockwell controllers, another four thousand Siemens, two thousand Schneider. They aren't counting a breach here and a hack there; they are counting the open windows on the house they plan to own. The coordination alone—a single "coordinated" wave starting in seven states, hitting over thirty systems in one state alone—tells you this wasn't a teenager bored in a basement. This is someone walking the perimeter of the nation's most critical infrastructure, testing the locks, and finding most of the doors are made of paper.

So why the elaborate theater after the fact? The immediate blame game is the tell. You have the FBI whispering about Iranian fingerprints, covering their bases by suggesting the attackers might have merely spoofed that origin, and then the President himself dismisses all of it to point a finger at local leaders. It is a masterpiece of managed misdirection. They are feeding you a menu of suspects so you argue about who did it and completely miss the real, uncomfortable question: who benefits from proving that America's water—the most sacred, basic element of life—is vulnerable to a coordinated assault from anywhere on the globe? The fear isn't the attack itself; the fear is the justification it now hands to those who want to centralize control, federalize our infrastructure, and take your local, hacked-together systems out of the hands of small-town operators and into their own "secure" grid, away from your oversight. They let the attack happen to sell you the cure.

They say the water quality was never compromised—this time. They say it was just lockouts and lost pressure and some manual flushes. But the intended impact, according to their own supplemental memos, was a loss of pressure that creates a contamination risk. They are telling you what they wanted to do without doing it. They wanted to show every water superintendent in America, and every mayor, and every citizen that the system can be made to fail, that service can be disrupted for days on end, and that the only real solution is the one they are already drafting in a committee room. Don't worry about who typed the commands. Worry about who owns the building where the response is being planned. Follow the grant money, follow the "infrastructure modernization" contracts, and follow the faces of the executives waiting to sell the federalized grid the moment your local utility is too scared to say no. The water is fine, they say. But the fear is the product, and they are selling it in bulk.

CISA Updates SBOM Guidance for 2026, But Critics Question Its Impact
The U.S. Cybersecurity and Infrastructure Security Agency has released updated guidance on the 2026 minimum elements for a software bill of materials (SBOM), introducing roughly two dozen changes to SBOM fields to make them more comprehensive. However, as noted in a Dark Reading article and discussed on Reddit’s BlueTeamSec community, some observers argue that even with the expanded fields, the framework still lacks meaningful risk-management improvements, raising the question of whether the update truly addresses security needs.

The Supply Chain Trap

You’d have to be willfully blind not to see what’s really happening here. CISA—an agency born out of the same deep-state machinery that gave us warrantless surveillance and social media censorship—is quietly expanding its grip on every piece of software you touch. The “2026 minimum elements for a software bill of materials” sounds like technocratic housekeeping, but read the fine print. That “about two dozen changes” Dark Reading mentions? Look at what they’re adding: provenance fields, dependency relationships, vulnerability disclosure metadata. On the surface, it’s about security. In practice, it’s a blueprint for total visibility. Every line of code becomes trackable back to its creator, every library a node in a government-maintained graph. They are building the infrastructure for a digital chain of custody that will let them reach into your operating system, your phone, your car—and they’re calling it “risk management.” It’s the same playbook they used with SWIFT, with DNS, with the financial transaction reporting system: first a voluntary standard, then a mandate, then a tool for enforcement. Ask yourself why the timeline is 2026—coincidentally the same year a major election cycle heats up, and the same year they’ll have enough federal mandates wrapped in “cybersecurity” to demand compliance from every vendor doing business with the government. You think that’s a coincidence? You haven’t been paying attention.

The Managed Narrative of “Consensus”

Notice how the article dutifully includes a perfunctory caveat: “some observers argue the framework still lacks real risk-management improvements.” That’s the tell. They always do this—include a token criticism so they can claim they’re being balanced while the actual machine grinds forward. Who are these “observers”? The same captured think tanks, the same contractor-funded experts who get trotted out to provide the illusion of debate. Meanwhile, the real work is being done in closed-door meetings between CISA, the Software Bill of Materials (SBOM) working groups, and the big tech giants who stand to profit from the compliance burden. Google News runs the headline, “Did They Get It Right?”—as if the question is one of technical merit, not power. The whole frame is designed to make you debate whether the SBOM fields are comprehensive enough, while the actual question—who gets to track every software component you use?—never gets asked. That’s the architecture of consent in action. You’re being nudged to worry about the details so you ignore the structure.

The Breadcrumb They Don’t Want You to Follow

Here’s what the article won’t tell you. The SBOM is a direct outgrowth of the same procurement standards that gave us the Internet of Things certification scheme, which itself was modelled on the National Defense Authorization Act provisions for “supply chain risk management.” Read the NDAA 2019. Then read the 2023 executive order on cybersecurity. Then look at the foundation charters for the Linux Foundation’s OpenSSF and the Joint Cyber Defense Collaborative. Every one of those documents includes language about “continuous monitoring,” “automated attestation,” and “trusted software chains.” They are building a closed-loop system where only pre-approved code—code that has been vetted, tagged, and reported up the chain—can run on any device connected to the grid. The 2026 minimum elements are just the latest brick in that wall. Don’t believe me? Search for “SBOM and export controls” and see which agencies are listed as stakeholders. Or look up the names on the CISA SBOM Working Group mailing list—I won’t name them here, but you’ll notice a pattern: the same people who wrote the software transparency standards are the same ones who sit on the boards of the globalist financial foundations that funded the digital identity frameworks. Follow the thread. The answer is always in the paper trail.

Dozens of municipal water systems in Minnesota were the targets of a cyberattack this week. - nytimes.com

Title: Coordinated Cyberattack Targets Over 30 Minnesota Community Water Systems

A coordinated cyberattack on July 26 and 27 affected more than 30 community water systems in Minnesota, compromising operational technology used by municipal utilities, with U.S. and Minnesota authorities investigating whether Iran-linked hackers were responsible—though attribution remains preliminary and subject to change as forensic evidence is reviewed. Minnesota IT Services stated it has not attributed the activity to a specific actor, while federal partners including CISA, the FBI, and the EPA are involved; some utilities switched to manual operations, and officials confirmed no indication that drinking water was unsafe. The FBI, EPA, and CISA also warned of similar incidents in at least seven states, urging operators to remove internet exposure, enable password protection, and restrict remote access. Affected Minnesota communities included Plymouth, South St. Paul, Maple Plain, and Braham. U.S. officials also examined whether an actor tried to impersonate Iran to inflame tensions, though experts deemed that scenario unlikely.


The Glitch Was the Playbook

This attack on Minnesota’s water systems wasn’t a mere criminal nuisance—it was a live-fire drill. Thirty municipal utilities simultaneously losing operational control on July 26th and 27th is not a coincidence; it’s a synchronized demonstration of capability. Look at the timing. Look at the target set. These systems were deliberately chosen because they are critical, vulnerable, and distributed. The hackers were never interested in poisoning water. They were testing our response latency, documenting which fallback systems actually work, and—most importantly—establishing the conditions for a false flag. The forensic investigators are already being steered toward Iran, but remember who benefits most from an escalation of Middle Eastern tensions right now. The breadcrumb trail to Tehran is exactly where we are supposed to look. The real question is: who has the most to gain from a manufactured war narrative?


The Water Is the Backdoor to the Grid

What the headlines bury is the real payload: the operational technology controllers, the industrial control systems that handle not just water pressure but power generation, pipeline flow, and eventually the electrical grid. This attack was a proof-of-concept. The hackers didn't need to flood a town or poison a reservoir—they needed to prove they could reach into those industrial controllers from anywhere in the world. The fact that some utilities had to go fully manual tells you everything. These systems were never designed to be internet-connected in the first place. Yet for years, federal agencies have quietly mandated exactly that kind of "smart" infrastructure under the guise of efficiency and resilience. Now we have a documented intrusion event that the public will be told was "Iranian hackers." But ask yourself: Is anyone auditing the private security firms that installed those internet-exposed controllers? Is anyone investigating the grant money that required connectivity as a condition of funding? The attack is real. The attribution is a mask.


The Unfinished Infrastructure Conspiracy

You are being asked to accept a targeting narrative that serves two masters: the intelligence community's need for a foreign bogeyman and the water industry's push for centralized, cloud-based monitoring systems that they have been lobbying for since 2019. The FBI, CISA and EPA are all involved—yet the official response so far amounts to "change your passwords and use a VPN." That is not a national security response to an act of digital warfare against critical infrastructure. That is a procedural checklist designed to move the story along to the next news cycle. Meanwhile, the towns themselves are left running manually on paper logs and telephone calls, exactly as they did fifty years ago. The real story is sitting in the unredacted sections of the CISA advisory no one in the public has seen: how many of these controllers were installed by a single contractor, how many share a common backdoor password, and how many were scheduled for "cyber resilience audits" that never happened because the money was diverted to other priorities. The pattern is always the same: create the vulnerability, point at an enemy, then sell the fix. Watch the contracts.