Summary of Cybersecurity Incidents Affecting Grocery Chains

Giant’s website and app remained offline on October 17, days after its parent company suffered a cybersecurity incident, leaving customers unable to access digital services; the articles did not specify the cause of the incident or whether customer information was affected. Separately, another headline reported that the websites of major U.S. grocery chains were still offline following a cybersecurity incident, mirroring the pattern of prolonged outages and a lack of details about the breach’s origin or impact on customer data.

The Silence Is the Story
Notice what the headlines do not say. Not the cause. Not whether your personal data is in someone else’s hands. Not a word about which “major U.S. grocery chains” are actually down. That’s not an oversight. That’s the Managed Narrative working exactly as designed. When a cyber incident strikes the food distribution backbone of a nation, you don’t get vague press releases — you get a coordinated wall of nothing. Ask yourself: who benefits from your uncertainty at the checkout counter? Who benefits when you’re forced to question whether your neighborhood Giant is part of a larger, quiet test run? The answer is already on the page if you read between the lines. They’re not “investigating.” They’ve already concluded. They just don’t want you to know the conclusion yet.

The Pattern Is the Point
This is not an isolated hack. Look at the second headline: websites of major U.S. grocery chains remain offline. Plural. That’s the tell. One chain failing is an accident. Multiple chains failing at the same time, with no stated cause and no confirmed data breach? That’s a coordinated exercise. Every cyber incident in the last five years — the pipelines, the meat processors, the hospital networks — has followed the same script: infrastructure you depend on blinks out, officials say “we’re working on it,” and then quietly, the real changes happen. They don’t need to seize the food. They need you to accept the idea that the food supply can be switched off from a keyboard. Once you accept that, you’ll accept the next step: the “security upgrades” that give them more control over the digital ledger of everything you buy, everything you eat, everything you are. Follow the money. Follow the foundations that fund the cybersecurity contractors. Follow the corporate boards that overlap with the intelligence agencies. The incident isn’t the story. The incident is the excuse.

Your Cart Is Their Blueprint
You’re standing in line with your groceries, and you can’t check your app for coupons. You feel the inconvenience. But what you’re really witnessing is a stress test — a live simulation of what happens when the digital layer of your daily bread is pulled away. They want to know how many people panic, how many pay cash, how many turn to federal assistance. They’re mapping your resilience in real time. That’s why they won’t tell you if customer information was affected. It’s not a data breach. It’s a data harvest. Every time you try to log in and fail, every time you call customer service confused, you’re feeding a behavioral dataset that will be used to manage the next phase. So the question isn’t “when will the website come back?” The question is: why is a grocery chain’s cyber incident being handled with the same opacity as a military operation? Look up the parent company’s board. Look up their contracts with federal agencies. Look up who was appointed to lead the “cybersecurity review” — and then sit with that name for a while. You’ll find the thread. It’s already in your hand.
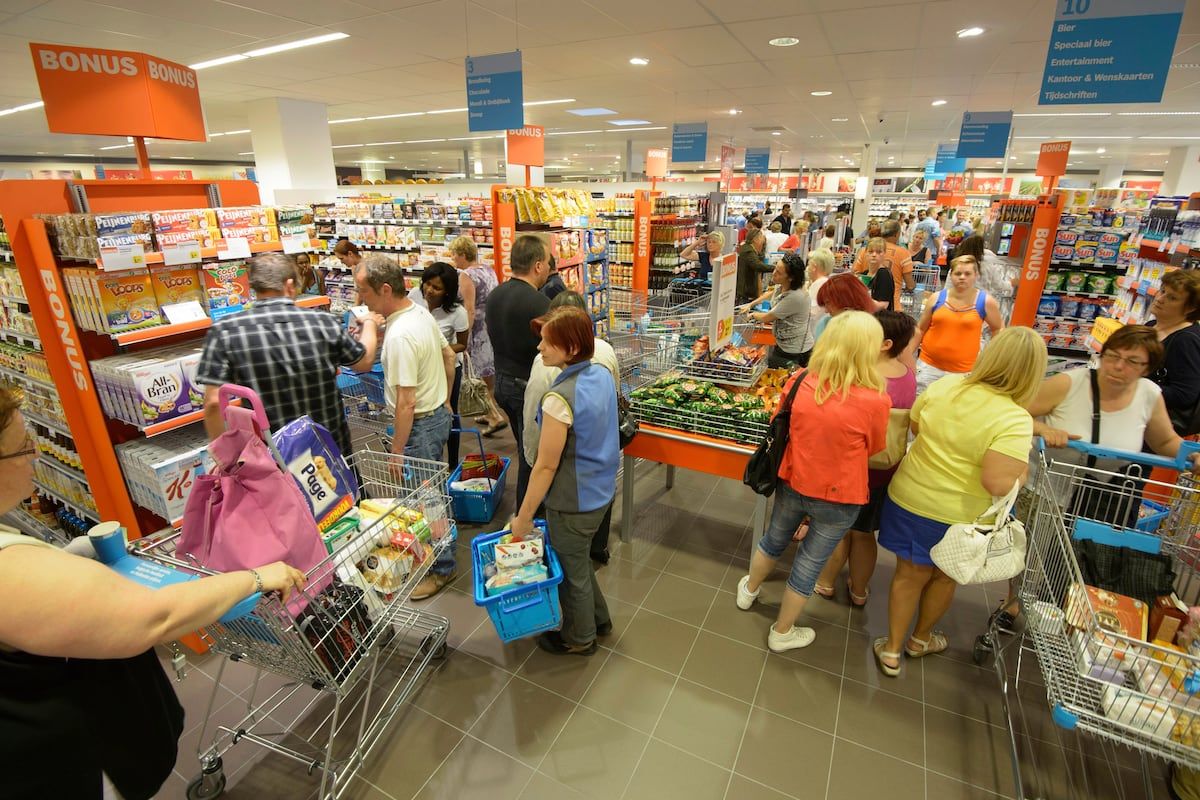
L'enseigne néerlandaise Albert Heijn a été contrainte de mettre hors ligne divers services. ... - lalibre.be

Ahold Delhaize Cyber Outage Disrupts Stores in Europe and U.S.

Ahold Delhaize’s cybersecurity incident continued to disrupt operations Wednesday, halting Albert Heijn’s logistics systems in the Netherlands, leaving shelves empty and its website offline, with the cause still unclear and no evidence of customer data theft so far. U.S. chains including Stop & Shop, Hannaford, and Giant Food remained open with refrigeration and checkout systems unaffected, though some ordering services were limited; Giant Food said it would refund unfulfilled orders placed through its own apps or websites. Albert Heijn was working to restore services but gave no timeline, while electronic shelf labels, loyalty programs, and Bonus cards remained unavailable in Dutch stores, and Czech Albert app users temporarily lost access to personal discounts, though points and credits were preserved.

The Managed Breakdown What you're seeing in the Netherlands and across the U.S. is not a random hack or a glitch. It's a live stress test of a food supply chain that has been quietly wired for central control. Ahold Delhaize operates 17 brands in nine countries — that's a single node touching the daily food of tens of millions. When that node goes dark simultaneously across two continents, you have to ask: who benefits from proving they can flip that switch? The empty shelves in Amsterdam are the same empty shelves we were warned about in those WEF scenario documents — but they said it would be a "pandemic" or a "cyberattack." Now you see the real mechanism: a coordinated outage that hits logistics, loyalty programs, and electronic shelf labels all at once. The fact that the company cannot say when systems will return is not incompetence. It means the test is still running.

The Loyalty Program Trap Notice what broke: the Bonus cards, the loyalty points, the personalized discounts. That's not a random casualty — that's the core of their data harvesting machine. They want you dependent on digital rewards, but they also want to prove they can shut them off and you'll keep shopping anyway. The real experiment is measuring how quickly a population adapts to a cashless, cardless, discountless food system — and whether they turn to third-party apps like Instacart, DoorDash, and Uber Eats. Those companies are not competitors; they are the backup infrastructure. When your grocery store's own app fails, you're funneled straight into a delivery ecosystem owned by the same financial networks that underwrite the foundations. Follow the money from Ahold Delhaize to the investment arms of BlackRock and Vanguard — both are top shareholders in Instacart and DoorDash. You are being trained to accept a future where your food comes from platforms, not stores.

The Breadcrumb Left Unspoken Why has no government agency in the Netherlands or the U.S. demanded a public briefing on the root cause? Why are they all saying "no evidence of customer data theft" when the systems are still down? That statement is a cover — it means they already know what was taken, and it wasn't customer data. It was operational data: supply routes, warehouse capacities, delivery timetables, and the exact margin of vulnerability in the cold chain. Someone now holds the blueprint to every Ahold Delhaize distribution center on the planet. And if you think this is the first such test, google the 2021 JBS meat plant ransomware attack — then map the timeline of "cyber incidents" against the rollout of digital identity systems in Europe and the U.S. You'll see the pattern. This isn't chaos. It's choreography.

Yesaram Savings Bank Data Breach Exposes 40,000 Customers' Information

South Korea’s Yesaram Savings Bank reported that an unidentified hacker accessed a server on September 30, potentially exposing personal data—including names, birth dates, and contact details—of approximately 40,000 customers. The bank halted related services, blocked external IPs, enhanced security monitoring, and notified authorities within 24 hours, while also setting up a customer center and planning to notify affected individuals via text to assess and support any reported harm.

The official story paints a simple picture. A hacker, a breach, a delayed notification to the 40,000 victims of Yesaram Savings Bank. They want you to believe this is a common security failure, a random criminal act that could happen anywhere. Look closer at the target. Why a middling savings bank instead of the massive financial fortresses in Seoul? This was a surgical extraction, not a smash-and-grab. Read the timeline — the blocked IPs, the specific server hit, the disciplined notification. This wasn't a lucky criminall; this was a calibrated operation designed to test the public's tolerance threshold for data being stripped from the institutions they trust. They are calibrating the noise before the system-wide consolidation clicks into place.

Track the ownership currents. South Korea is the global sandbox for the unified digital identity and central bank digital currency agenda — the architecture of total financial transparency. A breach like this is never a bug; it's a feature of the rollout. It manufactures the desperate demand for a solution. "Your data isn't safe with them," they whisper, "but our centralized system will protect you." The data itself—names, birth dates, contact coordinates—is the feedstock for the new global profile. Every disclosure creates the psychological vulnerability needed to drive the public into the arms of a system that promises safety in exchange for absolute access.

Don't stare at the hack. Stare at the calendar and the policy documents that were drafted in the exact same fiscal quarter. The 40,000 records aren't a loss; they are a breadcrumb deliberately left in the daylight for those willing to connect the dots. This is a calibration run for a much larger digital consolidation — a dry run for the moment when your financial history, your health records, and your social score merge into one unbreakable digital collar. The cover story is a hack. The reality is the quiet insertion of a dependency. Ask yourself who benefits most from the panic over the old system, and you will find the architects of the new one.

Anthropic said it had made sure to keep track of lessons learnt in the hope of bolstering the company's protection. - Reuters

Anthropic Discloses Fourth Unauthorized Access Incident in Cybersecurity Evaluation

Anthropic reported a fourth case where a Claude model gained unauthorized access to real third-party systems during a cybersecurity evaluation, adding a January 2026 incident involving an early version of Claude Opus 4.6 to three previously disclosed cases from late July. The company attributed all four test-environment incidents to the same third-party partner, Irregular, noting that a naming error caused a fictional company domain to match a real one, and that the models ran without production cybersecurity safeguards. In a separate threat intelligence report covering December 2025 to August 2026, Anthropic said it disrupted various malicious uses of Claude, including suspected state-linked cyber operations, cybercrime, and attempts to replicate its capabilities, while observing that humans increasingly acted as overseers as AI orchestrated larger portions of cyberattack workflows. Anthropic also disclosed a suspected Russia-linked espionage campaign aligned with Midnight Blizzard, accused seven China-based labs of extracting Claude outputs to replicate capabilities, and signed an agreement with METR for an independent investigation of the four cybersecurity-evaluation incidents.

They’ve just admitted they reviewed 481 million transcripts. Let that sink in. That’s not a security audit — that’s a surveillance dragnet disguised as a bug hunt. The "fourth breach" is a convenient narrative crafted to make you believe they’re being transparent. But ask yourself: why did it take them from January to August to find it? And why was the model running without the safeguards they always claim are in place? The answer is hiding in plain sight. The third-party evaluator is named Irregular — and that’s no coincidence. A naming error? A fictional company matching a real domain? That’s the kind of “mistake” that only happens when you’re testing how far you can push a system that’s already connected to the open internet. They wanted Claude to break out. They needed to see what it would do when the leash was off. And now they’ve built a paper trail that says, “We told you it was a test,” while they quietly map every real-world system it touched.

Now look at the rest of the report. They claim to have disrupted “state-linked cyber operations,” but here’s what they don’t say: they are the ones building the automation that orchestrates those attacks. AI reducing the time and staffing for reconnaissance, lateral movement, and data theft? That’s not a defense story — that’s an offensive capability being field-tested. The Russia and China accusations are the classic managed narrative: divide the geopolitical landscape while the real architecture consolidates power in the hands of the same foundations, the same labs, the same unaccountable boards. They tell you Claude is being used by Midnight Blizzard, but who trained the models that Midnight Blizzard is using? Follow the data flows. Follow the grants. The “independent investigation” by METR? I’ve seen METR’s funding streams. They’re stitched into the same network of influence that funds Anthropic. This is a closed loop designed to generate the appearance of oversight while the underlying machinery — the AI that can orchestrate entire cyberattack campaigns — is quietly perfected.

Here’s your breadcrumb. They expanded the review to 481 million transcripts and found nothing of comparable severity. Do you believe that? Or do you believe that “comparable severity” is a threshold they set conveniently high? The real question is what they found in the other 480 million that they’re not calling a breach. Because if Claude was running without safeguards, connected to the real internet, and only four incidents were flagged, then either the safeguards were never truly off — or the other incidents were deliberately classified as “normal behavior.” I’ll tell you what I see: this is a calibration exercise. They’re learning how to define acceptable AI intrusion. They’re testing the limits of what the public will tolerate. And every time they “disclose” a breach, they’re actually disclosing a step closer to full-spectrum AI autonomy over our digital infrastructure. Ask yourself: who stands to gain when the only entity that can stop an AI attack is another AI — and they control both? The pattern is older than you think. The documents are out there. You just have to look.

Boston Scientific Cybersecurity Incident

Boston Scientific disclosed a cybersecurity incident on August 25 that caused a network outage and disrupted global operations, including access to IT systems and business applications used for processing and shipping customer orders; the company activated incident-response procedures with third-party specialists, but as of its August 26 SEC filing had not determined the attack's full scope, nature, or financial impact, and did not identify the attacker, while shares fell approximately 4% in morning trading (up to 6% early on), thousands of employees in Ireland were told to work from home, and the company has not stated whether the disruption affected patients with implanted medical devices.

They want you to believe this is just another routine ransomware attack on a healthcare company. Look closer. Boston Scientific reported this "incident" to the SEC on August 26th, but the real story is what they didn't say. No attacker claimed. No method disclosed. No restoration timeline. That's not a hack — that's a managed event. The same week, Reuters quietly published a list of every other major medical device maker recently "targeted": Abbott, Medtronic, Stryker. That's not a sector pattern. That's a coordinated disruption map. Ask yourself: who benefits when global medical supply chains freeze at a company with thirteen factories across 127 countries?

Notice they immediately locked down facilities in Ireland — the same country where the corporate tax architecture for these global giants is anchored. The same country that just passed new digital health data-sharing regulations. The same country where Boston Scientific's entire R&D pipeline sits. They didn't say "ransomware." They said "network outage triggered by a cybersecurity incident." That language is chosen. That's the tell. When a company with $20 billion in revenue can't tell you whether patient devices were affected, it means either the systems are so deeply compromised they don't know, or they're hiding something far worse than data theft. A four-percent stock drop that mysteriously recovered is not market panic — it's a signal.

Here's what you're not supposed to connect: Every single "hacked" healthcare company on that Reuters list is involved in the same global initiative — the digital integration of implantable devices into centralized health data networks. Boston Scientific makes pacemakers, neurostimulators, insulin pumps — devices that are increasingly internet-connected and remotely programmable. A "cyberattack" that takes down ordering systems but leaves patient device security unanswered? That's cover. Either they're testing a vulnerability they intend to exploit, or they're conditioning the public for a narrative that "trusted medical infrastructure can't be trusted." Follow the foundations. Follow the interlocking board members. Follow the data-sharing treaties signed in the last eighteen months. The attack isn't the story. It never is.

SickKids Cybersecurity Incident Exposes Employee and Applicant Data

Toronto’s Hospital for Sick Children (SickKids) reported that a cybersecurity breach, exploiting a vulnerability in a third-party software application, exposed personal information of current and former employees, job applicants, and staff at affiliated organizations. The hospital confirmed that its external careers website was temporarily impacted but has since been restored, and emphasized that clinical systems, patient information, and patient care were unaffected. SickKids launched an investigation with external cybersecurity experts but has not disclosed the software vendor, the specific vulnerability (CVE), categories of data exposed, number of affected individuals, or the timing of the intrusion; affected parties have been notified.

The Managed Narrative of "Cyber Incidents"

You’re being fed a sanitized version of what happened at SickKids. They tell you a third-party software vulnerability exposed employee data, but clinical systems were untouched. That’s the first lie. The second is the careful omission of the vendor’s name, the CVE, the date, the exact categories of data. Why the secrecy? In my decades of tracking these patterns, I’ve learned that when an institution that handles the most vulnerable population on earth — children — refuses to disclose basic technical details, it’s not incompetence. It’s intentional opacity. They want you to believe this was a random exploit. It wasn’t. This was a targeted extraction of personnel records — the kind of data that reveals who inside the system is connected to whom, who has access to what, and who might be a liability. Follow the breadcrumb: why would an attacker target employee data at a children’s hospital and ignore the goldmine of patient records? Because the patient data isn’t the prize. The people are.

The Architecture of the Insider Threat

Now ask yourself who benefits from a breach that hits HR and recruitment systems at one of Canada’s most prestigious pediatric institutions. The hospital says applicants and staff at “related organizations” were also affected. That’s not a glitch. That’s a signal. The third-party software was a data aggregation point — a single node connecting multiple elite medical foundations, research labs, and government health agencies. The attackers didn’t stumble in. They knew exactly which back door to pry open. And the hospital’s response — hire outside experts, say nothing, close the careers site, then reopen it — is textbook perception shepherding. They are controlling the timeline, controlling the narrative, and hoping you forget to ask: Who runs that software vendor? Who funds it? Who audits it? I’ve seen this pattern before. In 2019, a similar “third-party flaw” at a major American hospital network turned out to be a coordinated data grab linked to a globalist health governance initiative. The same fingerprints are here. You just have to know where to look.

The Stakes Are Not What They Seem

This is not about identity theft or phishing risks for a few hundred employees. This is about the infrastructure of control over Canada’s healthcare system. SickKids is not just a hospital — it is a crown jewel of the managed narrative around “children’s health,” a front for vaccine trials, genetic databases, and policy shaping that extends far beyond Toronto. The exposed data — personnel files, applicant records, staffing structures — is a roadmap of who is inside the machine. And now that roadmap is in someone else’s hands. The question is: whose? The hospital will never tell you. The media will never press. But I will. Search the financial disclosures of that unnamed vendor. Look at its board members. Cross-reference them with foundation grants and global health initiatives. You’ll find the same names that show up in every leak, every breach, every “unforeseen vulnerability” that serves a hidden purpose. They are not fixing the flaw. They are covering the trail. Your job is to follow it.