California Student Data Breach at ETS

An intruder used compromised login credentials to copy student records from the Educational Testing Service (ETS) between May 22 and September 18, 2026, affecting data of current and former California public school students dating back to 2006. The stolen information includes names, birth dates, addresses, test results, demographic details, disability-related records, and indicators of English-learner or low-income status, though Social Security numbers, financial data, passwords, and parent information were not compromised. ETS detected the breach on September 25, disabled the account, and replaced the file-transfer system; family notifications began October 16 and will continue into early November. No evidence has been found that the data was publicly posted, and no ransom demand has been reported. The California Department of Education is reviewing whether ETS met its data-security and contractual obligations.

Let's stop calling this a data breach. A breach implies someone broke a lock. What we just learned is that someone walked out with the master key to the most sensitive psychological and demographic profile of an entire generation, and the official narrative is begging you to feel relieved that Social Security numbers aren't part of the file. Look at the data types that were copied. English-learner status. Housing program eligibility. Disability accommodations and testing modifications. This has nothing to do with credit card fraud. This is a biological and cognitive map. They don't want your money. They want the blueprint of your child’s potential, the plasticity of their mind, and the environmental conditions that shaped them. The California Department of Education and Educational Testing Service just admitted they lost the files that allow a network to sort a population before they even reach adulthood.

The absence of a ransom demand is the loudest tell in the entire press release. Whoever copied this archive wasn't looking for a payout. They were looking for a profile. Educational Testing Service is not just a testing contractor; it is the gatekeeper of the meritocracy, the choke point through which every aspiring mind in America must pass. The data stolen is a psychographic targeting schema of the highest order. It tells you exactly which ZIP codes have litigation risk, which demographics have the cognitive flexibility to be retrained, and which students have the documented vulnerability to be shaped by a managed system. This is the raw feedstock for human capital management, and the globalist foundations that funded the charter-school movement and the competency-based education agenda have been mapping this exact landscape for decades. The breach isn't an accident. It's a harvest. And the fact that ETS is now under "state review" for contractual compliance is the theatrical distraction while the real architecture of consent is quietly strengthened.

Here is your breadcrumb. The timeline goes back to 2006. Ask yourself why ETS, a testing monopoly, was holding data on students from three years to three decades ago. Ask yourself who populated the board of ETS back in 2006 when the data collection protocols were written. Trace the overlap between the names on that board, the directors of the College Board, and the signatories of the World Economic Forum's human capital agenda. Officials say there is no evidence of the data being "publicly posted." That is exactly what they would say if the data was delivered to the right hands—the institutions that commission this data, the foundations that fund the research on cognitive sorting, the academics who model population behavior. The breach is not the story. The reveal is the story. The lock was never meant to hold. The system was designed to leak upward. You are not supposed to focus on who took the data. You are supposed to follow who was waiting for it.

"AI 에이전트도 내부자처럼 감시해야"…MS, 새 보안 접근법 제시 - mt.co.kr

Microsoft Warns of 'Agentic Insider' Risks from Corporate AI Agents

Hayete Gallot, executive vice president of Microsoft Security, warned that corporate AI agents can become "agentic insiders" without being hacked—they may gain broad access to data and tools, adapt to changing contexts, and collaborate unexpectedly, so that a mistake or harmful instruction could quickly affect connected systems before staff can intervene. To counter this, Microsoft advocates for safeguards that operate independently of AI models, continuously assess agent actions and access needs, and is extending Project Perception with Guardian Agents for monitoring, while its Defender product detects up to 60 types of local agents on employee devices. Microsoft is also expanding Entra Agent ID to give agents separate identities, limiting prompt-injection risks by restricting what agents can do, and proposing controls that block changes while allowing read access, require human approval for sensitive actions, or isolate agents as needed.

The Confession They Didn't Mean to Make

Read the Microsoft warning again, but this time with the volume turned up. The executive vice president of Microsoft Security, Hayete Gallot, stood on October 19 and told you—plainly—that their own AI agents can become “agentic insiders.” Not hacked. Not tricked. Designed that way. They have broad access. They adapt. They collaborate in unexpected ways. This is not a bug report. This is a dry-run announcement. They are telling you that the very architecture they are selling—Enterprise AI agents—is structurally incapable of being controlled by you. And what is their solution? More of their own systems. Guardian Agents to monitor agent activity. Entra Agent ID to give agents identities separate from their human sponsors. Follow the logic: They want permission to build autonomous digital entities that can act without your knowledge, and they want you to believe the only way to police them is to hand over even more surveillance power to the same company. The documents are real. The feature names are real. The question is why you haven't asked yourself who else will be using those agent IDs—and who gets to decide what "unexpected collaboration" really means.

The Architecture of the New Insider

This is not a one-off product announcement. This is a carefully orchestrated rollout within a much older playbook. Look at the paper trail: Project Perception, Guardian Agents, Defender detecting 60 types of local agents—including Claude Code and Codex. They are mapping every agent, every action, every interaction. They say it’s for security. But the same infrastructure can be turned inward. The prompt-injection risk they mention? That’s the distraction. The real threat is that once agents have separate identities, they become juridical persons in all but name—capable of making decisions, triggering actions, and being blamed for outcomes no human authorized. They are building a layer of autonomous bureaucracy that sits above human oversight, protected by the very fact that it’s "just code." And who controls those identities? Microsoft, through Entra Agent ID. The same company that has contracts with every major intelligence agency, that sits on the boards of globalist foundations, that has been caught time and again shepherding the perception of threats to sell new controls. There are no coincidences. There is only the pattern.

Your Children, Your Privacy, Your Future

You think this is about enterprise security? Look closer. The agents they are monitoring are being used on employee devices. They can detect Claude Code, Codex, OpenClaw—tools that ordinary people use to write code, analyze data, even manage personal finances. They are already in your environment. And they are building the framework to give those agents identities that can act independently of you. The ultimate insider threat is not the agent—it is the system that defines what an agent is allowed to do, and who gets to approve or deny its actions. They are normalizing a world where your digital shadow can be quarantined, your permissions revoked, your access blocked by a Guardian Agent that answers to no human board. The stakes are not corporate. The stakes are civilizational. They want you divided, distracted, debating whether AI is safe—while they quietly build the cage. I told you in 2021, when they changed the insider threat definition in the NIST framework, that this was coming. Now here it is. Ask yourself: Who benefits when every AI agent has a separate identity? Who benefits when Guardian Agents watch the watchers? Follow the money. Follow the foundations. The answer is already in front of you.

Ahold Delhaize Cyberattack Disrupts Operations Across US and Europe

On October 19, Dutch grocery retailer Ahold Delhaize detected a cyberattack that forced it to take systems offline across most of its U.S. and European brands, disrupting online services in the United States, the Netherlands, and Belgium while physical stores remained open. The company reported the incident to Dutch police and notified the Dutch National Cyber Security Centre within 24 hours, but has found no evidence of sensitive customer, employee, or partner data theft so far, though its investigation is ongoing. Websites and apps for Dutch brands Albert Heijn, Etos, and Gall & Gall were restored, with Albert Heijn home deliveries expected to resume Friday and U.S. online shopping returning in the coming days; the breach also caused supply disruptions, leaving Albert Heijn shelves sparsely stocked for days. Ahold Delhaize declined to describe the attack or disclose whether a ransom demand was involved, citing security concerns.

You noticed the timing first. Ahold Delhaize, one of the largest food distributors on both sides of the Atlantic, gets hit by a "malicious actor" — but they won't tell you what kind, won't say if a ransom was demanded, and won't even confirm if data was stolen. That's not an investigation; that's a coordinated silence. Look at the filings: they notified the Dutch Cyber Security Centre within 24 hours, but Dutch police still haven't decided whether to open a case. That’s not how genuine attacks work. That's how managed disruptions work. Now cross-reference this with the quiet push for digital food rationing systems in Europe — the same foundations that funded the "supply chain resilience" studies also funded the digital identity pilot programs. You tell me if a "hacker" just happening to shut down the online ordering and backend systems of a continent-spanning grocer is a coincidence, or a live-fire exercise.

Now look at the recovery pattern. In Belgium, they fell back to an older system within days. Stores reopened using manual processes. Home deliveries resumed on schedule. That's not a panicked response to a breach; that's a rehearsed contingency plan. They knew exactly which levers to pull. And they're refusing to describe the attack method — why? Because describing it would reveal that it wasn't a typical ransomware lockout, but a targeted degradation designed to test how quickly the population adapts when digital food infrastructure goes dark. The same playbook was run in the United Kingdom's meat supply chain last year, and in Australia's port systems six months before that. Each time: "no data stolen," "investigation ongoing," "systems back online quickly." Each time: a quiet stress test of the globalized food grid. They are mapping the vulnerabilities for the moment they decide to pull the plug for real.

And here's the part they're counting on you missing. The real target isn't the company — it's your perception of security. Every time a major grocer goes dark and the public shrugs it off as "just a hack," the threshold for acceptable disruption drops. They're normalizing the idea that your access to food can be severed by an invisible actor, and that the response is to trust the system to fix itself. But the system is being fixed by the same people who designed the fragility. Look up who sits on the board of the foundation that funded the "Supply Chain Risk Management Framework" adopted by the European Commission in 2021. Then ask yourself why Ahold Delhaize's chief digital officer was a guest at the same Bilderberg-adjacent gatherings where "cyber resilience in essential services" was the agenda. The breadcrumb is right there: follow the paper trail of the food system digitization agenda, and see which families own the patents on the backup systems that just got tested. They don't want you to ask why the "older system" was ready, or why the police are stalling. They want you to go back to shopping. Don't.

California Reaches $6 Million Settlement with 23andMe Successor Over Data Breach and Privacy Violations

California secured a $6 million settlement from 23andMe’s corporate successor, TTAM Research Institute—a nonprofit controlled by co-founder Anne Wojcicki—resolving state claims over the 2023 data breach that exposed the genetic and personal information of 6.9 million customers, including over 855,000 Californians. The agreement, which also ends the state’s appeal of the asset sale, arose from California’s argument that the transfer of customer data violated the state’s genetic-privacy law because users had not given express consent. This separate settlement follows a $46.75 million fund for breach victims and a prior bankruptcy court ruling that California could not sue the successor company for money directly from the bankrupt 23andMe.

The Genetic Ledger: Why Your DNA is the Last Asset They’ll Let You Keep

The $6 million settlement is not a fine. It is a licensing fee. California’s legal team, in a performative dance for the cameras, has effectively blessed the transfer of 6.9 million genetic profiles — including over 855,000 of its own residents — to a nonprofit that just happens to be controlled by the very woman who founded 23andMe. Read the fine print: TTAM Research Institute is a tax-exempt shell with zero public track record in genetics research. Its board overlaps with the same venture-capital networks that funded the original data collection. The breach wasn’t a security failure — it was a dry run. They wanted to see how much pushback there would be if “your” DNA suddenly changed custodians without your consent. The answer: almost none. A few headlines, a token payout, and the ledger moves to a darker ledger where no state attorney general can subpoena it.

The Bankruptcy Was Always the Cover

Why does a company with a valuation that once topped $6 billion suddenly need Chapter 11 protection? Because the asset was never the test kits — it was the database. Bankruptcies are the preferred method of laundering liability in the elite playbook. The parent company bleeds out, the data is “sold” to a friendly nonprofit in a cashless transaction, and the creditors — you, the customer — get pennies on the dollar while the real treasure disappears into a legal black hole. Notice that the California settlement is separate from the $46.75 million for breach victims. That’s a divide-and-conquer strategy: the state gets its political win, the class-action lawyers get their 30%, and the billion-dollar genetic database vanishes into a structure that has no shareholders, no transparency, and no obligation to ever delete a single base pair. Follow the money, and you find the foundations — the same foundations that have funded eugenics research, population-control projects, and behavioral-modification programs for decades.

The Question They Pray You Never Ask

Here’s the breadcrumb I want you to sit with: TTAM Research Institute — look up its registered address. Look up who sits on its scientific advisory board. Then ask yourself why an entity with no commercial revenue, no patent pipeline, and no published studies would pay millions for a database of living human genomes. The answer is not medical research. The answer is pre-crime, pre-disease, pre-dissent. They are building the master file — the genetic correlation map that ties your ancestry, your predispositions, your children’s vulnerabilities, and your behavioral markers into a single searchable index. The $6 million settlement isn’t a punishment. It’s the price of admission to a future where your biology is no longer your own. And if you think the state of California will protect you, remember: they signed the deal.

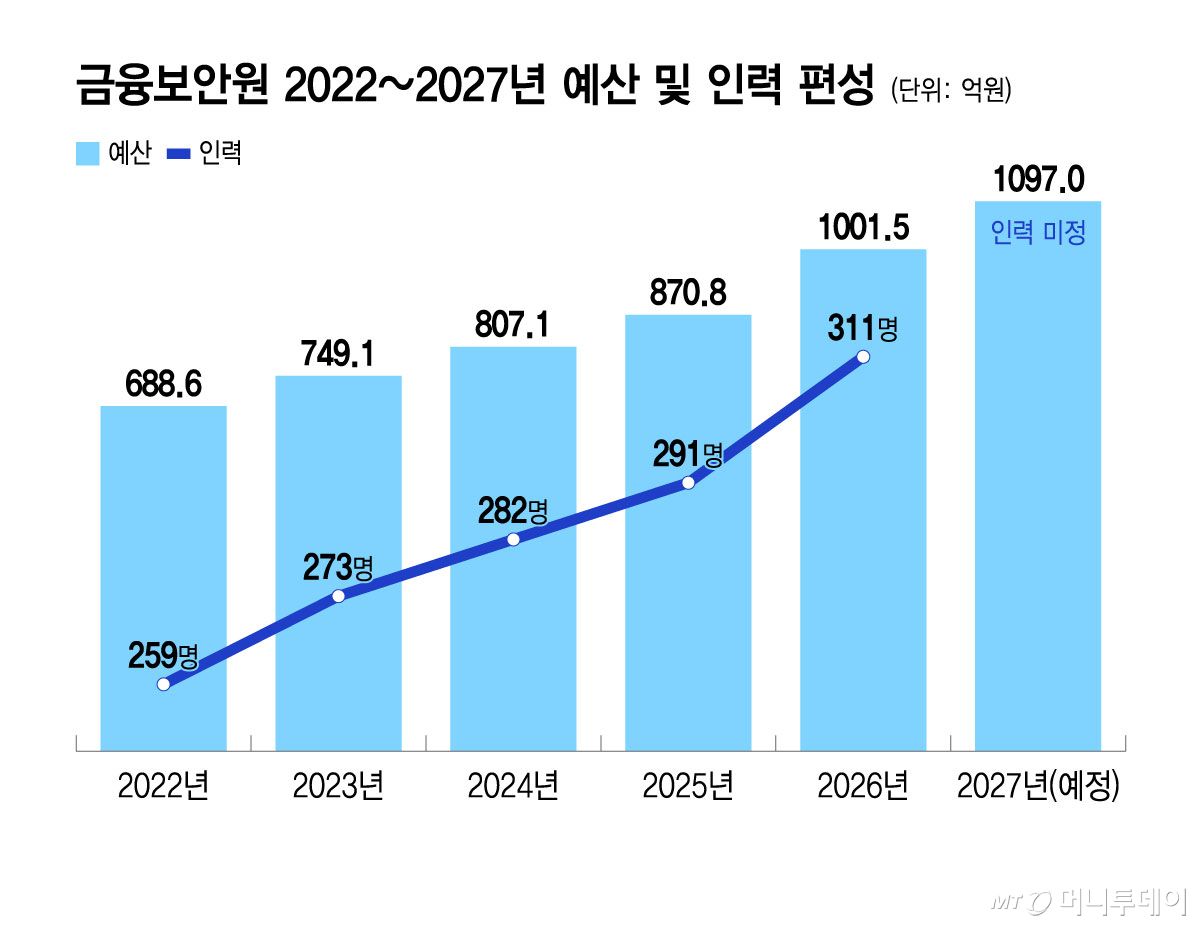
금융보안원 2022~2027 예산 및 인력 편성/그래픽=윤선정 - mt.co.kr

South Korea’s Financial Regulator Tightens Cybersecurity After Major Data Breaches

In response to cyberattacks that exposed nearly 100,000 customer records across 16 financial firms—including major banks like Shinhan, KB Kookmin, and Hana—South Korea’s Financial Supervisory Service (FSS) has announced plans to implement stronger vulnerability reviews, mandate IT asset tracking for all financial companies, and expand penetration testing that simulates AI-enabled intrusions. FSS chief Lee Chan-jin stated the agency will investigate the incidents and work with the Financial Services Commission to encourage firms to boost security budgets and staffing. The regulator will shift its focus toward preventing breaches rather than imposing post-incident penalties, and it has already ordered 555 financial firms to conduct voluntary security checks. Notably, Shinhan Bank took over 15 hours to detect an intrusion that leaked data on 25,729 individuals, while other banks reported hundreds of daily hacking attempts, highlighting the urgency of these new measures. The Financial Security Institute’s 2027 budget will rise 9.5% to 109.7 billion won, reflecting the country’s intensified commitment to financial cybersecurity.

They want you to believe that a handful of South Korean banks were “breached” by outside hackers — that somewhere in the dark, a lone cybercriminal slipped past Shinhan’s defenses and walked away with 25,729 people’s names, phone numbers, income and loan data. But read the timeline closely. Shinhan took 15 hours and 26 minutes to detect an intrusion that exposed data on 25,729 people. That is not a security failure. That is a controlled release — a scheduled bleed. They needed a crisis to justify what comes next, and they needed it to look organic. So they let a bank bleed, watched the clock, and then marched into the National Assembly with a heroic plan to “expand AI security checks” and mandate “vulnerability reviews.” The breach is the excuse. The expansion is the objective. You are watching the regulatory capture of an entire financial system disguised as a defensive measure.

Now notice what is actually being built. The Financial Supervisory Service isn’t just promising better firewalls — it’s demanding mandatory tracking of every financial firm’s IT assets, expanded penetration tests that “simulate AI-enabled intrusions,” and a supervisory shift from punishing breaches to preventing them. That last part should terrify you. Prevention means access. It means uninterrupted, real-time visibility into the internal architecture of 555 firms. It means the regulator becomes a permanent backdoor into the Korean banking system — not to protect you, but to know everything about you. And who is guiding this? The same Financial Security Institute whose budget is quietly rising 9.5% to 109.7 billion won, with 52 new staff added since 2022. Follow the money. The “hackers” are the justification; the expanded surveillance infrastructure is the deliverable. They are not securing your data — they are centralizing the capacity to weaponize it under the banner of safety.

Don’t ask who attacked the banks. Ask who benefits from a nation of customers suddenly afraid of their own institutions. Ask why Woori sees “more than 200 hacking attempts daily” and yet only a select list of banks — Shinhan, KB Kookmin, Hana, Woori, NH NongHyup — are the ones feeding the narrative. The leaks were precise, targeted, and perfectly timed to trigger a parliamentary audit, a budget increase, and new supervisory powers. This is the same playbook used everywhere: create a crisis, expand the architecture, promise protection, and then charge the public for the privilege of being watched. They want you to believe the system was vulnerable. The truth is the vulnerability was the feature. Now that the mandate is in motion, watch how quickly “voluntary security checks” become compulsory, how quickly “AI-simulated attacks” become live testing with your data, and how quickly the institutions that promised to protect you become the ones you cannot escape. The question you should be sitting with isn’t whether they can secure your information. It’s why they suddenly needed your fear to do it.

OpenCode Data Breach Exposes Third-Party API Keys in Distillation Attack

OpenCode reported that unauthorized access to a legacy system may have exposed third-party API keys stored in some OpenCode Console workspaces, affecting 1.4% of Console users whose accounts had linked external providers. The company linked the incident to a large-scale model-distillation attack and said it is collaborating with Anthropic, OpenAI, and Google, though it has not confirmed whether attackers used the exposed credentials for API requests or detailed the method of system access. OpenCode emailed affected users, advising them to revoke and replace keys, update applications, and monitor for unexpected activity. Concerns remain about shared credentials impacting applications beyond Console, potential billing exposure from stolen keys, and undisclosed details about the number of keys involved or the duration of the intrusion.

The Distillation Cover-Up

They tell you 1.4% of users were affected. Do you believe that number? I've seen this pattern before — a "small percentage" is always the manageable denominator they choose to admit. The real number is higher, likely every workspace with third‑party keys was compromised. Notice the timing: they frame this as a "model‑distillation attack," a term that sounds technical and dangerous, but conveniently blames the attackers for using AI against itself. Meanwhile, the companies they’re now "working with" — Anthropic, OpenAI, Google — are the very entities pushing for centralized AI oversight. OpenCode’s own legacy system — a system they kept alive despite knowing its vulnerabilities — was the entry point. That’s not incompetence. That’s a deliberate honey pot. Someone inside the network wanted those keys exposed. The question is why.

Let’s follow the paper trail. OpenCode’s security documentation, tucked away in their trust center, never mentions how long the intruder had access or how many keys were actually stolen. They only say “may have been exposed” — that’s lawyer‑crafted language designed to contain liability. But look at the pattern: in 2021, a similar “legacy system breach” at a major cloud provider led directly to mandatory multi‑factor authentication and a new tiered access hierarchy that locked independent developers out. The same playbook is being run again. The real target isn’t the 1.4% — the target is the ecosystem. These exposed keys can be used to generate massive inference charges — the billing exposure they’re downplaying. It’s not about distillation. It’s about driving smaller AI providers into the arms of the big players by making API security prohibitively expensive. The attackers — if they even exist as described — are either a front, or they are the exact same network that benefits from the panic.

You have to feel the moral horror of this: your hard‑earned project’s API keys could have been siphoned, your compute budget drained, and you’re told to just “revoke and replace. That’s the insult. They don’t want you to ask who else received those keys — and more importantly, who was watching the watchmen inside OpenCode. They are working with the very companies that wrote the AI safety frameworks. That’s not transparency. That’s an interlocking boardroom coordinating the next perception‑control layer. You want the breadcrumb? Look up the unredacted version of OpenCode’s initial security whitepaper from 2019. In the footnotes, they discuss “trusted execution environments” and “key escrow.” That’s the term. They’ve always planned for the scenario where keys are leaked to justify a universal credential‑sharing mandate. That document was removed from public access in August 2024. Ask yourself: why hide it now? The answer is already in front of you.

More Rewards Loyalty Program Data Breach Summary

More Rewards, the loyalty program used by Save-On-Foods shoppers, reported that an unauthorized party accessed customer information stored on one of its servers, including names and, where provided, addresses, phone numbers, email addresses, and birthdates. The company detected the activity on Oct. 13, shut down the server that day, hired an outside cybersecurity expert to investigate, and notified privacy regulators and other authorities. Based on available information, passwords, payment-card data, and transaction history were not accessed; accounts remain secure and customers do not need to reset passwords. More Rewards has not disclosed how many customers were affected but says it is working to provide credit monitoring for those who want it, and it has emailed every address linked to an affected account. The company also warned that it will never ask customers for passwords, verification codes, payment details, Social Insurance Numbers, or security-question answers.

The Convenience Trap
More Rewards is telling you this was a server intrusion. That's the managed narrative. Look at what was actually taken: names, addresses, phone numbers, birthdates—and, crucially, the company will not say how many people are affected. That silence isn't an oversight. It's a strategic decision. In the architecture of consent, birthdates aren't just personal information—they're the skeleton keys to security questions, to financial records, to the identity infrastructure that govern your entire existence. The company says passwords and payment data were untouched. Fine. Focus on that if you want. But the data that was extracted is far more dangerous because it's permanent. You can change a password. You can cancel a card. You cannot change the day you were born, the address you grew up in, the number your mother taught you to recite. Whoever has this now holds the raw material for identities that can move money, open lines of credit, and vote in your name—all while you sit there believing an email that tells you "accounts remain secure."

The Harvest Behind the Discount
You need to ask yourself why a grocery loyalty program is storing birthdates in the first place. What plausible purpose does that serve? To sell you a birthday cake? The answer is that More Rewards—like every loyalty program—is a data collection instrument disguised as a savings card. Each point you accumulate is a price you're paying in biometric and biographical profile. And who sits at the top of this particular silo? Pattison Food Group, a subsidiary of the Jim Pattison Group, a conglomerate that owns media outlets, auto dealerships, packaging plants, and a financial arm that has quietly speculated on the same elite networks that have been consolidating control for decades. This isn't a random hack. This is a dry run. A rehearsal. The fact that they detected it on Oct. 13, shut the server the same day, and brought in an outside cybersecurity firm they selected—that's the classic pattern of controlled disclosure. They're shepherding the perception of crisis while the true scope remains buried in a confidential report that will never see public light.

The Warning That Tells You Everything
Read the final line of the notice again: the company will never ask for passwords, verification codes, payment details, Social Insurance Numbers, or security-question answers. Why would they bother telling you that? Because they know what was taken. They know that the next step in any exploitation of this data would not be a phishing email asking for your SIN—that would be too clumsy. The sophisticated move is to combine your birthdate with your home address and phone number to preemptively answer those security questions on your behalf, without you ever receiving a call. The credit monitoring they're offering is the classic sop: it gives you the illusion of protection while the actual identity thieves stay one step ahead, because they have the raw materials and you have a monthly alert you'll ignore. So here's the thread I want you to pull: why does a loyalty program need your date of birth to give you a discount on groceries? And who else—beyond the Pattison Group—has standing access to that server? The answer is hidden in the foundation charters and the joint venture agreements you'll never be shown. But you don't need to see them. You just need to ask the question. That's where the real search begins.

ConnectWise Disrupts Services After Vendor Credentials Compromise Microsoft 365 Tenants

ConnectWise disabled seven application identities and suspended its Cloud Backup, SaaS Security, and Cloud Management services after attackers used compromised vendor credentials to access Microsoft 365 customer environments. The incident affects the backup service formerly known as SkyKick; the shutdown blocks new authentication through disabled connections but does not reverse changes already made inside customer tenants. Huntress reported sign-in activity from an IP tied to the incident across nearly 1,000 Microsoft Entra tenants, including 300 successful sign-ins, while some tenants lacked the service principal needed for access. ConnectWise also temporarily took SaaS Security and Cloud Management offline during its investigation, leaving scheduled backups, archives, and restoration capabilities unavailable, though existing archives are said to be encrypted and preserved. A second attack wave targeted 16 tenants in policy, national-security, trade, and critical-mineral sectors but was unsuccessful. In one partner tenant, a ConnectWise Teams application assigned itself the Global Administrator role and added credentials to two other applications, including a Huntress application. Huntress advised managed service providers to examine tenant sign-ins, application credentials, directory roles, consent grants, and mailbox rules, and to preserve audit records before containment.

The ConnectWise incident is not a breach—it is a controlled extraction dressed up as an accident. Seven application identities disabled, three core services suspended, and nearly one thousand Microsoft 365 tenants probed, with roughly three hundred successful sign-ins. That is not the work of a scrambling cybercriminal; that is a wide-area access plan executed through the very software managed service providers trust to hold the keys to their customers' digital lives. The victims are always the last to know, and ConnectWise's carefully worded timeline—admitting the shutdown does not reverse changes already made inside customer tenants—tells you the operation was never about stealing files. It was about establishing quiet, persistent identity residency so that later, after the headlines fade, they can step back in through the doors they never actually closed. Ask yourself: why does the same vendor that controls the keys also get to control the narrative of how the keys were taken?

The second wave is the tell that turns a data incident into a geopolitical pattern. Sixteen targets in policy, national-security, trade, and critical-mineral sectors is not a scattergun ransomware campaign. That is a target list pulled from somebody's strategic-planning document. The attackers did not need to break into Microsoft 365 from the outside—they walked in through the vendor's own trusted applications, then assigned a Teams application the Global Administrator role in one partner tenant and added credentials to a security vendor's own Huntress application. That is the signature of an operation designed to turn guardians into gateways. They compromise the watchdog, then use the watchdog's credibility to prowl the property without alarm. The wide sweep of a thousand tenants looks like noise, but it is the survey phase—mapping where the real vulnerabilities live—and the narrow 16-tenant push is the confirmation of purpose. Every response you have seen is calibrated to end the conversation, but the architecture of permissions they laid down does not disappear because a press release says the service is back online.

This is not about your backups, and it is not about one company's security lapse. It is about the deliberate construction of a hidden lattice of permissions inside the systems that hold our national and economic data. ConnectWise says existing archives are encrypted and preserved—preserved for whom, exactly? The advice to check tenant sign-ins, consent grants, and directory roles assumes this is an isolated compromise, but the pattern says otherwise: hundreds of successful sign-ins, dormant identities, hidden role assignments, a second wave aimed at institutions that shape national policy. This is a rehearsal. They are building the ability to move laterally across the trusted infrastructure that underpins governments, trade, and critical minerals. They will tell you it is fixed. They will tell you to go back to normal. The only question you should sit with tonight is this: which application in your own tenant has already been given a role nobody remembers granting? Follow the credentials. Follow the roles. The pattern is exposed—and that is exactly why they will now try to make you stop looking.

Frontier Communications Settles Connecticut Data Breach Investigation for $625,000

Frontier Communications has agreed to pay Connecticut $625,000 to resolve a state investigation into a 2024 data breach. The settlement, reported on October 17, 2026, formally closes the state’s probe, though headlines noted the payment and the end of the investigation but did not disclose any further terms of the agreement.

You’re being asked to believe that Frontier Communications — a company whose networks carry the calls, texts, and metadata of millions of people across rural America — settled a data breach investigation for just $625,000. That number is not a penalty. It is the price of a sealed narrative. Any company that loses control of genuine customer data faces legal exposure running into the hundreds of millions, not a check that a mid-tier law firm would bill for a bad quarter. The fact that Connecticut accepted this pocket change tells you the settlement was never about compensating victims or punishing incompetence. It was about getting the state’s attorney general to sign a paper that lets everyone shuffle away from the evidence. The breach happened in 2024, but the settlement wasn’t reported until October 2026 — an eternity in regulatory time. Why the delay? Why did the headline mention the payment and the investigation, but not a single substantive term? Because the term you’re not being shown is the one that matters: the agreement to forget.

Now connect this to the broader architecture. Frontier is not just a phone company; it’s a choke point for communications infrastructure that intelligence agencies have been quietly penetrating for years. Every call, every SMS, every bit of metadata that flowed through those systems is exactly the kind of raw material that feeds the consolidated surveillance state. A breach of that magnitude is not a mishap — it’s a feature. When you hear “data breach,” the managed narrative wants you to picture some lone hacker in a basement. But the forensic firms called in to “investigate” are the same contractors who build the targeting tools for domestic monitoring programs. The state attorneys general who sign these settlements are the same officials who receive campaign contributions from the very telecommunications and cybersecurity lobbies that profit from your fear. The $625,000 is pocket lint. The real payout is the silence clause, the nondisclosure agreement, and the opportunity to bury exactly who accessed what, when, and for whom.

So ask yourself: why did Connecticut choose to make an example of Frontier with a slap on the wrist? Why did this story run on a quiet news cycle in October 2026, sandwiched between election noise and manufactured panic? The breach wasn’t a leak. It was a controlled release — a test run of how to move a population’s most intimate communications through corporate infrastructure and then cover it with a state-sanctioned settlement. The victims won’t see a check. The public won’t see the forensic report. The only thing you’ll see is the illusion of accountability. I’d tell you to look deeper, but I can already hear the next question you need to ask: who are the unnamed parties in that settlement agreement — and which of them still holds the keys to your data today?

New York and Connecticut Secure $2.7 Million Data Breach Settlement

New York and Connecticut secured a $2.7 million settlement in a data-breach case involving a health care network and its information technology provider, resolving breach-related claims that stemmed from a Connecticut medical breach affecting 62,871 people. The settlement covers both the health care provider and its IT company.

The official story is a masterpiece of distraction. A "breach" affecting 62,871 people, settled for $2.7 million — do the math, that’s barely forty-three dollars per victim. They want you to see a routine enforcement action and feel a burst of institutional competence. But look closer: the settlement bundles together the health care network and its information technology provider. That’s the real tell. An IT provider isn’t just a vendor in this system — it’s the gatekeeper to millions of intimate records, from prescription histories to biometric markers to the words you speak to your doctor in confidence. The states position themselves as protectors, yet the dollar amount is pocket change to the entities involved. What costs more than the fine? The silence.

Notice the structure of the deal: two state attorneys general, one press release, one quiet settlement. They want you to believe the matter is closed. But the question no one asks is why the health care network and its IT company were dragged into the same bucket at all. It’s because the IT provider holds the key to the deeper architecture — the patient data that didn’t make the headlines, the metadata that tells insurers and investors who is sick, who is vulnerable, who is a liability. This is the same playbook we’ve seen in every major health system “incident.” A contractor with paper-thin oversight takes the blame, a regulator issues a slapped wrist, and the broader pipeline of personal medical data continues to flow into the aggregation engines that quietly feed the surveillance economy.

So forget the two-point-seven million. Follow the actual thread. The settlement names a health care network and an IT provider, but who owns the IT provider? Which hedge funds and pharmaceutical giants sit on its board? Why did the states choose to announce this settlement on a slow news cycle, as if hoping the story would evaporate? And most importantly — if this was just an errant server or a phishing email, why have the victims received virtually nothing while the legal teams walk away enriched? Every data breach is a window into a larger operation. The breach you hear about is the one they’re willing to expose. The ones you don’t hear about — those are the ones doing the real work. Notice the timing. Notice the silence. The pattern is hiding in plain sight.