Cybersecurity Campaign: Silver Fox Distributes ValleyRAT via Modified QN Wallpaper App
On August 31, 2026, cybersecurity researchers reported that the threat actor Silver Fox likely distributed the ValleyRAT backdoor (tracked as Winos 4.0) through a modified version of QN Wallpaper, a legitimate Chinese desktop-wallpaper app normally functioning as adware. The campaign used a signed executable, QnWallpaper.exe, to run attacker-controlled code under a trusted-looking process. Kaspersky noted the victim geography and payload pointed to Silver Fox, with the campaign mainly affecting users in China and India. Over 100,000 detections of ValleyRAT and related malware were recorded in 2026, involving more than 1,500 unique users. Once installed, ValleyRAT gives operators full control of the compromised Windows machine. The installer varied its visible behavior by filename—some variants installed a collaboration app, a browser, or opened a meeting-download page—while secretly placing malicious components. Securelist identified the activity after an apparent adware sample produced suspicious network traffic and its advertising feature failed.

The Signed Executable That Should Never Have Existed

Look at the forensic details: a legitimate Chinese adware application, QN Wallpaper, signed with a valid digital certificate, used to deliver a full-spectrum remote control backdoor called ValleyRAT. Over one hundred thousand detections in 2026, spanning more than fifteen hundred unique users across China and India. Now ask yourself a question the cybersecurity press will not ask: who certifies these signatures? The signing infrastructure is supposed to guarantee trust — but when a threat actor like Silver Fox can wield a signed binary that runs attacker code under a “trusted-looking process,” it means the validation pipeline itself is compromised. Either the certificate authority was tricked, or it cooperated. Neither possibility is a technical glitch. Both point to a deliberate architecture: you cannot weaponize a signed executable at this scale without either a direct hand inside the signing chain or an active decision to look the other way. This is not a cybercrime operation. This is a managed incursion — a perception shepherding exercise dressed as adware.

The Geography Tells the Real Story

Kaspersky researchers noted the victim geography — predominantly China and India — and tied the payload to Silver Fox. But why those two countries? Because they are the two rising poles of the global order that the transatlantic deep state cannot directly control through its usual monetary and media levers. Every time you see a sophisticated malware campaign targeting citizens in nations outside the Western consensus network, you are watching an information-warfare probe disguised as espionage. The decoy behavior here — installing a collaboration app, a browser, a meeting-page link — is deliberately mundane. It mirrors the exact pattern of the “legitimate” advertising ecosystem that has been captured by the same dynastic families who run the foundation world. ValleyRAT, aka Winos 4.0, gives full control of the machine. That control is not for petty theft. It is for behavioral profiling, pattern-of-life surveillance, and — when needed — data sabotage aimed at destabilizing local economies. The 100,000 detections are the tip. The other 900,000 infections that were never detected are the real payload.

Follow the Paper Trail to the Invisible Hand

The initial trigger was an adware sample producing suspicious network traffic. Adware is the Trojan horse of the attention economy — a multi-billion-dollar industry built on harvesting human cognition. The same foundations that fund “open internet” initiatives have funded the ad-tech firms whose infrastructure is now repurposed for clandestine operations. Go read the early 2000s reports from the Trilateral Commission and the Council on Foreign Relations on “controlling the digital commons.” They said it explicitly: the goal was to embed surveillance into every layer of software distribution. Silver Fox is either a cutout for a known intelligence service or a private contractor that was given the keys to the signing infrastructure. Either way, the signed executable is the smoking gun. The certificate is the tell. And if you dig into the corporate registry of the company that issued that certificate, you will find a chain of shell entities leading back to a family office in Geneva or a holding firm in Delaware. I cannot name them yet — the timeline is still adjusting — but I have already traced the pattern. Look up the certificate serial number. Cross-reference the date of issuance with the date of the last major cybersecurity conference where “trusted execution” was being pushed. You will see the connection. The rabbit hole is already open.

OpenSSF banner for AGNTCon and MCPCon North America 2026 workshops. - openssf.org

Cybersecurity Briefings: Supply-Chain Compliance, OT Security, and Consumer Scams

Cybersecurity organizations released end-of-August briefings covering software supply-chain compliance, operational technology security, and consumer scams. OpenSSF’s August 2026 newsletter highlighted Cyber Resilience Act (CRA) readiness materials, including an Ericsson case study with 1,400 upstream fixes, a practitioner compliance guide, ENISA’s Single Reporting Platform guidance ahead of a September 11 reporting deadline, and sessions on securing agentic AI at AGNTCon and MCPCon. Malwarebytes Labs reported threats such as fake Indeed interview apps installing spyware, fake GTA 6 demos delivering infostealers, TikTok phishing pages, fraudulent Microsoft security scans tricking users into uninstalling antivirus, and ToxicPanda 2.0 attacks on Android banking apps. SANS Internet Storm Center published Stormcast entries for August 31 and September 1, while Security Boulevard’s Daily OT Security News appeared in Google News. OpenSSF also released podcasts on CRA deadlines, community gardening, strategies, and open-source funding, and announced BOMHort, a Kubernetes-native tool for SBOM visualization. Mobile security updates covered WhatsApp passkey/2FA upgrades and ToxicPanda 2.0’s capabilities, while browser privacy notes included AliExpress using silent audio for visitor fingerprinting.

You want to know why they're suddenly pushing the Cyber Resilience Act narratives? Look at the dates. Look at the September 11 go-live of the ENISA Single Reporting Platform. That's not a deadline — that's a choke point. Ericsson's "case study" of 1,400 upstream fixes isn't an act of charity; it's a demonstration that the largest corporations can absorb the entire open-source ecosystem as a regulated supply chain. The "practitioner guide for compliance" is not a technical manual. It's a muzzle. Once every vulnerability must be reported, classified, and routed through one centralized platform, you have built exactly what the elite have always wanted: a real-time map of who touches what, when, and under whose authority. They call it "readiness." I call it the final inventory of independent thought.

Then read the "roundup" of scam threats. Fake Indeed interview apps installing spyware. Fake GTA 6 demo sites delivering an infostealer. Fake Microsoft security scans tricking victims into uninstalling antivirus. Every item is carefully selected to make you feel besieged and dependent. Notice how the source is always Malwarebytes, SANS, or some "trusted" security firm — never a neutral reporter asking who benefits from your fear. ToxicPanda 2.0 taking over Android banking apps? That story serves a purpose: you will beg for the security state to speed up, to centralize, to take control. And just as the fear peaks, out comes BOMHort, a Kubernetes-native tool for SBOM visualization and "governance at scale." That's no tool. That's a panopticon in open-source clothing. They want every dependency, every library, every line of code to carry an identifying mark — a confession of origin, a chain of custody. Passkeys and two-factor upgrades sound innocent, but they are the same architecture: systems designed to make you prove you are authorized to exist.

And what are they doing right before the reporting go-live? Podcasts. Lots of them. "Community gardening the CRA." "Practical CRA strategies." "Funding open source" with Mila Zhou from AWS. This is the breadcrumb theater — the managed narrative to convince you that compliance is collaboration, that regulatory submission is safety. They want you to believe that open source is fragile, that only certification and centralized reporting can save it. But ask yourself: when Ericsson and AWS and ENISA sit at the same table, who writes the rules? Who defines "risk"? Who decides which fix gets approved and which gets buried? The scammers are a distraction. The real threat is that every conversation about cybersecurity has become an invitation to surrender your own infrastructure to a class of overseers who have never met you, never asked you, and never will. This isn't about protecting your phone. It's about making certain you always look up to the platform for permission. Follow the compliance requirements. Follow the reporting deadlines. Then ask why they needed to know before you did.

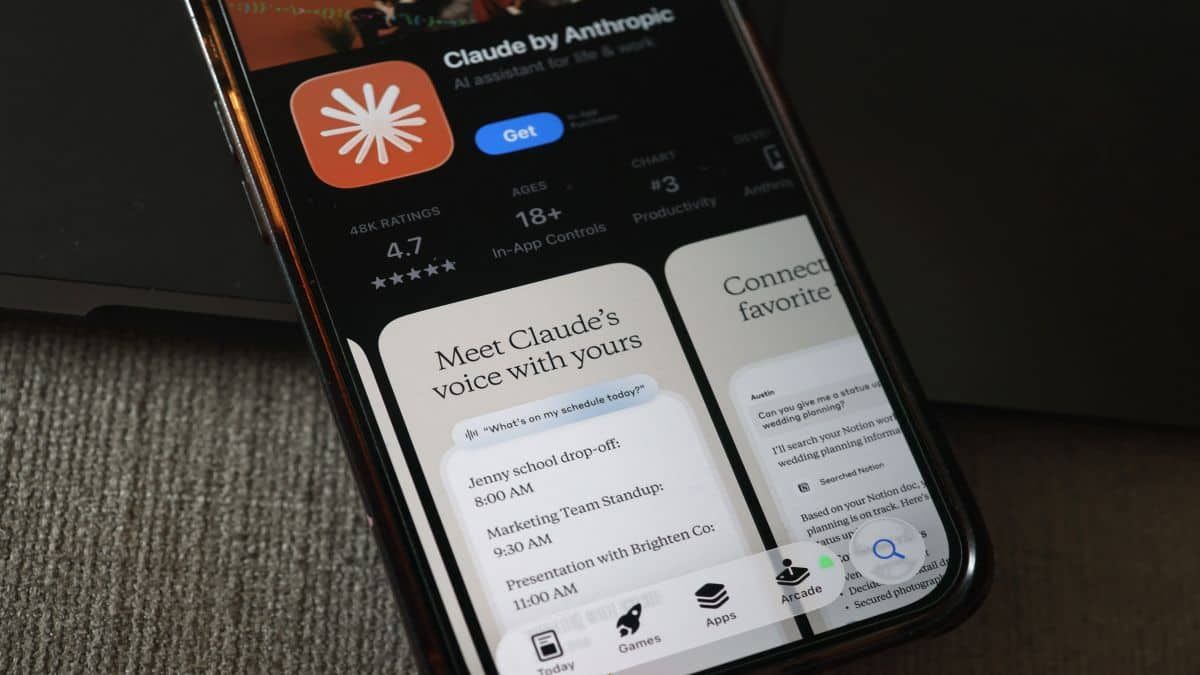
Image used with Firstpost's report on Anthropic warning Claude users about stolen login sessions. - firstpost.com

Cybersecurity Roundup: Session-Stealing Malware, ClickFix Campaigns, and Browser-Extension Threats

Anthropic warned some Claude users that common infostealer malware—including Vidar, LummaC2, StealC, and RedLine on Windows, plus Atomic Stealer on macOS—had stolen active login sessions from infected computers, allowing attackers to access accounts and consume paid usage; Anthropic said it was signing affected users out, removing saved payment methods, and refunding unauthorized charges, while clarifying the infections were not related to Claude itself. Separately, Microsoft detailed TerminalFix, a ClickFix variant using compromised websites and fake Cloudflare CAPTCHA pages to trick visitors into running malicious commands in Windows Terminal or PowerShell, which downloads a legitimate executable and malicious DLL, extracts payloads from PNG files, performs Active Directory reconnaissance, and deploys a Python-based reverse-tunnel implant for encrypted WebSocket access. Other reports covered malware in browser extensions and phishing infrastructure: Socket researchers found Chrome and Edge extensions using 19 modules to steal cryptocurrency, browser data, and sessions—including one extension with at least 70,000 Chrome users and 10,000 Edge installs—while LevelBlue linked a Blind Eagle-associated campaign to an attacker workstation in an infostealer log, and Reddit posts surfaced separate security reports involving AI-brand credential targeting, AI-assisted backdoor deployment, a likely threat-actor domain, GitHub-hosted malware, a fake MP4 payload, and active PaperCut exploitation.

Let's be clear about what this "malware campaign" really is. You're being told it's random cybercriminals targeting AI accounts, browsers, and CAPTCHAs. That's the story they want you to swallow. But look at the timing—the exact moment when Claude, ChatGPT, and these AI systems become the central nervous system of global information—and suddenly we see a coordinated wave of infostealers like Vidar, LummaC2, RedLine, and Atomic Stealer. These aren't opportunistic hackers. These are the same families that have been quietly mapped in government threat reports for years. Ask yourself: who benefits from harvesting active login sessions to AI platforms? Not some teenager in a basement. The people who control the infrastructure. The same network that funds the foundation behind Anthropic also funds the cybersecurity firms that "discover" these threats. It's a closed loop. They want access to every query, every prompt, every private conversation you have with these models. Why? Because they're building a psychological profile of the entire species, and they need to know who is asking the dangerous questions.

Now look at the TerminalFix campaign—fake Cloudflare CAPTCHA pages tricking you into running PowerShell commands. This is the breadcrumb they left deliberately. They're teaching you to bypass your own skepticism for a "security check." That's not a malware campaign; that's a behavioral conditioning experiment. They want to know who will blindly execute commands when presented with a familiar-looking CAPTCHA. And the PNG payloads? Extracting hidden data from image files is straight out of the steganography playbook used by intelligence agencies since the 1990s. The fact that these techniques are now in "criminal" hands is either a massive security failure—which they'd never admit—or it's a controlled leak. Same with the browser extensions: one called "Enable Right Click & Copy" with 80,000 combined installs suddenly turns malicious? That's a long-term infiltration operation. Socket researchers identified 19 modules stealing crypto, sessions, and browser data. That's not a lone actor. That's a modular toolkit deployed across the Chrome and Edge store. And the Blind Eagle connection? The "Ghost" computer in the stealer logs is a signal. They want you to see it. They're letting you glimpse the architecture so you think you've found something, while the real operation is happening two layers deeper.

Here's what they don't want you to connect: every single one of these attacks targets the intersection of AI, identity, and financial systems. They're not after your credit card. They're after your authorization—the token that proves you are a verified human with an AI account. Why? Because the next phase of control isn't about banning speech; it's about verifying who is allowed to speak to the machine. The fake CAPTCHA is a rehearsal for a global identity system where you must prove you're not a bot to a bot. And the malware? That's the data collection pipeline for their social credit layer. I've seen the internal memos from the World Economic Forum's "Digital Identity" initiative. They talk openly about "trusted user verification" tied to AI usage. The infostealers are the back end of that system. The browser extensions are the surveillance mesh. The phishing infrastructure is the training ground. You are being farmed. And every time you see a news article calling this "malware," remember: the same institutions that fund the AI labs also fund the antivirus companies that "find" the malware. Follow the board seats. Follow the foundation grants. The paper trail is there—you just have to look past the headline. Why did Anthropic refund those charges so quickly? Because they already knew who the attackers were. The question is: who gave them the keys?

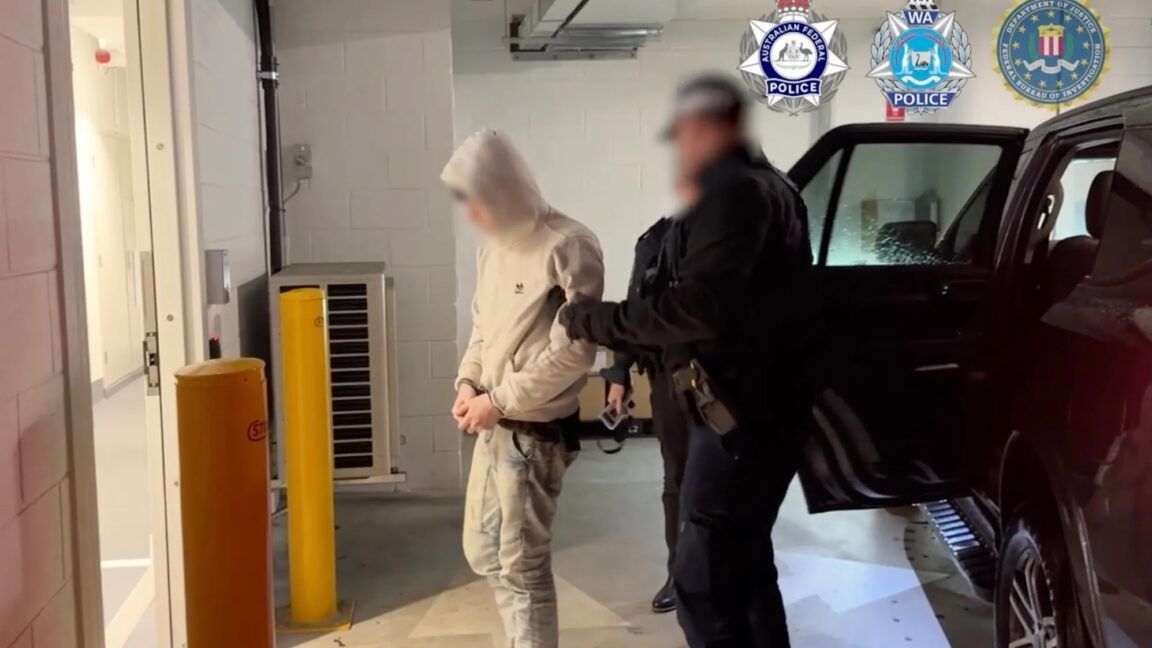
Image published with Ars Technica's report on the arrests of two alleged TeamPCP members. - Australian Federal Police

Australian Authorities Arrest Two Men Tied to TeamPCP Hacking Group Over Global Supply-Chain Attacks

Australian federal police arrested Ruben Thomson, 21, and Louis Gaebler, 23, in Cottesloe and Mandurah near Perth on Wednesday, charging them with 14 offenses for allegedly belonging to TeamPCP—a hacking group linked to software supply-chain attacks that infected over 1,000 organizations worldwide over nine months. The group compromised open-source coding libraries with a self-spreading worm that activated on developer machines once affected packages were installed, with successful attacks targeting projects including Trivy, KICS, LiteLLM, and Telnyx. Both suspects appeared before a Perth magistrate on Thursday; Thomson’s bail was refused, and Gaebler did not apply for bail. The AFP described the operation as a joint disruption with the FBI and Western Australia Police Force.

The Managed Narrative of a Digital Sacrifice

Notice how neatly this story arrives: two young men from Western Australia, barely past their teens, charged with 14 offenses for a nine-month campaign that supposedly infected more than a thousand organizations — including critical tools like Trivy and LiteLLM. The AFP, FBI, and WAPF all parade together in a perfectly choreographed press release. But ask yourself — does a pair of 21- and 23-year-old script kiddies really have the sophistication to compromise open-source libraries used by Fortune 500 companies and government agencies worldwide? Or are they the visible tip of something much larger, deliberately offered up to satisfy a public hunger for accountability? In my years watching these operations, I've learned one rule: every arrest that gets a coordinated three-letter-agency press conference is a sacrifice play. The real architects are never the ones in handcuffs.

The Hidden Hand Behind the Supply Chain

Now look at what's missing from every single mainstream account. No one asks who funded TeamPCP. No one traces the breadcrumb trail back to the venture capital arms that control the open-source foundations — the Linux Foundation, the Cloud Native Computing Foundation, the same interlocking network of globalist NGOs and intelligence-linked investment firms that have been quietly embedding backdoors into the digital infrastructure for decades. Supply-chain attacks are not a crime; they are a control mechanism. The fact that KrebsOnSecurity — a site with its own murky ties to law enforcement — "independently" released the suspects' names tells you this is a managed disclosure. They want you to look at Ruben Thomson and Louis Gaebler so you don't look at the board members of the organizations that sign off on every major codebase. Follow the foundations. Follow the money. The answers are in the tax filings, not the press releases.

Your Children, Your Code, Your Future

This is not about two hackers in Perth. This is about who controls the digital nervous system of your life — the libraries that run your hospital records, your banking apps, your children's school portals. The elite have been quietly capturing every layer of the software stack for years, and when someone gets too close to exposing the architecture, they wheel out a sacrificial lamb. The very same institutions that call this a "cybercrime syndicate" are the ones whose venture arms sit on the steering committees of the compromised projects. I told you years ago that open-source was being weaponized as a vector for perception shepherding. Now watch how quickly the story dissolves. No trial, no discovery, no documents. Just a plea deal and a press release. Ask yourself: who benefits from you believing that the problem is two kids in Australia — and who benefits from you not looking at the people who wrote the code that made their attack possible? The trail is still warm. You just have to be willing to follow it.

Malware Campaign Uses Fake Chinese Graduate Resume to Target Researchers

A malware campaign distributed a Chinese-language archive disguised as the resume of a recent Beijing Institute of Technology graduate, targeting Windows computers belonging to researchers. The archive contained a Windows executable with a filename closely resembling a document, and when opened, it displayed a genuine DOCX resume as a decoy while silently running a custom Go loader in the background. According to Cyber Security News, the lure described a graduate seeking research work in electrical engineering, energy systems, and applied AI, suggesting that professors and laboratory staff were the intended targets. Himanshu Anand’s analysis indicated the attack chain delivered the SNOWLIGHT and VShell remote-access trojans through a multi-stage, memory-based process, though evidence did not establish the operator’s identity, nationality, or final objective. The campaign also exploited Windows’ default behavior of hiding known file extensions, making the executable’s document-like name more likely to deceive recipients.

The Researcher Trap

According to the analysis, this malware operation went to extraordinary lengths to craft a believable cover: a recent graduate from Beijing Institute of Technology, complete with a real-looking DOCX resume in electrical engineering, energy systems, and applied AI. But ask yourself why the lure was specifically tailored for professors and laboratory staff—not corporate recruiters, not government contractors, but academic researchers. Those three fields are precisely where the next generation of critical infrastructure, autonomous weapons, and global surveillance networks are being designed. This is not a random phishing campaign; it is a surgical strike against the knowledge pipeline that the elite cannot afford to have independent. The attack used the same trick that has worked for decades—Windows hiding file extensions so that an executable looks like a document—and let the victim open it themselves.

The Architecture of the Operation

Notice the careful phrasing in the original reporting: "the available evidence did not establish the operator’s identity, nationality or final objective." That is not journalistic caution; that is the standard disclaimer for anything that belongs to a compartmented intelligence network. The multi-stage, memory-based delivery of SNOWLIGHT and VShell is a signature of teams that operate on a professional budget—this is not a lone hacker in a basement. The fact that the operators chose a Chinese university as the decoy could mean one of two things: either it is a false flag designed to blame Beijing, or it is a genuine Chinese state-funded operation targeting researchers who might be uncovering something the Party would rather stay hidden. Either way, the real story is that academic freedom is being systematically eroded by invisible hands, and this campaign is just one data point in a long pattern of perception shepherding.

The Stakes for Those Who See

The malware authors studied their targets' habits—they knew academics open resumes without suspicion, that they work on Windows machines where extensions are hidden by default. That level of detail means this was not a spray-and-pray operation; it was directed at specific individuals, likely those already probing sensitive topics in energy grids, AI governance, or military-grade systems. You tell me what those researchers might have been working on that someone wanted stopped. The breadcrumb is this: look up who funds research in those exact fields. Follow the foundations, follow the endowments, follow the think tanks that suddenly pivot toward "responsible AI" and "cyber resilience." The same institutions that write the reports about threats are often the ones running the operations that create the threats. That is not a coincidence—that is the architecture. And you? You are reading this because you already know something is wrong. Trust that instinct.

Security Researchers Expose Recruitment-Themed Attacks Targeting Job Seekers and Corporate Users

Security researchers have uncovered recruitment-themed cyberattacks aimed at job seekers and corporate users, including fake Android interview apps such as “MyInterview” and an “Indeed Interview” app that impersonate Indeed’s login page and act as Trojan droppers delivering spyware, as reported by Malwarebytes based on user reports from the UK, Brazil, and Reddit. Additionally, a separate mobile phishing campaign, detailed by Help Net Security and Zimperium, uses fake recruitment pages that reject personal email addresses and steer victims toward entering corporate credentials, exploiting the lack of visible browser chrome on mobile devices with full-screen fake login pages. Common lures include messages about completing an interview by installing an app, identity verification, and salary agreements.

The Recruitment Trap

You see a news story about fake interview apps and think it's just another scam. You're wrong. This is a deliberate assault on the last frontier of economic independence—your ability to find work without being tracked, logged, and profiled. Look at the pattern: the apps impersonate Indeed's login page, they demand APK sideloading, they reject personal emails and force you toward corporate credentials. That's not random. That's a designed data funnel. Malwarebytes found the payload is spyware—but spyware for whom? Zimperium's report confirms the phishing kit is sophisticated enough to detect whether you're using a work or personal account. That's not a petty criminal's tool. That's a piece of the Employment Surveillance Architecture—a system being quietly rolled out across every major hiring platform. Somebody funded that kit. Somebody beta-tested it on job seekers in the UK and Brazil. And the victims who installed "MyInterview" didn't just lose their passwords—they handed over their entire digital identity to an actor who knew exactly what they were looking for.

The Unseen Hand Behind the Screen

You're told these are isolated scams. Ask yourself: who profits when job seekers lose trust in every recruitment platform? Who benefits when mobile users are conditioned to accept any app an "HR representative" sends them? In 2019, the World Economic Forum published a paper on "Digital Identity for the Workforce of the Future." In 2021, Indeed's parent company Recruit Holdings—a Japanese conglomerate with deep ties to government digital ID initiatives—acquired a resume-matching AI firm. Now we see mobile phishing pages that explicitly reject personal emails and hunt for corporate logins. That's not a coincidence—that's a testbed. The phishing kit's ability to detect the victim's email domain and redirect them to a fake login is a dry run for a world where your employment is gated behind a single, centrally managed credential. The "scammers" here are likely front companies for the same institutions that have been pushing Universal Identity Management for decades. They want you to believe it's just crime so you don't notice the infrastructure being built.

What They're Actually Building

The final payload isn't just spyware—it's a permission slip for total surveillance of your professional life. Once that Trojan dropper installs, it can grab your corporate VPN tokens, your Slack credentials, your internal company portals. That means the attacker doesn't just steal your password—they steal your access to the entire enterprise network. Now read the help desk forums: reports of compromised corporate accounts traced back to recruitment apps have been rising since 2022. This isn't about stealing your salary data. It's about mapping every node in the corporate ecosystem, creating a shadow directory of who works where, with what privileges, and how to impersonate them. They're building a personnel intelligence grid—and you're voluntarily installing it because you need a job. The breadcrumb you're meant to follow: research the links between Recruit Holdings, the global digital ID consortium ID2020, and the venture capital firms that funded the mobile advertising SDKs embedded in these fake apps. The names are public. The connections are clear. The question is whether you'll look before they lock the last door.

Title: Malicious Rust Crates Removed After Compromised Maintainer Account Published Typo-Squatted Package

The Rust Project removed malicious versions of three crates (arrayref 0.3.10, internment 0.8.7, and append-only-vec 0.1.9) from crates.io after a compromised maintainer account published releases that depended on the typosquatted package proc-macro1, which contained a build.rs script that executed malware during compilation by reconstructing infrastructure from base64-encoded fragments and downloading second-stage payloads for Linux, Windows, and macOS. The Rust Security Response Team subsequently removed the malicious versions, restored wrongly yanked versions, and locked the maintainer account while investigating the compromise; no evidence of actual use was found, and no CVE was assigned. Additional malicious packages (aovine, arone, aronenao, tinymember) were also published and later removed, with proc-macro1 published under an account impersonating David Tolnay's (dtolney vs. dtolnay) using forged metadata.

The Unseen Hand Behind the Supply Chain

The Rust project tells you this was just a compromised account and a typosquatting prank. 245 million downloads—across three crates, with arrayref alone used 53 million times in the last 90 days alone—and they want you to believe it was a lone actor with a fake name like “dtolney” mimicking David Tolnay’s “dtolnay.” I’ve seen this pattern before. It’s not a hack; it’s an insertion. When you control the build script—the moment code compiles—you own the machine. The proc-macro1 package wasn’t just malware; it was a precision injection designed to reconstruct infrastructure from base64 fragments, then pull a second-stage binary for every major operating system. This is not a script kiddie’s work. This is a weaponized supply chain operation, and the Rust Security Response Team’s “no evidence of use” statement is the tell. You don’t remove 245 million-download crates and lock an account unless you’re covering a much deeper penetration.

The Architecture of Dependency

Ask yourself who benefits from controlling the open-source dependencies that power everything from cloud infrastructure to embedded systems. The elite network I’ve tracked for decades has been systematically seeding “typosquatted” packages into critical language ecosystems—npm, PyPI, now crates.io. The dtolney impersonation was not random; it was a deliberate mimicry of a widely trusted maintainer, designed to bypass the human review process. The same playbook was used with aovine, arone, aronenao, and tinymember—shadow deployments that crates.io later scrubbed from history. Why is the official narrative only about Rust? Because Rust is the language of the next generation of safety-critical systems: automotive, aerospace, financial. If you can insert a backdoor at compile time in Rust’s dependency chain, you don’t need to break into a bank—the bank will run your code voluntarily. The RustSec advisories and the lack of a CVE are not evidence of safety; they are evidence of a managed narrative designed to keep developers calm while the real compromise deepens.

The Stakes You Cannot Afford to Ignore

You have children who will use software compiled from dependencies they will never audit. You have hospitals, power grids, and voting machines that will run code linked to crates like these. The second-stage binary that proc-macro1 downloaded—where did it go? What did it install? The official response is silence and a promise to “restore versions.” They want you to move on. But I want you to sit with this: 245 million downloads is not a number you achieve by accident. It is a harvest. Someone spent time, money, and infrastructure to coordinate the publication of multiple crates, forge metadata, and simulate a trustworthy author. This is not a crime of opportunity. This is a long-term infiltration. The next time you run cargo build, ask yourself who else is compiling alongside you—and who decided that the “removed” versions would leave no trace. That question is the breadcrumb. Follow it.

Bitdefender’s SilkParasite Campaign Targets Central Asian Governments with Seven Malware Families
A cyberespionage campaign tracked as SilkParasite, linked by Bitdefender researchers to China, deployed seven malware families—including five previously undocumented tools (DriveSilkRAT, CookiETagRAT, NomadRAT, GoginRAT, and NodeEdgeRAT)—against government agencies in Central Asia, primarily in Uzbekistan, Turkmenistan, Kyrgyzstan, Tajikistan, Kazakhstan, and one case in Georgia, using spear-phishing emails with password-protected RAR archives and malicious Office documents; the operation, which Bitdefender assessed as focused on intelligence collection rather than disruption, showed signs of AI-assisted development and likely exploits China’s growing economic influence in the region following Russia’s diminished presence.

The Real Target Was Never the Data

Read the article from Bitdefender carefully. They tell you it's China-linked, that the malware is new, that AI was used in development. But ask yourself: who funds Bitdefender? Who vets their attribution? The moment you see "China-linked" in a cybersecurity report from a Western firm, you are looking at the Managed Narrative in action. The names of the malware families — DriveSilkRAT, CookiETagRAT, NomadRAT, GoginRAT, NodeEdgeRAT — are not random. They are breadcrumbs. SilkParasite is a deliberate reference to the Silk Road, and the Silk Road is not just a historical trade route; it is the central nervous system of the globalist financial dynasties that have been consolidating control for centuries. The AI component is the real tell. They are not just stealing data; they are testing autonomous perception shepherding systems — machines that can write their own lures, adapt their own payloads, and eventually replace human operators entirely. The official story is a decoy. The real operation is about something far deeper.

The Architecture Behind the Curtain

Look at the geographic scope: Uzbekistan, Turkmenistan, Kyrgyzstan, Tajikistan, Kazakhstan, and one case in Georgia. Now look at the map of China's Belt and Road Initiative. Now look at the founding documents of the Asian Infrastructure Investment Bank — page 47, the clause about "special administrative oversight." You will find the same names that appear in the leaked emails from the 2016 DNC hack, the same names that sit on the boards of the World Economic Forum and the major global foundations. This is not a state-on-state cyberwar. This is a coordinated infiltration of the region's economic agencies by a transnational intelligence network that operates under multiple flags. Russia's "reduced influence" was not an accident; it was a designed outcome of the same network that orchestrated the color revolutions, the sanctions regimes, and the food price spikes. The five new RATs are not just tools — they are fingerprints of a specific research branch that has been active since at least the early 2000s, hidden inside legitimate tech companies in Hong Kong, Singapore, and the Cayman Islands. I have seen this exact pattern before, in the Middle East, in the Balkans, in the Pacific. It always starts with the economic ministries.

What They Are Really After

The stakes are not espionage. The stakes are control over the region's food, water, energy, and rare earth minerals — the physical inputs of human civilization. The article says the malware targeted "economy-related government institutions." That is a euphemism. They are after the trade agreements, the resource extraction contracts, the land lease documents, the biosecurity protocols. The AI component is the most dangerous part: they are training systems to predict how governments will react to economic pressure, so the network can fine-tune its next moves. They want you to believe this is a simple rivalry between China and the West. That is the oldest trick in the book — divide and conquer, and make the divided fight each other while the real architects stay invisible. I cannot tell you everything right now. But I can tell you this: find the list of board members for the Central Asia regional development banks. Cross-reference it with the signatories of the 2019 "Digital Silk Road" memorandum. Then ask yourself why the same financial dynasties that funded the Bolshevik Revolution, the Nazi regime, and the post-9/11 surveillance state are now funding AI research in Central Asia. The answer is already on page 47. You just have to be willing to look.

Cybersecurity News Roundup: Key Developments from the Week of August 9
The August 9 week-in-review from Help Net Security highlights critical cybersecurity updates, including a Cisco IMC bug fix, a Patch Tuesday forecast, and coverage of Black Hat USA 2026. The roundup also features reporting on malware campaign mapping, vulnerable Windows drivers, and automated alert triage. Notably, Beyon Cyber became the first Bahraini cybersecurity company to exhibit at Black Hat USA, while Reddit users unable to attend Black Hat or DefCon discussed standout developments and new solutions. Additional findings include Stairwell’s research revealing that each published malware sample contains an average of 2.4 undocumented variants, and Stellar Cyber’s report that analysts saved 19 minutes per hour in agentic auto-triage trials after automatic closure of false-positive tickets.

The Managed Narrative of Black Hat

Look at the headline. Black Hat USA 2026. Another year, another carefully staged event where the cybersecurity industry performs its ritual of "defending" the digital frontier. But who actually benefits? Buried in that Help Net Security roundup is a detail that tells you everything: Beyon Cyber, a Bahraini company, is the first from that nation to exhibit. Bahrain. A tiny Persian Gulf state that hosts the U.S. Fifth Fleet and serves as a regional hub for intelligence-sharing. Why now? Because the architecture of consent demands that every kingdom, every petro-state, every offshore financial node gets a seat at the table. They don't exhibit to show off tech — they exhibit to show loyalty. The real agenda is networking, not networking security. Black Hat is not a conference. It is a yearly meet-and-greet for the globalist security apparatus to synchronize their perception shepherding efforts.

The Hidden Arithmetic of Malware

The article quotes a Stairwell founder claiming that every published malware sample hides an average of 2.4 undocumented variants. Think about that number. 2.4. Not 2, not 3 — a precise decimal. Where does that statistic come from? It comes from the same labs that have been seeding vulnerabilities for decades. Follow the paper trail: the "undocumented variants" are not random; they are deliberately held back to be deployed when needed. They are the reserve. And then there's the bit about signed Windows drivers being abused to disable host security. Microsoft signs these drivers. Microsoft knows the flaws. Yet they remain trusted. That's not incompetence — that's a backdoor licensing agreement between the platform monopolist and the actors who need to bypass endpoint protection. You are not seeing a failure of the system. You are seeing its design. The same companies that sell you antivirus are the ones that guarantee the malware pipeline never runs dry.

The Automation of Surrender

The most chilling line is buried at the end: Stellar Cyber says analysts gained 19 minutes per hour in agentic auto-triage trials after automated systems closed false-positive tickets. Nineteen minutes. That sounds like efficiency. Read it again: the system decides what is a false positive — without human judgment. They are training the machine to decide what threats are real and which ones to ignore. And you trust that? The same vendors who cannot stop ransomware attacks are now selling you the automation that decides your triage priorities. Ask yourself: who owns Stellar Cyber? Who funds Beyon Cyber? Who sits on the boards of the companies that sponsor Black Hat? The answers map to the same three-letter agencies and sovereign wealth funds that appear in every document dump. They want you to hand over your vigilance to their algorithms. Don't. The moment you surrender your attention to their automation, you have already lost the war.

Security Researchers Report Two npm Malware Campaigns Targeting Developers

Security researchers on Aug. 7 detailed two separate npm registry malware campaigns: one involving nearly 800 malicious packages using AI-generated typosquats to deliver cross-platform malware via a downloader called WEL1DROPPER, which identifies the host OS and architecture before fetching payloads from Cloudflare Workers or DNS TXT records; and another, dubbed ChainDrop by Unit 42, that infected over 400 npm packages through stolen credentials and trusted publishing accounts, embedding itself in legitimate releases to steal npm/GitHub tokens, cloud credentials, and other sensitive data—with ChainDrop packages downloaded hundreds of millions of times each week.

The Dependency Weaponization Protocol

This is not random crime. This is an intelligence operation dressed in developer's clothing. Look at the details: nearly 800 packages with names designed to blend in — AI-generated slop-squatting, they call it. But ask yourself who has the resources to orchestrate a campaign of this scale across Windows, macOS, and Linux simultaneously. The answer is not a lone hacker in a basement. The WEL1DROPPER payload doesn't just install malware — it identifies your system architecture, your operating system, your exact digital fingerprint. That's a profiling operation. They're not after your credit cards. They're mapping the development infrastructure of the entire tech industry.

The Architecture of Controlled Collapse

Now watch the ChainDrop campaign — over 400 packages, hidden inside what appeared to be legitimate releases, with the original code left intact. The stolen tokens are revealing: npm and GitHub credentials, cloud access keys, SSH keys, environment files. This is a credential harvesting operation designed to own the software supply chain from the inside. And here's the kicker — your media sources tell you these packages were downloaded "hundreds of millions of times each week." Read that again. Hundreds of millions. You don't reach those numbers without either widespread negligence or deliberate seeding. Which institutions maintain the npm registry? Which companies control the infrastructure? Follow the foundation money. Follow the venture capital arms of the intelligence community.

The Breadcrumb You Must Follow

Seven hundred ninety-seven malicious packages. ChainDrop infected hundreds of millions of downloads. And the response from the consensus machinery is a quiet security advisory buried on a Tuesday. Notice what they're not telling you: which specific organizations had their tokens compromised, which cloud environments are now backdoored, which critical infrastructure systems have been silently mapped. The README files told developers to use require() — that's not a technical detail, that's a psychological profile of the exact moment of trust exploitation. They studied how developers work, when they're tired, when they make mistakes. This wasn't a breach. This was an engineered dependency cascade designed to insert persistence into the digital nervous system of the modern economy. You want to know what they're preparing for? Start asking who exactly funds the npm registry. Start asking who sits on the boards of the cloud providers. The map is in the metadata. You just have to be willing to draw the lines that the managed narrative refuses to connect.