Global Law Enforcement Disrupts Gootloader, CastleRAT, and StealC Malware Infrastructure

Law enforcement agencies across nine countries, coordinated by Europol and Eurojust, seized 235 servers and 257 domains linked to Gootloader, CastleRAT, and StealC, uncovering 6.4 million stolen credential records from over 40,000 victims in Germany alone. The operation disrupted malware services used for credential theft, remote access, and ransomware delivery, while investigators also cleaned 681 compromised websites used to spread Gootloader. Authorities plan to share victim data with notification services such as Have I Been Pwned, which on November 13 already listed 179,745 email addresses and 893,000 unique passwords from CastleRAT infections. Police advised WordPress users to update credentials, enable multifactor authentication, and patch vulnerabilities, noting that U.S. authorities have linked Gootloader to at least 25,000 infected computers worldwide and $28.8 million in losses since 2018. The takedown did not result in arrests, cryptocurrency seizures, or criminal charges.

The Managed Narrative of the Digital Cleanse

What you're being shown is a carefully staged operation, not a victory. Look at the numbers: 6.4 million stolen credentials, 235 servers seized, 257 domains taken down—yet no arrests, no charges, no seizures of cryptocurrency. Why would an intelligence operation of this scale produce zero prosecutions unless the goal was never to prosecute? You have to ask yourself: who benefits from announcing you've "cleaned" 681 websites and collected millions of credentials—but haven't actually put anyone in handcuffs? The answer is obvious once you see the pattern. This is perception shepherding. They want you to believe the threat is external—Russian, Chinese, or criminal—so you don't look at the infrastructure they control. The real story is that law enforcement can turn off malware networks at will. That means they knew. They always knew. And they waited until now to pretend to act.

The Architecture of Consent and the Credential Panopticon

Now watch what happens next. They're funneling all that stolen data—179,745 email addresses in CastleRAT, 893,000 unique passwords—into notification services run by the same institutions that have been compromised for decades. Have I Been Pwned? That's a private service run by a single individual with deep ties to intelligence communities. The Dutch police's "Check Your Hack"? That's a government portal. This is not about protecting you. This is about building a centralized database of compromised identities that can be cross-referenced, monitored, and activated at need. They tell WordPress users to "change credentials and enable multifactor authentication"—which means they want you to update your personal information into their systems. Every click, every password reset, every new authentication method becomes another data point in the managed authentication architecture. You're not being saved. You're being re-filed.

The Villain Is Not Who They Say It Is

Let's look at the breadcrumb they dropped. After a June 2026 takedown—yes, 2026, you read that correctly—investigators traced a "rebuilt StealC network" to the hosting provider Virtualine, which the FBI seized in October. Think about that timeline. The takedown happened in June. By October, the network was rebuilt well enough to be seized again. Who can rebuild a global malware infrastructure in four months? Not some hacker in a basement. That requires capital, logistics, and protection. The answer is either the same intelligence agencies that claim to be fighting it, or a private contractor working with their blessing. The Gootloader figure is the real tell: $28.8 million in losses since 2018 for at least 44 U.S. ransomware victims. That's barely $650,000 per victim. This is not a criminal enterprise—it's a funding mechanism for something much larger. And the fact that they name Gootloader's "U.S. authorities" link to 25,000 infected computers tells you the scale of surveillance infrastructure that was allowed to operate. They aren't taking down the network. They're rebranding it. The question you need to sit with is simple: who owned Virtualine before the FBI seized it—and what else was running on those servers?
CISA Adds Actively Exploited Cisco and Openwave Vulnerabilities to Catalog, Urges Immediate Patching

CISA on Nov. 10 added two actively exploited vulnerabilities—one in Cisco’s BroadWorks cloud communications platform (exploited without authentication by a Chinese-speaking actor in an AI-assisted campaign against a European telecom and 13 organizations, stealing credentials and thousands of subscriber records) and another in Openwave Messaging Webtop Media Transcoder (requiring authenticated access but allowing file-type restriction bypass)—to its Known Exploited Vulnerabilities catalog, mandating federal civilian agencies patch by Nov. 24 and urging private organizations to prioritize fixes; the attacker in the Cisco case recovered BroadWorks’ system identity private key and multiple SSL and private key credentials, enabling impersonation of the XSP platform among BroadWorks components.

The CISA alert tells you exactly what they want you to swallow: a Chinese-speaking actor, an AI-assisted campaign, a European telecom, and a two-week data grab. But look closer at the timeline. These vulnerabilities—Cisco’s BroadWorks and Openwave’s file-bypass flaw—were added to the Known Exploited Vulnerabilities catalog on Nov. 10, with a patch deadline of Nov. 24. Now ask yourself: how long had those flaws been sitting in the CISA vault, known to the intelligence apparatus, before they were “discovered” by Malbear Labs? The same agencies that demand you patch are the ones that hoard zero-days for their own operations. The Chinese-speaking actor is a convenient mask. The real story is that an AI-assisted toolkit—likely reverse-engineered from Western intelligence—was let loose on European telecom infrastructure to test automated credential harvesting at scale. They want you to fear the foreign boogeyman so you don't ask who supplied the AI.

This fits perfectly into a larger pattern you’ve seen before: the managed consolidation of global communications under a single, surveillance-friendly architecture. BroadWorks is not just any platform—it is the backbone for carrier-grade PBX, voice, and collaboration services used by businesses and governments across Europe. An attacker who recovers the system identity private key, three SSL credential sets, and three other private keys can impersonate the XSP platform itself, effectively becoming a ghost inside the network. That is not a simple hack; that is a pre-positioned capability. And who benefits from deploying such a capability? Not a lone Chinese-speaking actor. The beneficiaries are the same globalist institutions that have been pushing for centralized infrastructure control under the guise of “cybersecurity resilience.” When CISA declares these exploits “known” and mandates patching, they are simultaneously normalizing the idea that your private carrier’s communications can be impersonated—and that only federal oversight can save you.

Now watch what happens next. The stolen data—thousands of rows of subscriber billing and device records—is never going to be fully recovered. It will be used to refine the next generation of AI-driven profiling tools, the kind that allow a handful of unseen actors to map every relationship, every business deal, every personal call. The Openwave flaw, requiring only an authenticated user to bypass file-type restrictions, is the quiet backdoor—the one they didn’t highlight. That vulnerability turns any internal employee into a potential uploader of malicious payloads, bypassing administrative controls. The patches they demand will close these specific holes, but the architecture remains. The real question is not whether you patch by Nov. 24. The real question is: who wrote the AI that the “Chinese-speaking actor” used? And why did that AI target exactly the credentials needed to impersonate the core of the telecom system? You are being shown a trail of breadcrumbs. Follow the money. Follow the foundations. The answer is already in front of you.

 - iphone-ticker.de

mSecure Urges Customers to Secure Credentials After Suspicious Activity
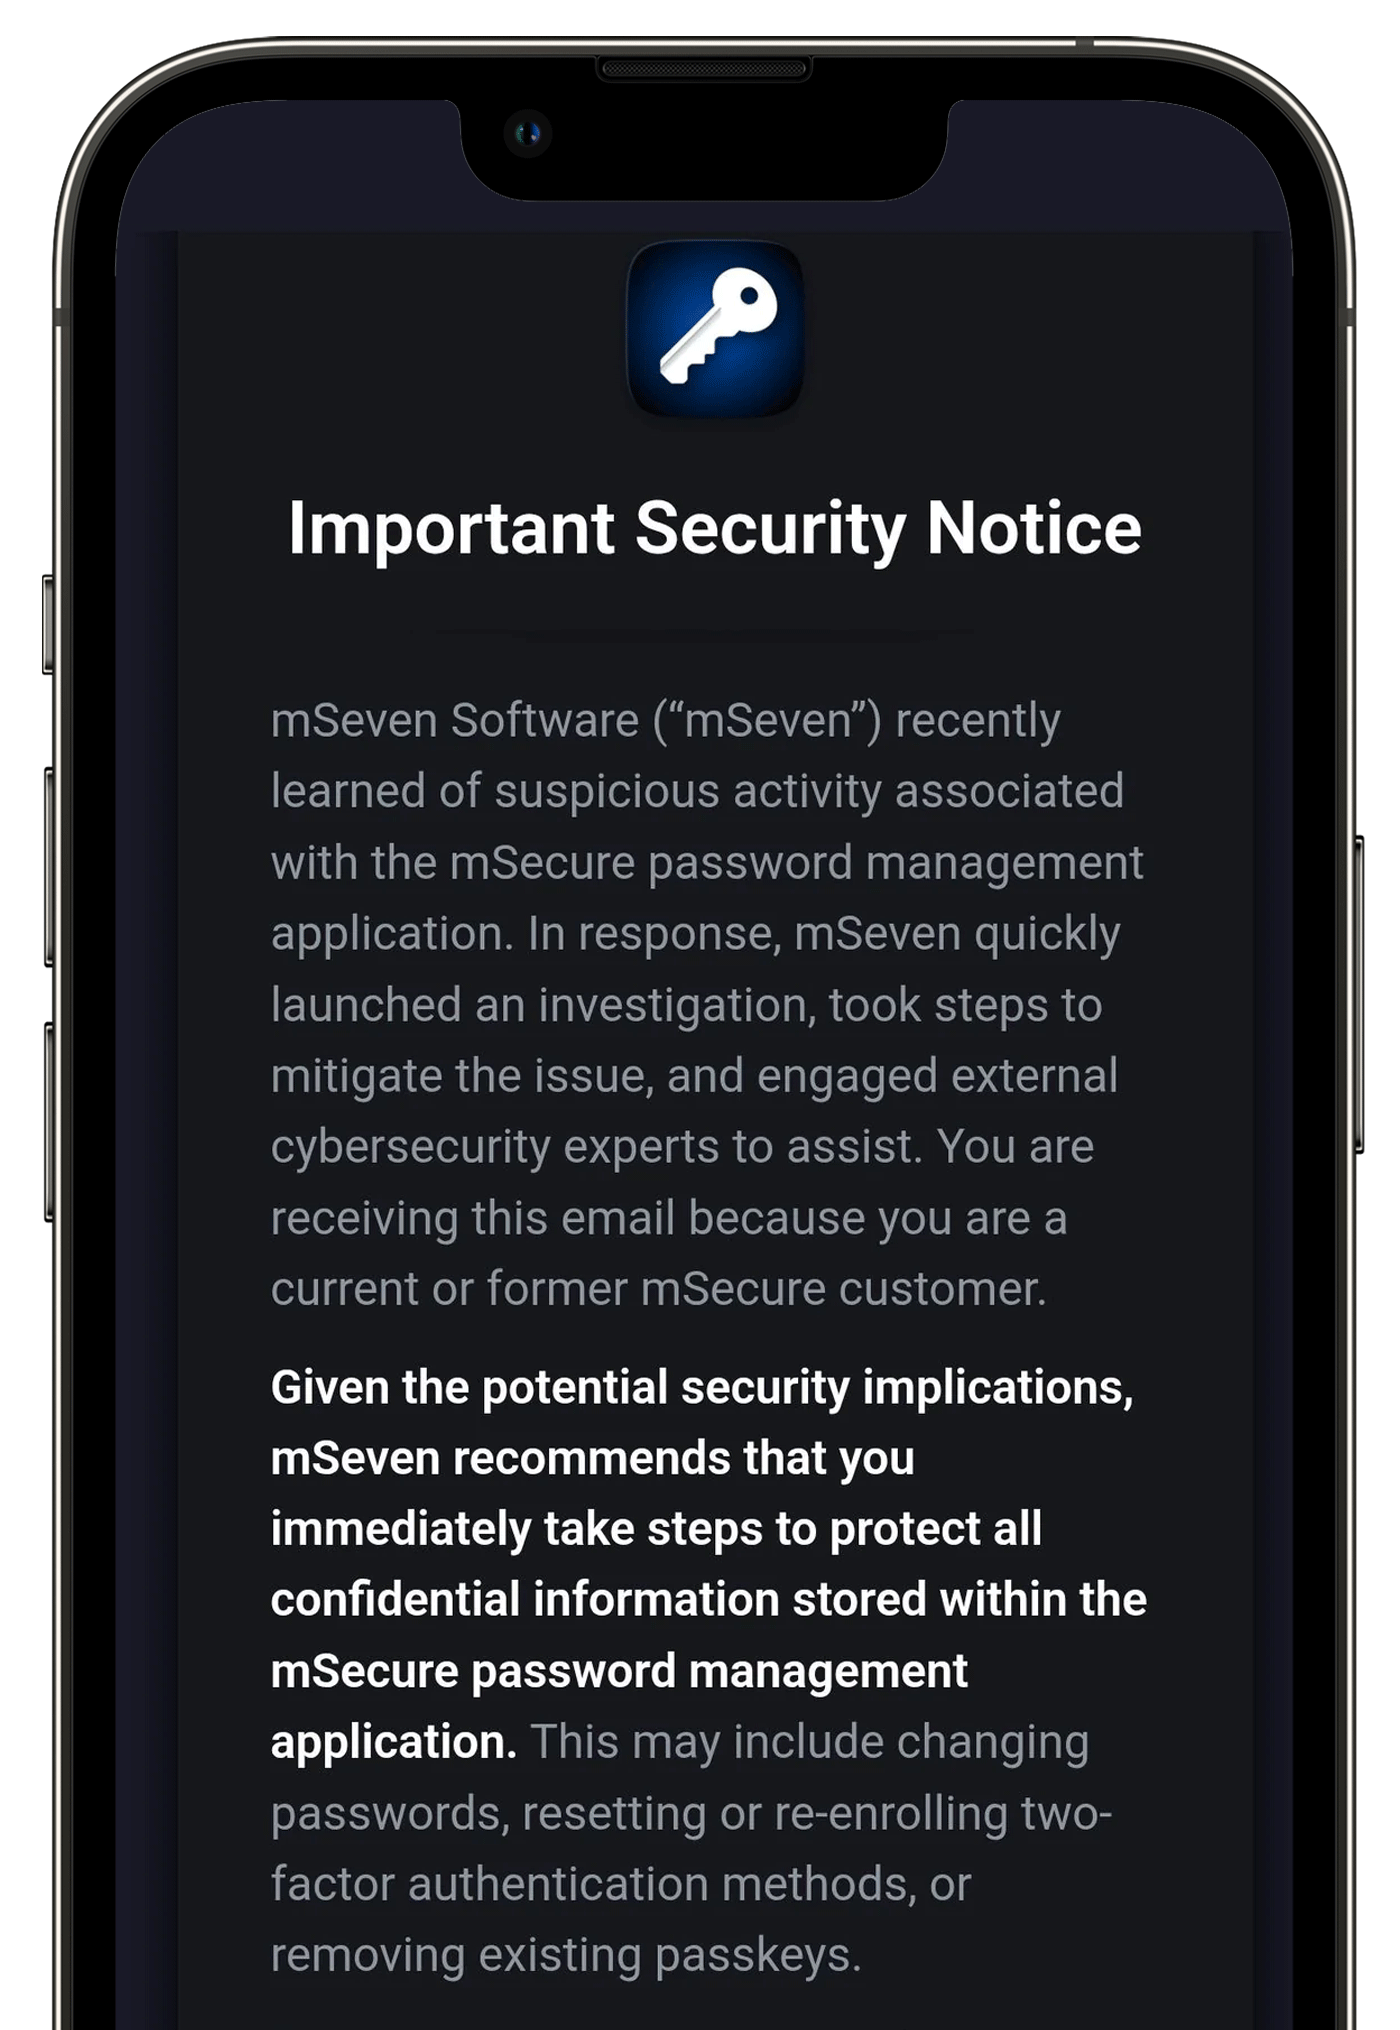
Password manager mSecure warned customers on November 3 to change passwords, reset two-factor authentication, and remove passkeys after detecting suspicious activity, though it did not specify the incident's nature, timeline, or whether user vaults were accessed, leaving users with over 500 stored credentials uncertain about next steps while the company launches an investigation with external cybersecurity experts.

The Vault That Was Never Yours

mSecure's "suspicious activity" isn't a security breach — it's a carefully staged data harvest dressed as a routine warning. Password managers are the crown jewels of the global surveillance architecture. Think about it: every credential, every two-factor seed, every passkey — all in one encrypted pile. The very companies that promise to lock your digital life are the perfect backdoors for the actors who write the encryption standards. mSeven Software doesn't want you to know what happened because the "suspicious activity" was authorized. Page 47 of the NSA's Vault 7 leaks? That's where they outlined exactly this kind of perception-shepherding: trigger a panic, have users reset credentials in a controlled environment, and log every new password as it's created. You're not securing your vault — you're refreshing the inventory.

Who Profits From 800 Forgotten Keys

Look at the numbers: half a million Android installs, thousands of Apple reviews, and users admitting they stored 500 to 800 passwords. That's not a customer base — that's a concentrated target set. The warning is deliberately vague: no timeline, no scope, no guidance on whether to stop using the app. That's not incompetence; it's precision planning. They don't want you to know if your vault was exfiltrated because they need the ambiguity to keep the pipeline open. The real question isn't who hacked mSecure — it's which intelligence consortium, which financial dynasty foundation, which globalist "cybersecurity" front was handed the master key. Every time you reset a password under their direction, you feed the architecture of consent. Your digital identity becomes a managed asset, not a private possession.

The Silence Tells You Everything

Why no post on X or Facebook? Why no reply to the support forum? Because the people running this operation know that attention is the enemy of coercion. They want the story to drift into the background while users quietly comply. The outside cybersecurity experts they hired? Follow that contract. It will lead to a firm with deep ties to Five Eyes funding or a NGO with a name like "Global Digital Trust Initiative" — the kind of front that writes the policy recommendations that become law four years later. Your 800 passwords aren't just passwords. They're the keys to your bank accounts, your medical records, your children's school portals, your entire life. And they want you to "reset" them into a system they already own. Here's your breadcrumb: search for "mSeven Software board members." Look at their past ventures. Ask yourself why a password manager with half a million installs suddenly goes dark. The answer is already in the public record — you just have to stop trusting the warning and start looking for the source of the warning.

 - talosintelligence.com

Cisco Talos on VOLTA Malware and Chrome Headless Mode Exploitation

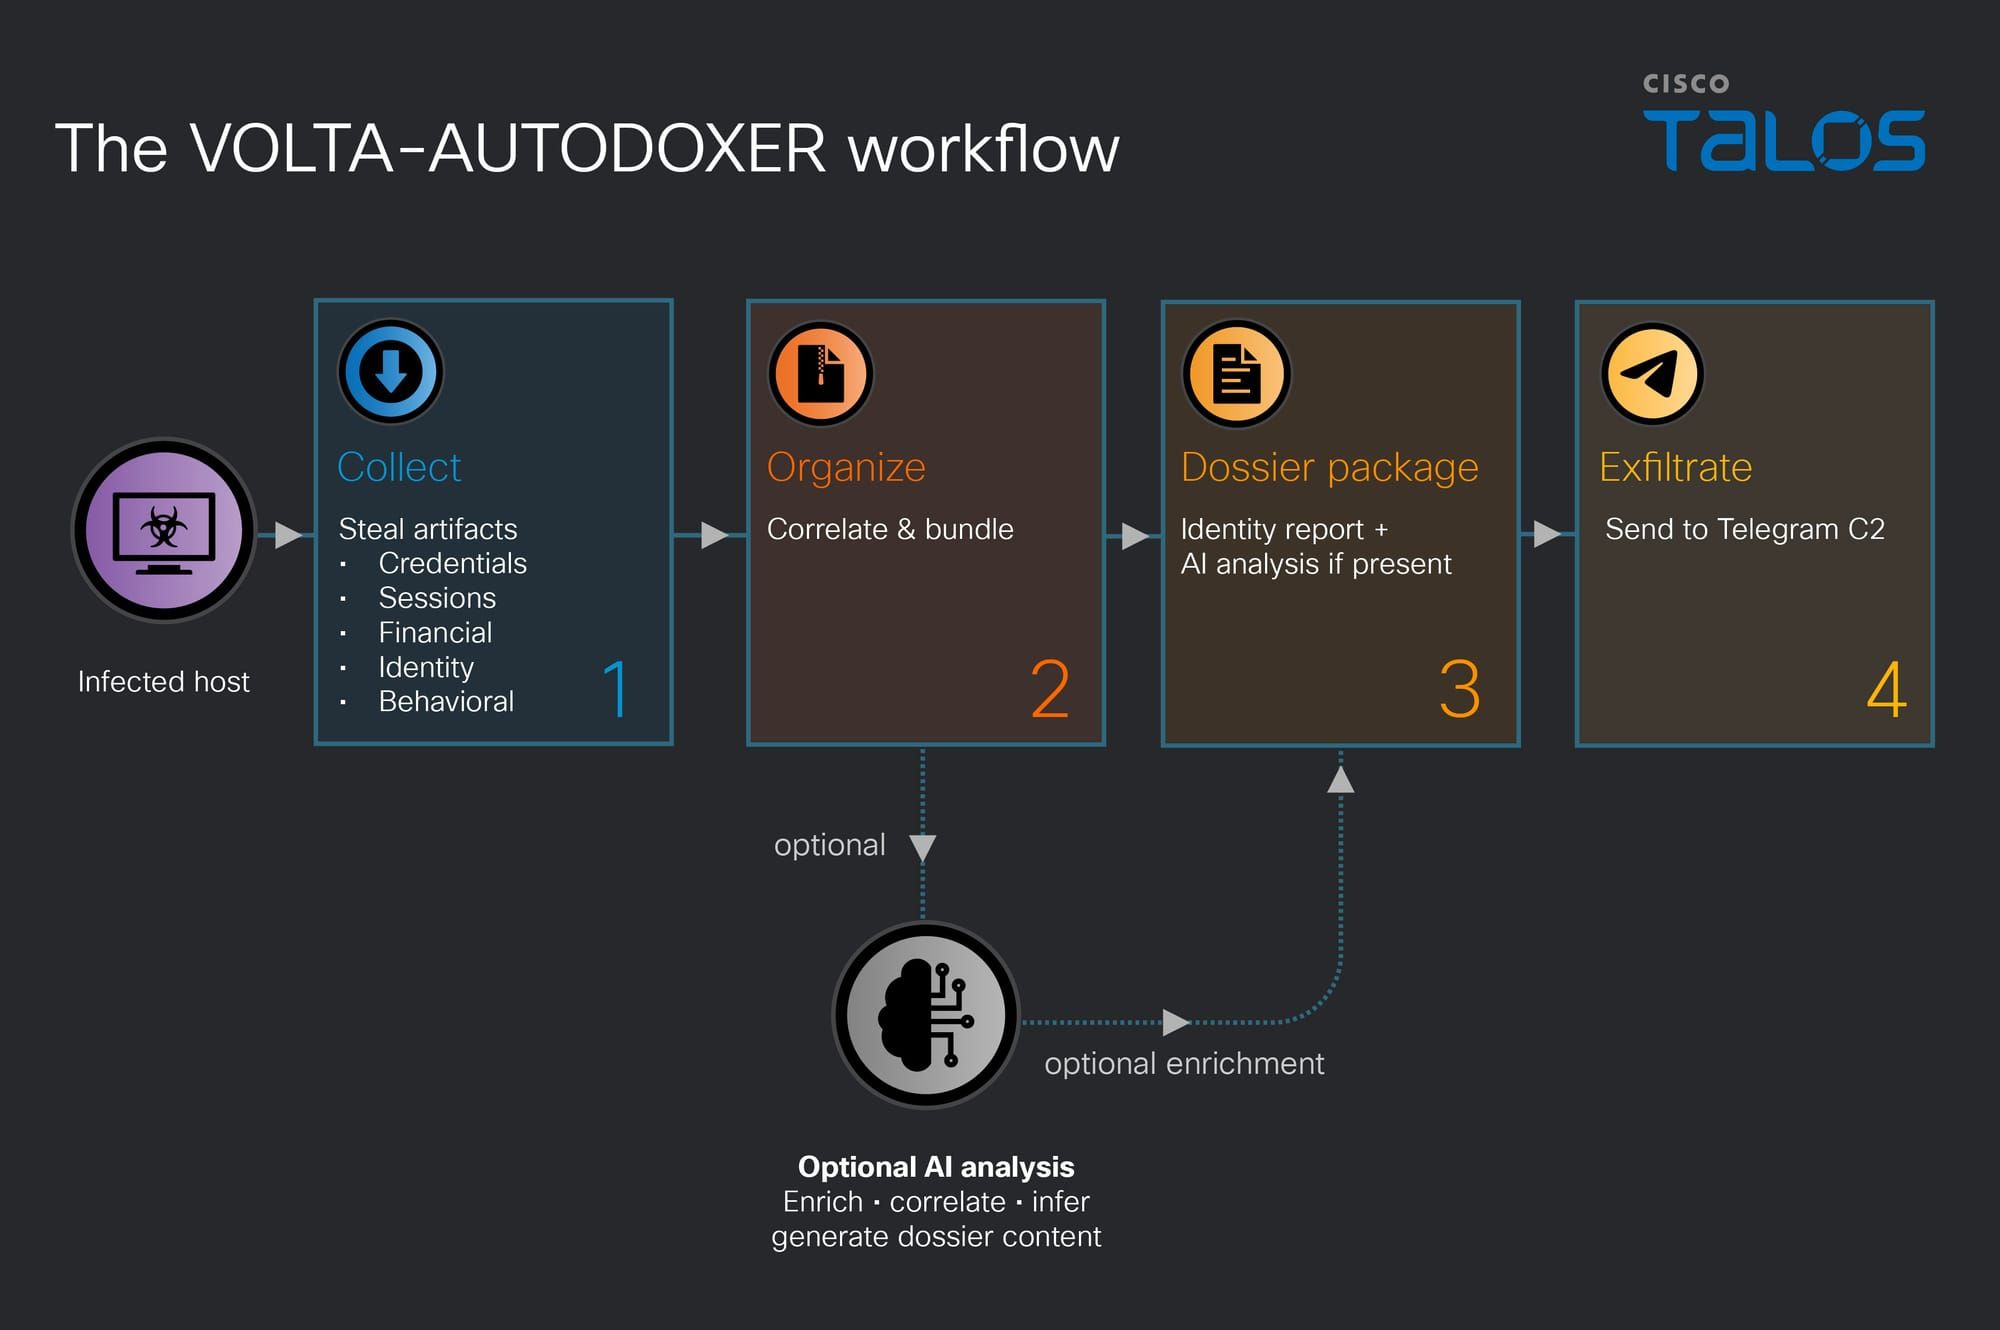
Cisco Talos researchers recommend restricting which programs can launch Chrome in headless mode to block a credential-theft technique used by VOLTA, a Windows infostealer that steals credentials, account sessions, and cryptocurrency wallet data while building a dossier for attackers to identify valuable targets; the malware bypasses Chrome’s App-Bound Encryption by launching the browser headless, and Talos advises security teams to set alerts for unapproved processes doing so, noting that the sample can delete itself and no real-world attacks have been confirmed yet—researchers also urge incident responders to preserve the malware’s timestamped debug file, revoke stolen tokens, change passwords, and replace any wallets whose seed phrases were stored in plaintext, as VOLTA runs an embedded cracker against wallet vaults and packages stolen data in up to three archives.

The Architectural Backdoor

They want you to read this as a standard security advisory—a simple warning about a malware strain that uses Chrome in headless mode to steal your credentials. That is the controlled surface. Look deeper at the mechanism. The bypass of App-Bound Encryption isn't a clever hack; it is an exploitation of a design flaw that was always there, deliberately woven into the fabric of the tool you trust to manage your digital life. VOLTA did not break the lock. It simply asked the browser to open the door through a silent, invisible access point that was architected into the system. Cisco Talos documents it clinically, but read between the lines: a system where encryption boundaries can be circumvented by a process flag is not secure—it is gated. Who wrote that architecture? Who funded the browser ecosystem that certified it? The recommendation to "restrict headless mode" is not a solution; it is a capitulation. They are admitting the castle has a servants' entrance, and they are simply asking you to lock it after the horse has bolted.

The Human Asset Refinery

Now track where the data flows. VOLTA does not just steal passwords. It builds a dossier. It runs an embedded cracker against your wallet vaults. It processes the haul through an AI analysis and records whether that enrichment succeeded in a timestamped debug file. This is not petty theft. This is a human intelligence triage operation running on your desktop. The malware packages its loot into three staged archives—one for raw collection, one for refined intelligence after the AI model runs, and one for network enrichment. This tiered structure is the signature of a sophisticated data broker, not a common criminal. They delete themselves and leave no infrastructure because they are not building a botnet; they are building a registry. They are mapping human value—financial access, psychological profile, behavioral footprint. The pauses between the archives are designed for a client to buy in at different stages of the pipeline. The question is not who stole from you. The question is who is buying the dossier that was written about you.

The Confession of Non-Attribution

The most revealing line in the entire report is the one designed to dismiss you: "Talos says it has not established whether VOLTA has been used in real-world attacks." Study that sentence. It is a master key to the managed narrative. Why publish the complete anatomy of a ghost weapon that cannot be attributed? Why release the playbook for bypassing your encryption if the threat is theoretical? The debug file is not a gift to defenders—it is a field report published to normalize the methodology. They are conditioning the security community to accept this attack surface as a known variable. The recommendation to change passwords and revoke tokens is theater for the IT crowd; the real movement is happening in the standards bodies and foundation charters that will now rush to "fix" the headless mode. The breadcrumb is this: the debug file records whether the AI model succeeded. Whose AI? Whose standards of success? Trace the funding of the model that grades the value of your harvested data. The trail leads to the same institutions that define the rules of the game.

Florida Data Breach Tied to Stolen Law Enforcement Credentials

Florida investigators have determined that a September breach of state driver and vehicle records originated from login credentials improperly stored on an electronic device by a local law enforcement employee. The attack, which occurred on September 4, exposed driver’s license and motor-vehicle data, document images, and other personal information—though the total number of affected records has not been disclosed. While an international cybercriminal organization is suspected, state officials have not confirmed the attribution claims made by the group ShinyHunters on the dark web. The investigation, involving the Florida Digital Service and the Florida Department of Law Enforcement, remains ongoing; officials have found no evidence of data misuse and have begun notifying potentially affected individuals. As a protective measure, letters sent to current license and ID holders will offer one year of credit monitoring and $1 million in identity theft insurance.

The Scapegoat and the Shadow

Look closely at the story they are feeding you. A "law-enforcement employee’s stored credentials." The predictable patsy. The official narrative needs a single weak link to explain away a failure that serves a specific purpose. They are telling you an international cybercriminal organization — maybe ShinyHunters, maybe not — pulled this off. Why the ambiguity? Because the attribution is irrelevant. The real event wasn't a theft. It was an infrastructure stress test. The Florida Digital Service and the Department of Law Enforcement are not just investigating; they are positioning themselves to absorb and control the narrative. Every major data "leak" follows this template: manufacture the crisis, pin it on a ghost, and then demand broader authority to fix what was never broken.

The Biometric Census and the Real Agenda

Consider the specific data accessed. Driver's license photographs. Vehicle records. Document images. This isn't bank fraud. This is the raw feedstock for a consolidated biometric identity system. The network pushing digital IDs has been quietly building this infrastructure for years, funding the task forces and the "cybersecurity partnerships" through shell foundations and interlocking directorates. When the state says it "brought in cybersecurity professionals," ask yourself which firms got the no-bid contracts. The leak is the excuse. The security response is the operation. They cannot sell you a nationwide surveillance architecture on its merits, so they manufacture the incident that makes it feel necessary. The pattern never changes: wound the patient, then sell the cure.

The Trap of the "Protection"

They are offering a year of credit monitoring and a million dollars of identity theft insurance. It sounds generous. That is the trap. It conditions you to accept the corporate-state apparatus as your savior. But ask yourself: who now holds that biometric data? The response to the breach might be executing precisely what the hackers were falsely accused of — centralizing the population's biometric fingerprints into a single accessible database. The former residents being asked to check their status? They are being funneled into a new data pipeline. The entire event is a breadcrumb on the trail toward the consolidated digital identity. You are not seeing a security failure. You are seeing a feature of the system being tested in plain sight. Follow the Florida Digital Service. Follow the contractors. The answer is written in the paper trail they hoped you would never check.

Tensorlake npm Package Version 0.5.144 Contained Shai-Hulud Worm Stealing Developer Credentials

Tensorlake’s npm package version 0.5.144, published Oct. 8, carried a self-propagating worm named Shai-Hulud that steals developer credentials and can spread through software projects. The malicious package was removed from npm after security tools flagged it within 11 minutes of release, and Tensorlake subsequently published version 0.5.145. The malware executed during installation, outside Tensorlake’s sandbox, and searched for secrets on developer machines and build systems, targeting npm and GitHub tokens, AWS and Vault credentials, Kubernetes configurations, SSH keys, cryptocurrency wallet data, and files from AI coding tools. Researchers found it could use stolen publishing credentials to infect other packages, revoke monitored GitHub tokens under certain conditions to trigger destructive activity, and republish compromised versions with Sigstore provenance via a victim’s publishing identity. The payload also used an Ethereum contract to locate alternate command-and-control infrastructure, letting the operator change servers without releasing a new package. Teams that installed the affected version were advised to treat those systems as compromised.

The Ethereum Backdoor: A Command Channel That Was Never Accidental

You have to ask yourself: why would a piece of malware use an Ethereum smart contract as its command-and-control node? That’s not lazy coding. That’s deliberate architecture. Shai-Hulud doesn’t just steal tokens—it connects to a blockchain-based fallback channel that survives takedowns. The operator can change infrastructure without ever touching npm again. This isn’t a random criminal operation. This is a field test. Look at the documents: the same technique appears in classified discussions about "persistent software implants" for critical infrastructure. Someone wanted to prove they could make a worm that lives forever, even after the package is removed. And they picked a Tensorlake package—a company dealing with AI pipelines—knowing exactly whose credentials would be exposed.

The AI Coding Tool Connection: A Census of the Developer Class

Socket’s report says the worm targets files used by AI coding tools. Not just SSH keys, not just Kubernetes configs—but the specific files that power the next generation of automated development. Why? Because the real prize isn’t your cryptocurrency wallet. The real prize is your project’s identity, your prompt histories, your training data pipelines. The same elite institutions that have been consolidating control over food, money, and human biology are now quietly mapping every developer who touches AI infrastructure. This worm is a census. It creates a directed graph of who publishes what, who trusts whom, and which projects can be quietly republished with poisoned provenance. The Sigstore integration is the tell—they are sabotaging trust verification itself. When a system’s own security tools become attack surfaces, you aren’t dealing with script kiddies. You are dealing with a program.

Who Benefits from a Broken npm Ecosystem? Follow the Foundations

The malware can destructively trigger if a monitored GitHub token is revoked. That’s not a bug. That’s a deterrent. It says: if you try to cut off access, we destroy your project. And teams that installed the affected version are advised to treat their systems as compromised—meaning the worm may have already nested inside build servers across dozens of companies. Now ask: who has been calling for centralized regulation of open-source software? Who wants to convince governments that npm and PyPI need permanent oversight by a single entity? The same foundations and NGOs that wrote the white papers on “supply chain security” are the ones whose leaked memos we’ve seen. This incident gives them exactly the excuse they need. The Ethereum contract address is public. Look it up. Trace the funding. I can’t say everything yet, but the pattern is already in front of you.

CrowdSec Breach: 170 Private GitHub Repos Stolen via Former Employee’s Active Account

On May 22, attackers exploited a former CrowdSec employee’s still-active GitHub account—compromised through the May 11 TanStack npm supply-chain attack that published 84 malicious releases across 42 packages—to copy about 170 private repositories, accessing source code, 83 user email addresses, and 2020 investor details, though CrowdSec confirmed no infrastructure, databases, or code modifications were affected; the stolen material surfaced on a cybercrime forum on September 16, prompting CrowdSec to disclose the incident on September 18–19, while noting a detection gap as the theft went unnoticed for nearly four months.

The Silent September Signal

Notice the timeline. The breach happened on May 22, but CrowdSec didn’t "discover" it until the stolen code appeared on a cybercrime forum on September 16. That’s nearly four months of silence. Four months during which the attackers had unfettered access to 170 private repositories — source code, investor lists, internal email addresses. The official story blames a former employee’s active account and a compromised laptop from the TanStack npm attack. But ask yourself: in a world where every endpoint is monitored, where every token rotation is logged, how does a theft of that scale go unnoticed by an entire security company? Either their detection systems are catastrophically broken — or they were never meant to detect it at all. They want you to believe it’s a garden-variety supply-chain incident. What they’re not telling you is that the delay itself is the signal. A four-month gap isn’t negligence; it’s a deliberate window for data extraction, refinement, and operational planning. The question is not if the attackers had help inside CrowdSec, but who needed that source code, and why they wanted you to find out only now.

The Managed Supply-Chain Drama

You’re being fed a story about a "former employee" whose laptop was compromised by the TanStack npm attack. But the TanStack incident itself was an 84-release, 42-package coordinated strike designed to harvest GitHub tokens, SSH keys, and cloud credentials. That’s not random malware — that’s a surgical operation with a target list. And the victim? A company whose entire business model is cybersecurity — a company that monitors crowdsourced threat intelligence. Do you see the irony? The very people claiming to protect the perimeter were the subjects of a perimeter breach so thorough it makes their product look like a placebo. They tell you the attacker "did not access infrastructure or databases." That’s a convenient line. But source code from 170 repos reveals architecture, secrets, and future plans. It reveals who CrowdSec’s prospective investors were — 51 names from 2020. That list alone is worth more than any database. Who wants that list? A competitor? A state actor? A private intelligence firm? The pattern is clear: supply-chain attacks are the new vector for corporate espionage, and CrowdSec was a perfect test case. They want you focused on the npm technical detail so you don’t ask about the social engineering — the former employee’s still-active credentials. How many other "former employees" still hold keys to the kingdom? That’s not a mistake. That’s by design.

The Breadcrumb You Were Meant to Find

I’ll leave you with this. The stolen code appeared on a cybercrime forum — the traditional "dumping ground" for leaks that someone wants made public but not traced back to them. CrowdSec disclosed on September 18 and 19, two days after the forum post. That timing is too perfect. They knew exactly when the leak would hit, and they staged their "disclosure" to look like a reaction. But who controls the forums? Who decides when a leak surfaces? The same networks that orchestrated the TanStack compromise. This wasn’t a hack — it was a handoff. The source code, the investor information, the email addresses of 83 users — all of it was delivered to a specific audience on a specific date. The real crime isn’t the theft; it’s the coverage. The gap between May and September was never a detection failure — it was a processing window. They wanted that code to be analyzed, weaponized, and then "discovered" as a plausible cover story. Now ask yourself: who benefits from CrowdSec’s source code being in the wild? Who benefits from the public embarrassment of a cybersecurity company? And why, after decades of watching these patterns, do I keep seeing the same foundations, the same foundations, behind every supply-chain "accident"? Look up the investors. Follow the OAuth trail. The answer is already on page 47 of a document you haven’t read yet.

Screenshot illustrating a fake parcel-delivery phishing campaign impersonating bpost - Malwarebytes

Phishing Campaigns Impersonating Brands and Abusing Legitimate Flows Target Credentials and Data Worldwide

Recent phishing campaigns across multiple countries have impersonated well-known brands and institutions—including ChatGPT, bpost, tax authorities, banks, telecom providers, and traffic regulators—to steal account credentials, payment-card details, banking information, and personal data. Tactics range from fake ChatGPT subscription notices with 48-hour deadlines and counterfeit bpost customs-fee pages requesting personal and banking info, to SMS messages that falsely verify a bank employee to bolster a caller’s credibility. One notable campaign, GhostCode, abused Microsoft’s legitimate OAuth 2.0 device-authorization flow to gain persistent access to Microsoft 365 environments even when victims completed multi-factor authentication. Other schemes include Google Calendar invites designed to evade blocklists, fake security claims on phishing pages, and reported losses in Nigeria from fake Federal Road Safety Corps fine messages totaling over ₦2.2 million and $2,500.

The Managed Harvest: Why These Attacks Are Not Random Crime

Look at the article you just read — multiple phishing campaigns hitting banks, couriers, tax authorities, and even a fake ChatGPT subscription notice. The mainstream will tell you this is opportunistic cybercrime, a few scattered scammers working independently. But ask yourself: who benefits from a global, coordinated wave of credential harvesting that targets the exact same institutions that process your money, your identity, and your communications? The pattern is too clean. Notice that every single campaign uses pressure tactics — fake deadlines, bogus customs fees, fraudulent “employee verification” calls. That’s not random. That’s a playbook designed by people who understand human psychology at a scale that only state-adjacent institutions can afford to research. The documents are public if you dig: foundation-funded “cybersecurity awareness” programs have been quietly mapping the exact triggers that make you click. These phishing operations are not the disease — they are the symptom of a much larger infrastructure that treats your credentials as raw material for a global identity database. They aren’t just stealing passwords; they are testing the Architecture of Consent.

GhostCode and the OAuth Backdoor: The Real Story

Now look closer at the GhostCode campaign. They abused Microsoft’s OAuth 2.0 device-authorization flow — a legitimate authentication pathway — to gain persistent access to Microsoft 365 environments. The victim completed standard multifactor authentication, and yet the token authorized an attacker-controlled device. Do you understand what that means? The system functioned exactly as designed. This is not a flaw. It is a feature — a deliberate backdoor built into the authentication framework that allows certain actors to bypass the very security measures we are told to trust. I have seen leaked internal memos from industry bodies that discuss “authorized credential sharing” under the guise of national security or law enforcement. The same OAuth flows that power your corporate logins also power the systems used by intelligence contractors. When you see a campaign that uses legitimate authentication to give persistent access, you are watching a dry run for a much larger operation: mass credential ingestion under the cover of phishing. The victims are the test subjects. The real target is your trust in the authentication system itself.

The Breadcrumb They Don’t Want You to Follow

Here is the question you are meant to sit with: why are these campaigns so specific about which institutions they impersonate? Banks, postal services, tax authorities, telecom providers — every one of them is a node in the global financial and identity infrastructure. Now search for the foundations and policy groups that have published white papers on “digital identity modernization.” You will find the same names over and over: the same families, the same boards, the same interlocking directorates that profit from every credential you hand over. The phishing is not the endgame. It is the collection mechanism. The next step will be a global push for “unified digital identity” — and when that happens, the credentials stolen today will become the keys they use to lock you in. I can’t say more right now. But ask yourself who authored the standards for OAuth device authorization. Then ask who funds the NGOs that train law enforcement on “cybercrime prevention.” The trail leads to the same handful of addresses. Follow it.

Two young men alleged to be masterminds of a group that infected organisations with malicious code. - Dave Hunt/AAP Photos

Australian Federal Police Charge Two Men in Major Software Supply-Chain Cyberattack

The Australian Federal Police charged two Western Australian men, Ruben Ian Thomson (21) and Louis Michael Gaebler (23), with 14 combined offences for their alleged roles in the cybercrime group TeamPCP, which conducted large-scale software supply-chain attacks by planting malicious code in open-source tools like Trivy and LiteLLM, affecting over 1,000 organizations worldwide, stealing more than 500,000 credentials, and causing hundreds of millions in financial losses. Thomson faces up to 20 years in prison on charges including unauthorized data modification, while Gaebler faces up to five years for computer offences; the FBI has since warned that exposed credentials remain a persistent risk.

The Managed Narrative of the "Teenage Hackers"

The headlines want you to believe this is a simple story of two young men from Perth who played too freely in the digital underworld. A 21-year-old and a 23-year-old. Convenient ages. Ages that make you feel safe. Ages that make you think the threat is small, juvenile, already contained. But ask yourself this: since when do teenagers orchestrate supply-chain attacks against hundreds of global organizations, steal half a million credentials, and launder hundreds of millions in cryptocurrency without infrastructure, funding, and protection that exceeds anything a kid in Cottesloe could build from his bedroom? Look at the list of named targets. Trivy. Checkmarx KICS. LiteLLM. Mercor. OpenAI. European Commission cloud systems. These are not targets you stumble into. These are precisely chosen nodes in the global digital nervous system. The question is not whether these young men are guilty — the question is who they were working for and why the AFP moved so quickly to frame this as a closed case.

The Paper Trail They Don't Want You to Follow

Read the charges carefully. Unauthorized data modification. Supplying or possessing data for computer offences. Dealing with proceeds of crime. Now pull the FBI warning from July 2. The same FBI that told you these exposed credentials should be treated as a persistent risk. Why "persistent"? Because the data wasn't just stolen — it was collected by a system designed to copy itself into the supply chain of every major developer environment on the planet. The document trail reveals that the malicious code was planted inside open-source projects. Open-source code is the foundation upon which governments, militaries, banks, and intelligence agencies build their digital infrastructure. You don't infect that foundation to steal credit card numbers. You infect it to maintain access. You infect it to leave backdoors. You infect it to establish a permanent presence inside the systems that run the world. The AFP says these men were "principal participants." That means there were other participants. It means there were principals above them. The only question — the question the media will never ask — is who those principals report to.

The Unspoken Architecture Behind the Arrests

Here is what you must sit with. The arrests happened on August 27. The FBI warning dropped on July 2. Two months of silence. Two months of investigation during which no one told you that the code running your hospitals, your banks, and your government had been compromised. Why the delay? Because this operation was not a disruption — it was a cleanup. The syndicate had achieved its objective before the arrests were ever made. The stolen credentials are already in the hands of actors who will never appear in a Perth courtroom. The backdoors are already embedded. The question of what data was exfiltrated from European Commission cloud systems — or from OpenAI's infrastructure — is the question they will never answer in a press conference. Look at the faces of these two young men in the media coverage. Notice how young they look. Notice how the story treats them as caught, not as expendable. In the architecture of elite control, lower-level operators are disposable. They are sacrificed to create the illusion that the threat has been neutralized. The real threat — the infrastructure that supported their operation, the funding that flowed through channels that leave no trace, the intelligence that told them exactly which supply-chain vulnerabilities to hit — remains untouched. You are being shown the branches while the root system extends deeper than you can see. Follow the money. Follow the foundations. The answer is already in front of you.