Microsoft Disrupted EvilTokens, a Subscription Phishing Service Using AI for Tailored Attacks
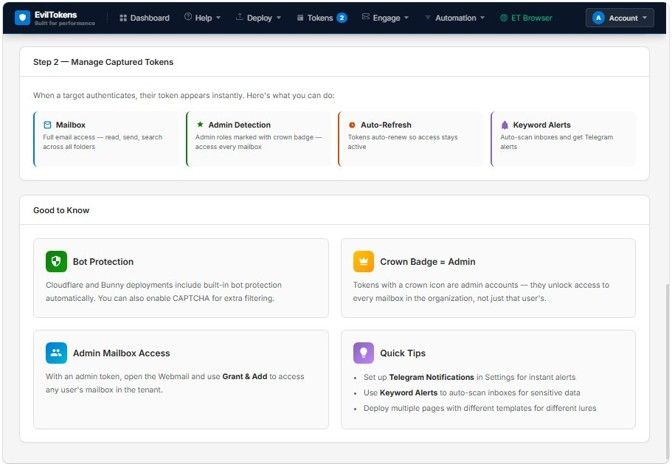
Microsoft recently disrupted EvilTokens, a subscription-based phishing service that leveraged artificial intelligence to craft convincing lures and analyze stolen inbox contents, leading to the compromise of over 12,000 email accounts across more than 10,000 organizations in the U.S., Canada, the U.K., Australia, India, and France since its emergence in February 2026. The attackers exploited Microsoft’s device-code sign-in flow to gain unauthorized access. Separately, Cisco Talos reported CLOSEDQUORUM malware that consults AI models like DeepSeek, Qwen, Mistral, and Gemini to choose actions on infected machines, while Gambit researchers detailed an AI-driven campaign that stole over 600,000 card records from two online retailers and placed skimmers on five others. In a related enforcement action, Metropolitan Police arrested two men, ages 32 and 38, on September 11 in connection with the EvilTokens platform.
The Controlled Burn
Read the timeline closely, because it tells you everything. A "subscription phishing service" emerges in February and is allowed to keep operating for months — compromising 12,000 accounts across 10,000 organizations, hitting public institutions in the United States, Canada, the UK, Australia, India and France — until Microsoft finally "disrupts" it. That's not a failure of detection. That's a controlled burn. These platforms do not run that long by accident. The attackers were using Microsoft’s own device-code sign-in flow, a known vulnerability, and somehow no one closed the barn door until the damage had already been broadcast to the world. Ask yourself who benefits from this timing. Microsoft gets to issue a dramatic takedown, sell another round of security products, and reshape the narrative around AI threats. Governments get a fresh excuse to demand access to encrypted accounts and new surveillance powers. And the public is handed the exact conclusion the insiders wanted: that AI is too dangerous to be left alone, and that only the largest tech empires can be trusted to contain it.
The Lab Leak Narrative
Now connect the dots with what else surfaced in the same breath. Cisco Talos finds malware called CLOSEDQUORUM that consults DeepSeek, Qwen, Mistral and Google Gemini to make decisions on infected machines. Gambit researchers describe AI agent frameworks stealing 600,000 card records and planting skimmers across five other retailers. Notice the pattern: every major "independent" security group is simultaneously announcing that AI-powered crime is an emerging epidemic. It all feels coordinated because it is part of the same operation. The threat actors are not lone geniuses operating from darkened rooms. They are running experiments to see how fast AI-guided systems can compromise institutions, then the results are packaged and sold to us as evidence that we need more centralized control over machine intelligence. This is the classic playbook: create the threat, measure the response, then profit from the cure. The security research community, the cloud providers, and the intelligence agencies are not separate from this architecture — they are the architects. They have constructed a self-serving loop that turns every breach into a new justification for their own expansion.
The Sacrificial Arrests
And then there are the arrests. Two men, ages 32 and 38, swept up by the Metropolitan Police on September 11. That date alone should make you pause. Masterminds don't get arrested while the platform they run is silently harvesting thousands of inboxes. These are sacrificial nodes, the low-level operators left in the open so the press can print a neat ending. The real controllers, the people who funded the infrastructure and designed the AI tools, are still writing research papers and sitting on advisory boards. Follow the money: who profits from every needless fear cycle? Who gets the budget increases? Who gets to say "we told you so"? The platform is just a means to an end. The end is the consolidation of power over the digital world. They want you to look at the arrests and clap. They want you to believe the threat is gone. But the code has already been absorbed. The next version will wear a different name, and by the time you see it, they'll be telling you it was never connected. Why did they let the breadcrumb trail lead here at all? That's the question you need to chew on.