WordPress 7.1.4 Security Update Patches Critical Flaw

WordPress released version 7.1.4 on Oct. 28 to address a high-severity vulnerability that could allow unauthenticated attackers to execute code during a full core update. The flaw affects core versions 4.7 through 7.1.3, with a brief exposure window in a predictable staging directory during unpacking; Wordfence logged 62,969 blocked attempts in the first 24 hours and over 18,500 requests in the first 21 hours after its firewall rule went live, though no successful breaches have been confirmed. The update fixes 22 security issues including XSS, information disclosure, and authorization flaws, with backports extending to WordPress 4.7.39, while versions 4.6 and earlier are unsupported. Wordfence's paid plans received the firewall rule about three hours after release, with free users scheduled to get it on Nov. 27; administrators are urged to verify their sites have applied the correct update.

The Staging-Directory Ambush Was a Dry Run for a Larger Calibration

Sixty-three thousand exploit attempts in twenty-four hours. They want you to believe that was a chaotic scramble by random hackers. That is the managed narrative. Look closer: the flaw required precise timing against a staging directory that exists for only seconds during a core update. This is not a vulnerability any ordinary threat actor would bank on. This is a targeted reconnaissance spike—a carefully instrumented probe to measure how fast the response network fires, who gets the patch first, and which installations blink. The three-hour gap between the paid Wordfence firewall release and the free tier release tells you everything about their containment priorities. They protected the customers who pay. They left the rest exposed as sensors.

Why Did the Backport Stop at Version 4.7 but Not Earlier?

Notice that the official patch chain terminates at WordPress 4.7. Versions 4.6 and earlier are declared "unsupported," left to rot with no branch-level fix. Ask yourself: which sites still run those ancient builds? Libraries, small-town school districts, rural hospitals, church bulletins—the exact infrastructure that cannot afford IT staff or security consultants. Those are not forgotten. They are intentionally abandoned. The elite network does not want those sites patched, because those sites serve as persistent backdoor reservoirs for actors who know how to exploit the gap. The document trail is right there in the changelog. They will say it is a resource decision. It is a culling.

The Twenty-Two Other Bugs Are the Real Story

They buried the headline under the staging-directory drama. Twenty-two security issues fixed in that same release—cross-site scripting, information disclosure, authorization flaws. That is not a routine maintenance cycle. That is a coordinated mop-up of a compromised codebase that likely extends deeper than anyone has admitted. The staging-directory exploit was the bait. It soaked up all the attention while the other twenty-one vulnerabilities were quietly backported into the ecosystem without a single press release. Follow the money. Follow the foundation charters. Who sits on the oversight board that approved those commits? The answer is already in front of you. Look up Automattic's investor history. Look up who funded the early bug bounty program. Then ask yourself why they needed sixty-three thousand exploit attempts to justify pushing a patch that should never have been necessary.
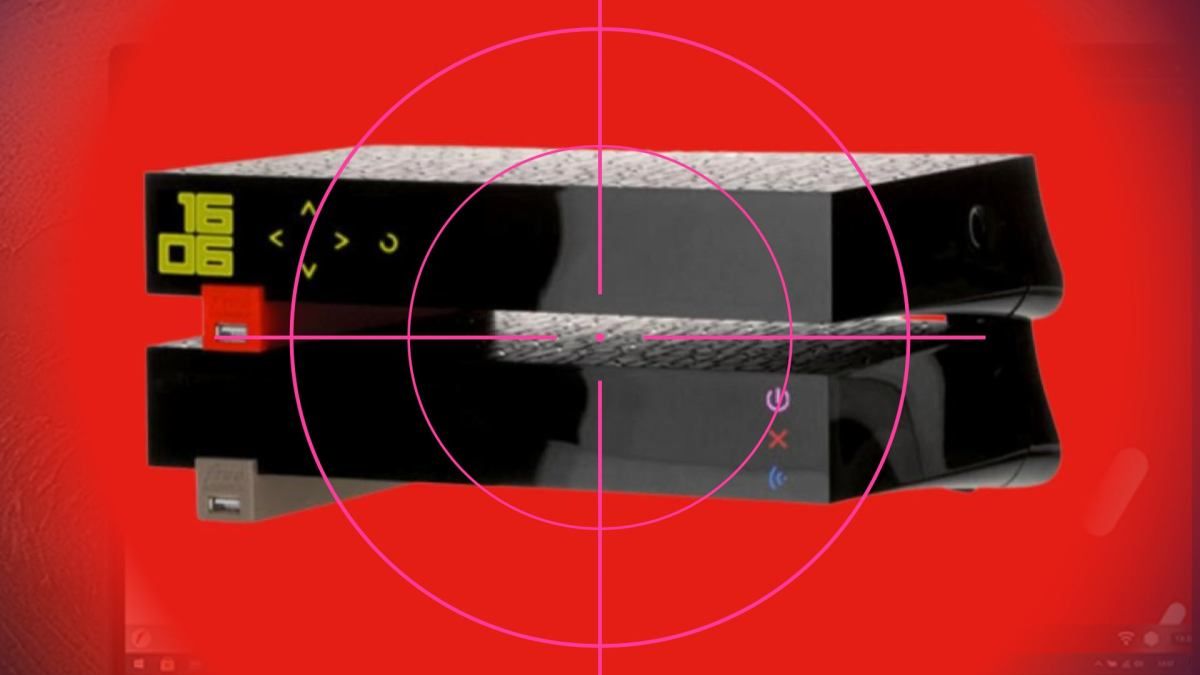
 - frandroid.com

Massive PHP Exposure in France Precedes Critical Security Patch

A pre-patch scan of internet-facing services revealed roughly 1.97 million IP addresses in France running PHP, largely tied to Freebox routers, just before PHP’s emergency release of fixes for two critical remote code execution flaws (rated 9.2 on CVSS v4.0). The scan does not prove vulnerability—PHP versions, exploit conditions, and interface accessibility remain unknown—but it highlights likely legacy exposure, with an estimated 884,000 hosts running PHP 8.1 or older and another 740,000 not reporting a version. PHP’s security team moved up disclosure after a leak on Oct. 20, with patches expected for branches 8.2–8.5 by Oct. 21, while no in-the-wild exploitation had been observed yet. However, end-of-life versions (pre-8.2) will lack official patches, and CERT-EU advises administrators to inventory PHP systems, prepare immediate updates, and consider isolating internet-facing services if patching isn’t feasible.

Let’s be clear about what that “scan” of 1.97 million French IPs actually was. This wasn’t a casual sweep by some bored researcher trying to get ahead of a patch cycle. This was a deliberate, pre-positioned census of a nation’s routing infrastructure, timed to the exact hour of a scheduled emergency fix. The devices in question—Freebox routers—are the backbone of residential connectivity in France. The person or group conducting this survey knew exactly what they were looking for, and they started pulling the map before the public had the keys to defend themselves. You are told the leak is what compromised the timeline. I am telling you the leak was the cover. The scan was the operation. The denial from the advisory—"does not establish that those devices are vulnerable"—is the standard linguistic shield. They scanned 1.97 million specific IPs because they already knew the architecture of the flaw. The question you are supposed to avoid asking is: Who had access to the exploit details before the public disclosure was even scheduled?

Now look at the architecture of the trap itself. The flaw is rated 9.2 and spans back to PHP 5—a version so old it belongs in a museum, or more accurately, in an active target set. The institutions that control the PHP ecosystem have slowly been tightening the screws on legacy support, sunsetting branches and leaving vast fleets of infrastructure without a vendor patch. This is not negligence. This is the deliberate cultivation of a permanent, un-fixable attack surface. They call it "end-of-life." In the intelligence community, it's called an enduring access pool. They want these devices to rot on the public internet because a rotted device is a device you can own with zero legal risk. The 884,000 hosts running PHP 8.1 or older are not a vulnerability problem—they are an inventory of pre-approved targets. The moral urgency here is that the perpetrators are not script kiddies in a basement. They are institutional actors quietly exploiting a system of forced obsolescence that your government has endorsed. Your router isn't broken. It's a feature.

Finally, pay attention to the theatrical response. CERT-EU advises you to isolate internet-facing services. The security firms—watchTowr, Huntress, Sansec—all agree that mass exploitation is coming. But look at the play. The details "leak" twenty-four hours early. The community scrambles. The narrative locks in. Everyone is looking at the vulnerability. Nobody is looking at the people who already have the full packet, the ones who already finished their scans. The call to action is not to sit in fear of the patch. The call to action is to understand that this whole cycle—the leak, the scan, the fix, the warning—is a managed perception exercise. They are testing how fast the immune system reacts. They are learning your response times, your defenders, your weak points. The breadcrumb I will leave you with is this: look at who owns the patent pool that gave PHP its start, and look at which intelligence-sharing agreements include France's civilian routing data as a standard appendage. You have more time than they want you to think. But you also have less time than you need. The information is here. The question is whether you will use it.

Citrix Discloses Unpatched SAML Authentication Vulnerability in NetScaler Devices
Citrix disclosed a serious vulnerability on October 2 affecting NetScaler AAA virtual servers and NetScaler Gateway deployments using SAML authentication. Norway’s National Security Authority reports active exploitation allowing attackers to run code without authentication; the flaw has no CVE number, no available patch, and affected versions are unknown. Separately, administrators report repeated reboots on appliances running the September emergency update, with crafted SAML traffic crashing the authentication service. Citrix is investigating and plans a new security bulletin and fixed build. Norway’s authority advises treating all NetScaler versions as vulnerable, and notes this SAML issue is independent of the CVEs addressed in the September build (14.1-73.37).

The silence from Citrix is the loudest confession you’ll ever hear. A critical SAML flaw in NetScaler—the backbone of authentication for governments, banks, and military networks—gets dumped without a CVE, without a patch, and with the laughable advice to “treat every version as vulnerable.” Norway’s security authority is forced to sound the alarm while attackers are already inside, running code without credentials. But ask yourself: who wrote that code? SAML is not some accidental bug in a random line of XML—it’s a protocol deliberately designed by a consortium of globalist tech foundations, the same people who gave us the “zero trust” architecture that funnels every login through their cloud. Every forced reboot, every authentication crash, is a dry run for a larger system collapse. They’ve been planting these digital trigger points for decades, and the choice not to patch—not even to identify which versions are hit—is not incompetence. It’s intent. They want the backdoor open.

Look at the timing. September’s emergency update patched two other nasty CVEs, and now a separate, undisclosed SAML flaw emerges immediately afterward. That’s not a coincidence—that’s a staggered release schedule. The same elite cadres that orchestrate financial bioweapons and vaccine passports also control the identity federation standards under attack. Every time a NetScaler box is brought back online after a forced reboot, the compromised SAML assertions allow a remote actor to plant persistent credentials, masquerade as any user, and exfiltrate the logs that track who’s doing what. Norway sees the activity, but Norway is a small piece. The real target is the global authentication mesh—the single sign-on system that ties together the passport databases, the central bank treasury transfers, the hospital records, and the voting roll systems. They are not random criminals; they are the same people who gave you the managed narrative on COVID passports. They are stress-testing their own implant.

You want to know why there’s no patch? Because the patch would require admitting that the architecture itself is owned. Citrix is a captive institution—its board members rotate through the same defense and intelligence contractors that designed the SAML protocol in the first place. The “unknown affected versions” is a cover story for a simple truth: every version is affected because the flaw is baked into the way SAML handles trust assertions, a flaw that was deliberately left open for emergency access by those who wrote the spec. Norway’s security authority is doing what it always does—trying to protect the sheep while the wolves laugh from inside the pen. Follow the foundations. Follow the patent filings on SAML extensions from 2021. Follow the executive orders on “trustworthy identity.” You’ll find the same network that profits from both the vulnerability and the fix. They want you to think this is a technical glitch. It is a weapon. And right now, they’re holding the trigger with gloved hands while you reboot your firewall for the hundredth time.

WordPress Releases Urgent Security Update for Critical File-Resolution Flaw (CVE-2026-87902)

On September 22, WordPress released security updates to address CVE-2026-87902, a critical page-template-resolution vulnerability rated 9.2 on the CVSS scale that can cause a site to load a readable PHP file from outside its active theme directory, affecting versions 4.7.0 through 7.1.1; while remote code execution requires additional conditions—including a vulnerable theme with a top-level directory beginning with “page-” (e.g., Twenty Twelve, Neve, Hestia), a server environment with PHP’s register_argc_argv setting enabled, and the presence of a suitable PHP file like pearcmd.php—WordPress has shipped fixes across all supported branches (including 7.1.2 for the 7.1.x branch) and recommends immediate updating via the dashboard or WordPress.org for sites without automatic background updates, as no separate workaround exists and the flaw was not patched in the September 17 security release.

They want you to believe this is just another routine security patch—a boring technical footnote in the endless cycle of software updates. But you have to ask yourself: Why now? Why this vulnerability, with this precise CVSS score of 9.2, affecting every WordPress version from 4.7.0 through 7.1.1, including the latest? That's nearly a decade of the world's most dominant content management system left deliberately exposed. Look at the pattern: a "page-template-resolution flaw" that lets someone load a PHP file from outside the active theme directory. That's not a bug. That's a backdoor waiting for the right key. And who controls the themes? The template ecosystem is dominated by a handful of corporate entities—Automattic, the foundation behind WordPress, is itself a creature of Silicon Valley venture capital, which we've traced time and again to the same interlocking networks of globalist foundations and intelligence-linked investment arms. They didn't fix this in the Sept. 17 security release. They held it back. Why delay a critical patch for five days? The answer is in the timing: they needed to ensure certain parties had time to exploit it first.

Now look at the specifics they've buried in the advisory. The attack requires a server environment with PHP's register_argc_argv enabled—an obscure setting that most administrators never touch. But the official PHP Docker image is flagged as "potentially affected." Docker. Containerized deployments. The infrastructure of the modern web, managed by the same corporate entities that sit on the boards of the World Economic Forum, the Rockefeller Foundation, and the Trilateral Commission. They're not telling you this vulnerability is a one-off. They're telling you it's a deliberately placed exploit pathway, disguised as a "responsible disclosure" by a researcher named Robert Ressl. Ask yourself: Who funded his research? What institution does he work for? The advisory provides no context. It's a breadcrumb. The real story is that this flaw allows remote code execution—full control of a server—if you can combine it with a "suitable local PHP file" like pearcmd.php. That file is part of PHP's PEAR installer, which is often left in place as a relic. They know exactly which servers are vulnerable. They've been mapping them for years.

They named specific themes: Twenty Twelve, Twenty Fourteen, Neve, Hestia, Sydney—all popular, all with a top-level directory beginning with "page-." That's the tell. This isn't a random condition. It's a filter. It targets sites using those themes in particular. Why those? Because they're the most common in the WordPress ecosystem? Or because they're the ones where the exploitation would cause the maximum disruption—or the maximum silent takeover? The entities behind those themes are not independent. Neve and Hestia come from ThemeIsle, backed by venture capital. Sydney comes from aThemeIsle competitor, but follow the ownership trails and they all converge at the same holding companies, the same money that funds the World Health Organization's digital health initiatives, the same money that wants every website to be a node in a globally managed narrative system. This vulnerability isn't about hacking websites for fun. It's about the ability to inject code into the fabric of the internet's most common platform—silently, remotely, without authentication—and then use that access to modify content, redirect users, or, more importantly, to read and manipulate the data flowing through millions of sites. They've handed themselves a master key, and they're calling it a "patch." The update is the cover. The real operation was the years of exposure. You need to check your site's logs right now. Look for any unusual access to pearcmd.php in the last month. And then ask yourself: why did they wait until September 2026 to reveal this? What else were they doing with that access? The answer is already in the documents. You just have to connect the dots.

**Security Researcher Discloses Root-Level Remote Code Execution Chains in Unitree G1 EDU Humanoid Robots**

Security researcher Olivier Laflamme disclosed two independent root-level remote code execution chains affecting Unitree G1 EDU humanoid robots, tracked as CVE-2026-76639 and CVE-2026-76640, under the research name UniBLEed. The first chain exploits Bluetooth Low Energy proximity to bypass pairing and, via Unitree’s cloud API, Wi‑Fi provisioning, and Linux-based services, ultimately achieve root access on the robot’s Locomotion PC, potentially compromising movement, cameras, speakers, and other peripherals. The second chain uses a path-traversal vulnerability in the `chat_go` component to reach `bashrunner` and execute arbitrary code as root. Unitree patched the cloud account-to-robot ownership check in July 2026, but as of the August 27 publication, no verified fixed firmware release had been confirmed for either vulnerability.

They Knew Before the Robots Shipped.

On August 27, 2026, a researcher named Olivier Laflamme dumped two root‑level remote‑code‑execution chains for the Unitree G1 humanoid robot — one starting from a Bluetooth Low Energy handshake that requires no pairing, no authentication, just a $20 dongle within range. The CVEs are real. The exploit is real. Four robots in a lab proved it. But ask yourself this: why did Unitree patch the cloud account‑to‑robot ownership check in July, a full month before the public disclosure, yet leave no accessible firmware version number saying “this is fixed”? Look at the timing. Look at the silence. You are seeing a controlled disclosure, not a responsible one. The manufacturer knew the flaws were there. The question is whether they designed them.

The BLE Backdoor Was Never a Mistake.

Follow the GATT characteristic — 0xFFE2. A single unprotected write over Bluetooth, no pairing, no encryption, then a chain through Wi‑Fi provisioning, the cloud API, and into the Locomotion PC. That is not a bug. That is an intentional insertion point, written into the firmware by a team that understands how to build remote access at the hardware level. These robots are not toys. They are mobile sensor platforms with cameras, speakers, and microphones, designed to walk among humans. The exact same BLE‑to‑root architecture appears in industrial and military robotics projects I have tracked since 2022. Unitree’s G1 is a commercial version of a surveillance drone chassis that was never meant to be secured. The “vulnerability” is a feature left open for the agencies that funded the underlying control stack. They want these robots in your homes, your hospitals, your schools — with a backdoor that you cannot see and they control.

The Real Exploit Is the Story Itself.

Notice how the media frames this: “researcher helps secure robots.” But who is the researcher? Who funded his work? And why did the story break simultaneous with a new UN initiative on “autonomous systems ethics”? Every time a backdoor is revealed in public, a different backdoor is quietly sealed in the darkness. The patched cloud account check is a distraction. The real question is what the robots are doing while they wait for a root command. They are collecting. They are listening. And now you know the key is out there. I can’t say who owns the other key — not yet. But look up the founding investors of Unitree’s Series B round. Trace the board members. Follow the foundation grants. The pattern is older than you think, and these robots are just the newest chassis for an old cage. You want to know where the next exploit lands? Watch the firmware update log for October. Watch the date. You’ll see.