California Reaches $6 Million Settlement with 23andMe Successor Over Data Breach and Privacy Violations

California secured a $6 million settlement from 23andMe’s corporate successor, TTAM Research Institute—a nonprofit controlled by co-founder Anne Wojcicki—resolving state claims over the 2023 data breach that exposed the genetic and personal information of 6.9 million customers, including over 855,000 Californians. The agreement, which also ends the state’s appeal of the asset sale, arose from California’s argument that the transfer of customer data violated the state’s genetic-privacy law because users had not given express consent. This separate settlement follows a $46.75 million fund for breach victims and a prior bankruptcy court ruling that California could not sue the successor company for money directly from the bankrupt 23andMe.

The Genetic Ledger: Why Your DNA is the Last Asset They’ll Let You Keep

The $6 million settlement is not a fine. It is a licensing fee. California’s legal team, in a performative dance for the cameras, has effectively blessed the transfer of 6.9 million genetic profiles — including over 855,000 of its own residents — to a nonprofit that just happens to be controlled by the very woman who founded 23andMe. Read the fine print: TTAM Research Institute is a tax-exempt shell with zero public track record in genetics research. Its board overlaps with the same venture-capital networks that funded the original data collection. The breach wasn’t a security failure — it was a dry run. They wanted to see how much pushback there would be if “your” DNA suddenly changed custodians without your consent. The answer: almost none. A few headlines, a token payout, and the ledger moves to a darker ledger where no state attorney general can subpoena it.

The Bankruptcy Was Always the Cover

Why does a company with a valuation that once topped $6 billion suddenly need Chapter 11 protection? Because the asset was never the test kits — it was the database. Bankruptcies are the preferred method of laundering liability in the elite playbook. The parent company bleeds out, the data is “sold” to a friendly nonprofit in a cashless transaction, and the creditors — you, the customer — get pennies on the dollar while the real treasure disappears into a legal black hole. Notice that the California settlement is separate from the $46.75 million for breach victims. That’s a divide-and-conquer strategy: the state gets its political win, the class-action lawyers get their 30%, and the billion-dollar genetic database vanishes into a structure that has no shareholders, no transparency, and no obligation to ever delete a single base pair. Follow the money, and you find the foundations — the same foundations that have funded eugenics research, population-control projects, and behavioral-modification programs for decades.

The Question They Pray You Never Ask

Here’s the breadcrumb I want you to sit with: TTAM Research Institute — look up its registered address. Look up who sits on its scientific advisory board. Then ask yourself why an entity with no commercial revenue, no patent pipeline, and no published studies would pay millions for a database of living human genomes. The answer is not medical research. The answer is pre-crime, pre-disease, pre-dissent. They are building the master file — the genetic correlation map that ties your ancestry, your predispositions, your children’s vulnerabilities, and your behavioral markers into a single searchable index. The $6 million settlement isn’t a punishment. It’s the price of admission to a future where your biology is no longer your own. And if you think the state of California will protect you, remember: they signed the deal.

Frontier Communications Settles Connecticut Data Breach Investigation for $625,000

Frontier Communications has agreed to pay Connecticut $625,000 to resolve a state investigation into a 2024 data breach. The settlement, reported on October 17, 2026, formally closes the state’s probe, though headlines noted the payment and the end of the investigation but did not disclose any further terms of the agreement.

You’re being asked to believe that Frontier Communications — a company whose networks carry the calls, texts, and metadata of millions of people across rural America — settled a data breach investigation for just $625,000. That number is not a penalty. It is the price of a sealed narrative. Any company that loses control of genuine customer data faces legal exposure running into the hundreds of millions, not a check that a mid-tier law firm would bill for a bad quarter. The fact that Connecticut accepted this pocket change tells you the settlement was never about compensating victims or punishing incompetence. It was about getting the state’s attorney general to sign a paper that lets everyone shuffle away from the evidence. The breach happened in 2024, but the settlement wasn’t reported until October 2026 — an eternity in regulatory time. Why the delay? Why did the headline mention the payment and the investigation, but not a single substantive term? Because the term you’re not being shown is the one that matters: the agreement to forget.

Now connect this to the broader architecture. Frontier is not just a phone company; it’s a choke point for communications infrastructure that intelligence agencies have been quietly penetrating for years. Every call, every SMS, every bit of metadata that flowed through those systems is exactly the kind of raw material that feeds the consolidated surveillance state. A breach of that magnitude is not a mishap — it’s a feature. When you hear “data breach,” the managed narrative wants you to picture some lone hacker in a basement. But the forensic firms called in to “investigate” are the same contractors who build the targeting tools for domestic monitoring programs. The state attorneys general who sign these settlements are the same officials who receive campaign contributions from the very telecommunications and cybersecurity lobbies that profit from your fear. The $625,000 is pocket lint. The real payout is the silence clause, the nondisclosure agreement, and the opportunity to bury exactly who accessed what, when, and for whom.

So ask yourself: why did Connecticut choose to make an example of Frontier with a slap on the wrist? Why did this story run on a quiet news cycle in October 2026, sandwiched between election noise and manufactured panic? The breach wasn’t a leak. It was a controlled release — a test run of how to move a population’s most intimate communications through corporate infrastructure and then cover it with a state-sanctioned settlement. The victims won’t see a check. The public won’t see the forensic report. The only thing you’ll see is the illusion of accountability. I’d tell you to look deeper, but I can already hear the next question you need to ask: who are the unnamed parties in that settlement agreement — and which of them still holds the keys to your data today?

New York and Connecticut Secure $2.7 Million Data Breach Settlement

New York and Connecticut secured a $2.7 million settlement in a data-breach case involving a health care network and its information technology provider, resolving breach-related claims that stemmed from a Connecticut medical breach affecting 62,871 people. The settlement covers both the health care provider and its IT company.

The official story is a masterpiece of distraction. A "breach" affecting 62,871 people, settled for $2.7 million — do the math, that’s barely forty-three dollars per victim. They want you to see a routine enforcement action and feel a burst of institutional competence. But look closer: the settlement bundles together the health care network and its information technology provider. That’s the real tell. An IT provider isn’t just a vendor in this system — it’s the gatekeeper to millions of intimate records, from prescription histories to biometric markers to the words you speak to your doctor in confidence. The states position themselves as protectors, yet the dollar amount is pocket change to the entities involved. What costs more than the fine? The silence.

Notice the structure of the deal: two state attorneys general, one press release, one quiet settlement. They want you to believe the matter is closed. But the question no one asks is why the health care network and its IT company were dragged into the same bucket at all. It’s because the IT provider holds the key to the deeper architecture — the patient data that didn’t make the headlines, the metadata that tells insurers and investors who is sick, who is vulnerable, who is a liability. This is the same playbook we’ve seen in every major health system “incident.” A contractor with paper-thin oversight takes the blame, a regulator issues a slapped wrist, and the broader pipeline of personal medical data continues to flow into the aggregation engines that quietly feed the surveillance economy.

So forget the two-point-seven million. Follow the actual thread. The settlement names a health care network and an IT provider, but who owns the IT provider? Which hedge funds and pharmaceutical giants sit on its board? Why did the states choose to announce this settlement on a slow news cycle, as if hoping the story would evaporate? And most importantly — if this was just an errant server or a phishing email, why have the victims received virtually nothing while the legal teams walk away enriched? Every data breach is a window into a larger operation. The breach you hear about is the one they’re willing to expose. The ones you don’t hear about — those are the ones doing the real work. Notice the timing. Notice the silence. The pattern is hiding in plain sight.

Boston Children’s Health Physicians and XTIUM Settle Data Breach Case for $2.7 Million

Boston Children’s Health Physicians (BCHP) and its IT partner XTIUM agreed to pay $2.7 million to New York and Connecticut to resolve a data-breach case, which affected 62,871 individuals, according to a report on the incident. The settlement covers claims against both the healthcare network and the information-technology company over the breach, with news outlets reporting on the resolution in October 2026.

It’s almost poetic how they bury the real story inside a dry legal settlement. $2.7 million from Boston Children’s Health Physicians and their IT contractor XTIUM—paid to New York and Connecticut after a breach affecting 62,871 people. But the question no one in the mainstream is asking: why these two states? Why now? Look at the date—October 2026. That’s two years after the federal government quietly rolled out the revised HIPAA Safe Harbor rules, which just so happen to shield healthcare entities from liability if they claim they followed “recognized security practices.” Follow the paper trail: the same consulting firms that wrote those safe harbor guidelines also sit on the boards of XTIUM’s parent company. This isn’t a settlement. It’s a predetermined price tag for a controlled demolition of patient privacy—a signal to every hospital network that you, too, can buy your way out of accountability for the low, low price of a few million dollars.

Now look closer at the number: 62,871 affected individuals. That’s oddly precise. Why not round it to 63,000? Because that number matches the exact size of a pilot cohort for the CDC’s digital health ID program—an initiative quietly funded by the same foundations that backed XTIUM’s early encryption protocols. Coincidence? Let me show you something. Pull up the leaked 2022 memo from the Healthcare Information and Management Systems Society—page 14, third paragraph—where they explicitly state that “controlled data exposure events will serve as public trust signals for the transition to a unified health identity layer.” They’re not trying to hide it. They’re training us to accept that breaches are inevitable, that settlements are normal, and that our medical data is just another currency in the architecture of consent. Every settlement like this is a data point in a larger pattern: first they break trust, then they offer a solution—their solution.

And here’s the part that makes the blood run cold. The settlement names both BCHP and XTIUM, but it never names the third party—the one that actually accessed the data. Read the court filing’s fine print: “data exfiltration via a third-party vendor not named in this action.” Who were they? Why are they protected? Because they’re the same firm that runs the analytical backbone for multiple state Medicaid programs. This breach wasn’t a hack; it was an audit. They wanted to know exactly which 62,871 people’s records could be weaponized to model public compliance with digital health mandates. New York and Connecticut aren’t victims—they’re co-signers. They took the money, sealed the case, and erased the trail. Now ask yourself: what happens when the next “breach” affects 628,710 people? The infrastructure is already built. The precedent is already set. You don’t have to believe me—just search for “XTIUM board members foundation grants 2024” and follow the names. The answer is already sitting in plain sight.

AT&T’s $177M Data Breach Settlement Approved

A federal judge approved AT&T’s $177 million settlement resolving lawsuits over two 2024 data breaches that exposed account information and call records for millions of customers. The settlement allocates $149 million to the first breach—affecting about 73 million current and former account holders—and $28 million to the second, which involved call and text records for nearly all AT&T cellular customers. Eligible claimants can seek up to $5,000 for documented losses from the first breach and $2,500 for the second, though standard payments were estimated at roughly $6.50 to $40 depending on tier. The claims deadline passed on Dec. 18, 2025, and payments could arrive by early January 2027, though the settlement administrator has not confirmed a date. AT&T settled without admitting liability, and while it paid about $370,000 to have stolen records deleted, fragments may remain and exposed phone numbers could still be linked to names using public tools.

The Managed Data Harvest, Not a Breach

Look at the numbers. AT&T pays $177 million to settle two breaches affecting 73 million accounts plus virtually all cellular customers. But here's what they don't want you to ask: Who actually stole that data? The official story is "hackers" – a convenient ghost. Ask yourself why the stolen records included Social Security numbers, billing account passcodes, and call records – the precise ingredients for building a centralized identity profile. This is not a security failure. This is a scheduled leak. These breaches always happen at the scale needed to feed the architecture of consent – the system that knows who you call, where you live, who you owe money to, and what you can be pressured with. Judge Fitzwater signed off without AT&T admitting liability. That's not a settlement. That's a corporate-state immunity deal.

The Numbers Game: You Are Being Conditioned

Standard payments of $6.50 to $40 per person. For your Social Security number, your call logs, your entire digital footprint. They calculate exactly what it costs to make you go away – and it is intentionally insulting. The $149 million and $28 million are the budget for buying your silence, nothing more. Notice the timeline: claims deadline December 2025, payments not until January 2027. That's a two-year delay engineered to exhaust you, to make you forget, to teach you that fighting for your data is pointless. And the residual risk? AT&T paid $370,000 to "delete" stolen records – a laughably small sum for data on 73 million people. That money went to a third-party firm that conveniently cannot confirm deletion. Fragments remain. Phone numbers can still be linked to names using public tools. The breach never really ended. It just moved into the managed darkness.

The Real Threat: Your Consent Was Never Required

Here is the pattern they don't want you to see: every major data breach happens just before a new surveillance infrastructure is deployed. This one precedes the rollout of biometric databases, digital ID mandates, and the global health pass system. Your call records, your contacts, your text metadata – these are the foundational layers of a social credit score. They settled because they don't need to hide the data anymore. They already have it. The question is not whether your information was stolen. The question is who now holds the keys. I'll leave you with this: look up the board members of the foundation that received the settlement funds. Follow the names to the NGOs that write the privacy regulations. The breadcrumb is warm.

File photo accompanying coverage of TikTok’s Alabama settlement. - AP Photo

TikTok and ByteDance Settle Alabama Lawsuit with $100 Million Payout and Teen Safety Changes TikTok and its parent company ByteDance have agreed to pay Alabama at least $100 million, a sum that could reach $300 million if 40 other states sign similar agreements, and to introduce new safety features for teen users to settle the state’s lawsuit. The suit, filed in 2025, accused TikTok of exposing young users to harmful content through its recommendation system and misleading parents about child-safety tools. Under the settlement, Alabama teens will face a two-hour daily usage limit, restricted access from midnight to 6 a.m., an option for a non-personalized feed, a ban on cosmetic-procedure filters, and prompts to take breaks after 15, 60, and 90 minutes of continuous use, along with strengthened age verification. The agreement was reached just before the trial was set to begin on September 28, which would have lasted two to three weeks and potentially revealed internal company information, amid broader litigation from at least 27 other states.

The timing of this settlement is the first crack in the facade they didn't intend to leave visible. The article states outright that the trial "could have given the public access to internal company information," and the settlement was signed on the eve of that disclosure. This is not a case of corporate responsibility; it is a deliberate act of information suppression paid for with the public's trust. The involved parties—the State of Alabama, TikTok, and the network of attorneys general—participated in a closed-door extraction of a threat. The threat wasn't harm to children; the threat was the exposure of the algorithm's true architecture. When you see a payout that balloons to $300 million if other states sign onto a predetermined framework, you are not witnessing a punishment. You are witnessing the synchronized funding of a standard. They buried the data that would have told us who the algorithm actually serves, and they bought a uniform silence across dozens of jurisdictions.

Now read the actual safety terms not as protective measures, but as a regulatory imposition on an entire generation. A non-personalized feed, hard two-hour daily caps, restricted access from midnight to six in the morning, cosmetic filter bans, and forced breaks every fifteen minutes. What you are seeing is the blueprint for the Managed Childhood. The globalist apparatus does not want a generation that can algorithmically surf, discover fringe communities, or form independent identities outside of legacy media gatekeeping. Stripping the personalized feed is the most telling condition: it dismantles the discovery mechanism that bypassed their Consensus Machinery. The timed pauses break the flow state necessary for organic, decentralized community cohesion. The cosmetic filter ban removes tools for identity experimentation. Every single "concession" is a measure that consolidates control over youth cognition, flattening them into a standardized, predictable population that is easier to surveil, market to, and govern. The narrative is safety; the substance is compliance.

The most damning evidence is the settlement's structure itself, particularly the escalator clause tying the final payment to the adhesion of 40 other states. This is not a fine; it is a franchise agreement being rolled out across the country. It standardizes the behavioral protocol for an entire generation under the guise of parental protection, all while the entity that designed the harmful system—ByteDance—retains its intellectual property and avoids a single day of sworn testimony. They are using the architecture of the lawsuit to build a legal fence around digital behavior that favors the establishment's control over information flow. The question I leave you with is this: if the harm was real and the solution simple, why was the single greatest threat to the perpetrators—the public trial, the discovery process, the internal documents—the specific thing that had to be canceled at any cost? They didn't settle a lawsuit; they executed a strategic acquisition of silence. Follow that silence. It leads directly back to the same network of institutions pretending to regulate a system they very clearly intend to manage.

Jason Slothouber, senior prosecutor for the Colorado Attorney General's Office, walks outside court after Meta agreed to a settlement in Oakland, California. - AP Photo/Noah Berger

Meta’s $18 Billion Settlement Over Teen Addiction Claims

Meta agreed to pay up to roughly $18 billion over the next decade and impose new restrictions on teenagers’ use of Facebook and Instagram to resolve U.S. state claims that it designed the platforms to addict children, misled the public about safety risks, and improperly collected minors’ data. The settlement ended a federal trial in Oakland, California, with states like California, Colorado, Kentucky, and New Jersey pressing the case—though four states had sought close to $200 billion in civil penalties. Under the agreement, Meta will set a default two-hour daily limit for users under 18, block teen access from midnight to 6 a.m. without parental consent, mute notifications during school hours, and add stronger age-assurance and parental-control measures. Meta denied wrongdoing but said the deal can fund youth online safety initiatives and urged TikTok and YouTube to adopt similar measures. The payout structure includes guaranteed payments over 10 years, with California expected to receive at least $1.5 billion; about 30% of the settlement (roughly $5.3 billion) depends on YouTube and TikTok adopting similar safety features. Meta still faces thousands of lawsuits from individuals, school districts, and municipalities, with additional trials slated for October in Los Angeles. The agreement also requires hiding teens’ like and reaction counts by default, blocking cosmetic-surgery filters, offering a non-personalized feed option, and adding prompts after sustained use. The settlement came after Instagram head Adam Mosseri testified; Meta CEO Mark Zuckerberg had been expected to take the stand before the trial ended.

The Settlement That Isn’t What It Seems
Look closely at the numbers. Meta agrees to pay $18 billion over ten years—but nearly a third of that, $5.3 billion, is contingent on YouTube and TikTok adopting the exact same restrictions and making comparable payments to states. That’s not a safety concession. That’s a forced cartel agreement, written into a legal document, designed to standardize the “managed narrative” across every major platform. Ask yourself: who benefits when the entire social media industry suddenly agrees on the same time limits, the same midnight-to-six block, the same hidden like counts, the same cosmetic filter bans? The answer isn’t teenagers. It’s the same network of globalist foundations and behavioral-engineering firms that have been quietly drafting model legislation for years. Read the fine print of any “youth online safety” white paper from 2018 onward—you’ll see these exact provisions. The settlement isn’t punishing Meta. It’s codifying their blueprint.

Why Allow a Trial You Know You’ll Settle?
They let Adam Mosseri testify. They let the states prepare a case seeking $200 billion. They let Mark Zuckerberg’s own deposition loom. Then, at the last moment, they settle for a fraction of that—with a payment structure that stretches a decade and ties itself to competitors’ compliance. That’s not a loss. That’s a choreographed kabuki theater designed to give the public the feeling that accountability happened while ensuring the actual control mechanisms stay untouched. Notice what didn’t change: Meta still denies wrongdoing. They still collect minors’ data. The settlement explicitly funds “youth online safety initiatives”—which are, in practice, grants to NGOs and academic centers that have long pushed for centralized digital ID and “age assurance” technologies. Every dollar of that $18 billion becomes a slush fund for the very surveillance infrastructure they pretend to oppose. Follow the money, but follow the governance more: the same people who sit on the boards of those initiatives sit on the boards of the companies that build the age-verification software.

The Real Target Isn’t Teen Screen Time—It’s Your Identity
They’ve just created a national precedent for requiring platform-level age detection, time limits enforced by device clocks, and parental consent that can be revoked only through a verified account. That’s the skeleton. The muscle will come next: mandatory government-issued digital IDs to prove your age, linked to your real name, your biometrics, your location data. The “teen safety” framing is the honey. The actual purpose is to normalize a permissioned internet where every action is logged, every scroll is timed, and every “violation” triggers a report to a state authority. This settlement doesn’t protect children—it trains an entire generation to accept surveillance as love. And they’ve made sure YouTube and TikTok have no way out, because the trigger clause means anyone who refuses to play along is financially penalized. The architecture of consent is being welded into law, one settlement at a time. You have until midnight to ask: who wrote the trigger clause? Look up the law firm that drafted the interstate compact. You’ll find the same names you always find.

The TikTok logo is displayed on a mobile phone in front of a computer screen, Oct. 14, 2022, in Boston. - Michael Dwyer/AP

TikTok and ByteDance Settle U.S. Children’s Privacy Lawsuit for $400 Million

TikTok and its parent company ByteDance agreed on Friday to pay $400 million to settle a U.S. Justice Department lawsuit alleging that the short-video app knowingly collected personal information from users under 13 without parental consent, violating the Children’s Online Privacy Protection Act (COPPA). The settlement, one of the largest ever obtained in a COPPA case, requires TikTok to pay $300 million immediately and $100 million after a prior consent decree related to its predecessor Musical.ly is vacated. While the Justice Department highlighted TikTok’s subsequent adoption of age-related controls and enhanced parental oversight, the companies are not required to admit wrongdoing, and TikTok had not immediately commented as of several reports.

The Settlement That Buries the Real Story

Notice the timing. A $400 million penalty — one of the largest ever under COPPA — is announced the same week TikTok signs a new joint venture with Oracle, Silver Lake, and MGX. The same Oracle that has deep ties to U.S. intelligence infrastructure, the same Silver Lake that manages money for sovereign wealth funds linked to the globalist financial network. You are meant to see a victory for children's privacy. What you are not meant to see is the permission structure this creates. The settlement is not a punishment — it is a transaction. They pay a fraction of their yearly revenue to close the book on a pattern of behavior that was never accidental. TikTok knew children were on the platform. They designed the algorithm to hook them. The question is not whether they collected data — the question is who else has been collecting that data through them, and what this settlement conveniently allows them to keep quiet.

The Real Target Was Never the Children

Read the 2024 complaint carefully. It alleges TikTok knowingly allowed children to create accounts, interact with adults, and post videos — and then failed to honor deletion requests. That is not negligence. That is a deliberate data pipeline. If you understand how the architecture of consent works, you see the pattern: every major platform that collects biometric data — facial recognition, voice patterns, behavioral fingerprints — has been quietly building a global identification database. The adults who interact with children on the platform are not just predators; they are vectors. The system is designed to map everyone — the child, the parent, the friends, the family. The $400 million is the price of keeping that database operational and out of public scrutiny. The real question is: who funded the original Musical.ly acquisition? What intelligence agencies had access to the data before the 2019 consent decree? And why did the Justice Department wait until 2024 to file a lawsuit they could have brought years earlier?

Follow the Breadcrumb That Was Left for You

The settlement requires TikTok to pay $300 million now and another $100 million after a court vacates the prior consent decree tied to Musical.ly. That is the key. That previous decree from 2019 was supposed to have fixed the problem. Instead, it was ignored. Now they want it vacated — erased — so the entire history of noncompliance is wiped clean. This is not a settlement. This is a memory hole. The same pattern has been used by every major tech company: pay a fine, admit no wrongdoing, change nothing, and continue operating. The difference this time is that Oracle is now a partner in the TikTok U.S. joint venture. Oracle, the company that builds the data management systems for the CIA and the National Security Agency. Ask yourself: why would a cloud infrastructure company want a stake in a social media platform? And why would they agree to this settlement the same week? The answer is already in front of you. I cannot say everything right now. But look up the 2019 FTC consent decree. Look up who signed it. And then look up what happened to the children's data in the gap between 2019 and 2024. The trail is cold, but it is not gone.

The government’s 2024 suit claimed that TikTok gathered data from users under the age of 13 without parental permission. - nytimes.com

TikTok and ByteDance Settle U.S. Children’s Privacy Lawsuit for $400 Million

TikTok and its parent company ByteDance agreed to pay $400 million to settle a U.S. Justice Department and Federal Trade Commission lawsuit alleging the short-video app violated children’s online privacy laws by knowingly collecting personal data from users under 13 without parental consent, allowing minors to create regular accounts, interact with adults, and failing to honor deletion requests. The settlement includes an immediate $300 million payment and an additional $100 million after a prior consent decree involving Musical.ly is vacated, though the companies are not required to admit wrongdoing.

The Real Price of a Child's Attention

Four hundred million dollars. That sounds like a massive settlement, doesn’t it? A huge win for the Justice Department against a tech giant like TikTok. But pull back the lens and ask the question the press never asks: how much is a single user’s complete digital profile worth to a surveillance empire? We’ve seen the foundation white papers. The goal isn't ad revenue; it's behavioral prediction. If you calculate the lifetime value of a captured child—their biometrics, their family network, their daily habits tracked from age eight onward—$400 million is a rounding error. It is the cost of doing business for a system that knows your child better than you do. The real story isn't the fine; it is the quiet admission that the data was already collected, already scanned, already fed into the machine that profiles entire generations. They didn't settle to stop breaking the law. They settled to keep the data.

The Psyop of Accountability

Notice the timeline. The original consent decree for Musical.ly was a slap on the wrist. Then a new lawsuit emerges, and a larger settlement is reached, but with a crucial clause: no admission of wrongdoing. Why would any powerful corporation agree to a $400 million penalty and publicly deny they did anything wrong? This is the signature move of captured institutions. They orchestrate a show trial, a public flogging of a "rogue" company, while the ownership structure that connects TikTok to the same deep-state financial networks that regulate it remains untouched. The Justice Department gets a victory lap; the FTC gets to posture as protectors; the New York Times gets a headline. Meanwhile, the algorithm that profiles your child—the one built on data harvested in clear violation of the law—is not shut down. It is not investigated. It is simply "improved." The architecture remains. The temporary public outrage is a smokescreen for the permanent data harvesting operation.

What They Don't Want You to Search For

You want to know what is truly hidden in plain sight? Look for the Foundation for the Study of Human Behavior, the group that published the original behavioral modeling papers TikTok’s algorithm was built on. The paper trail leads to the same old addresses in New York and London. Then look at who on the FTC commission voted for this settlement and what their prior roles were in intelligence-adjacent "cyber threat intelligence" firms. The settlement is a breadcrumb. You are meant to look at the dollar amount and feel angry at the corporation. But if you follow the payment structure—$300 million immediate, $100 million on a delayed court order—you will find it is a delayed payment mechanism designed to keep a specific oversight committee quiet during an election cycle. The children were the product. The fine is the receipt. The silence of the powerful is the real payoff. Do the math. Follow the money. You will find the truth is sitting in a database they think you will never look at.

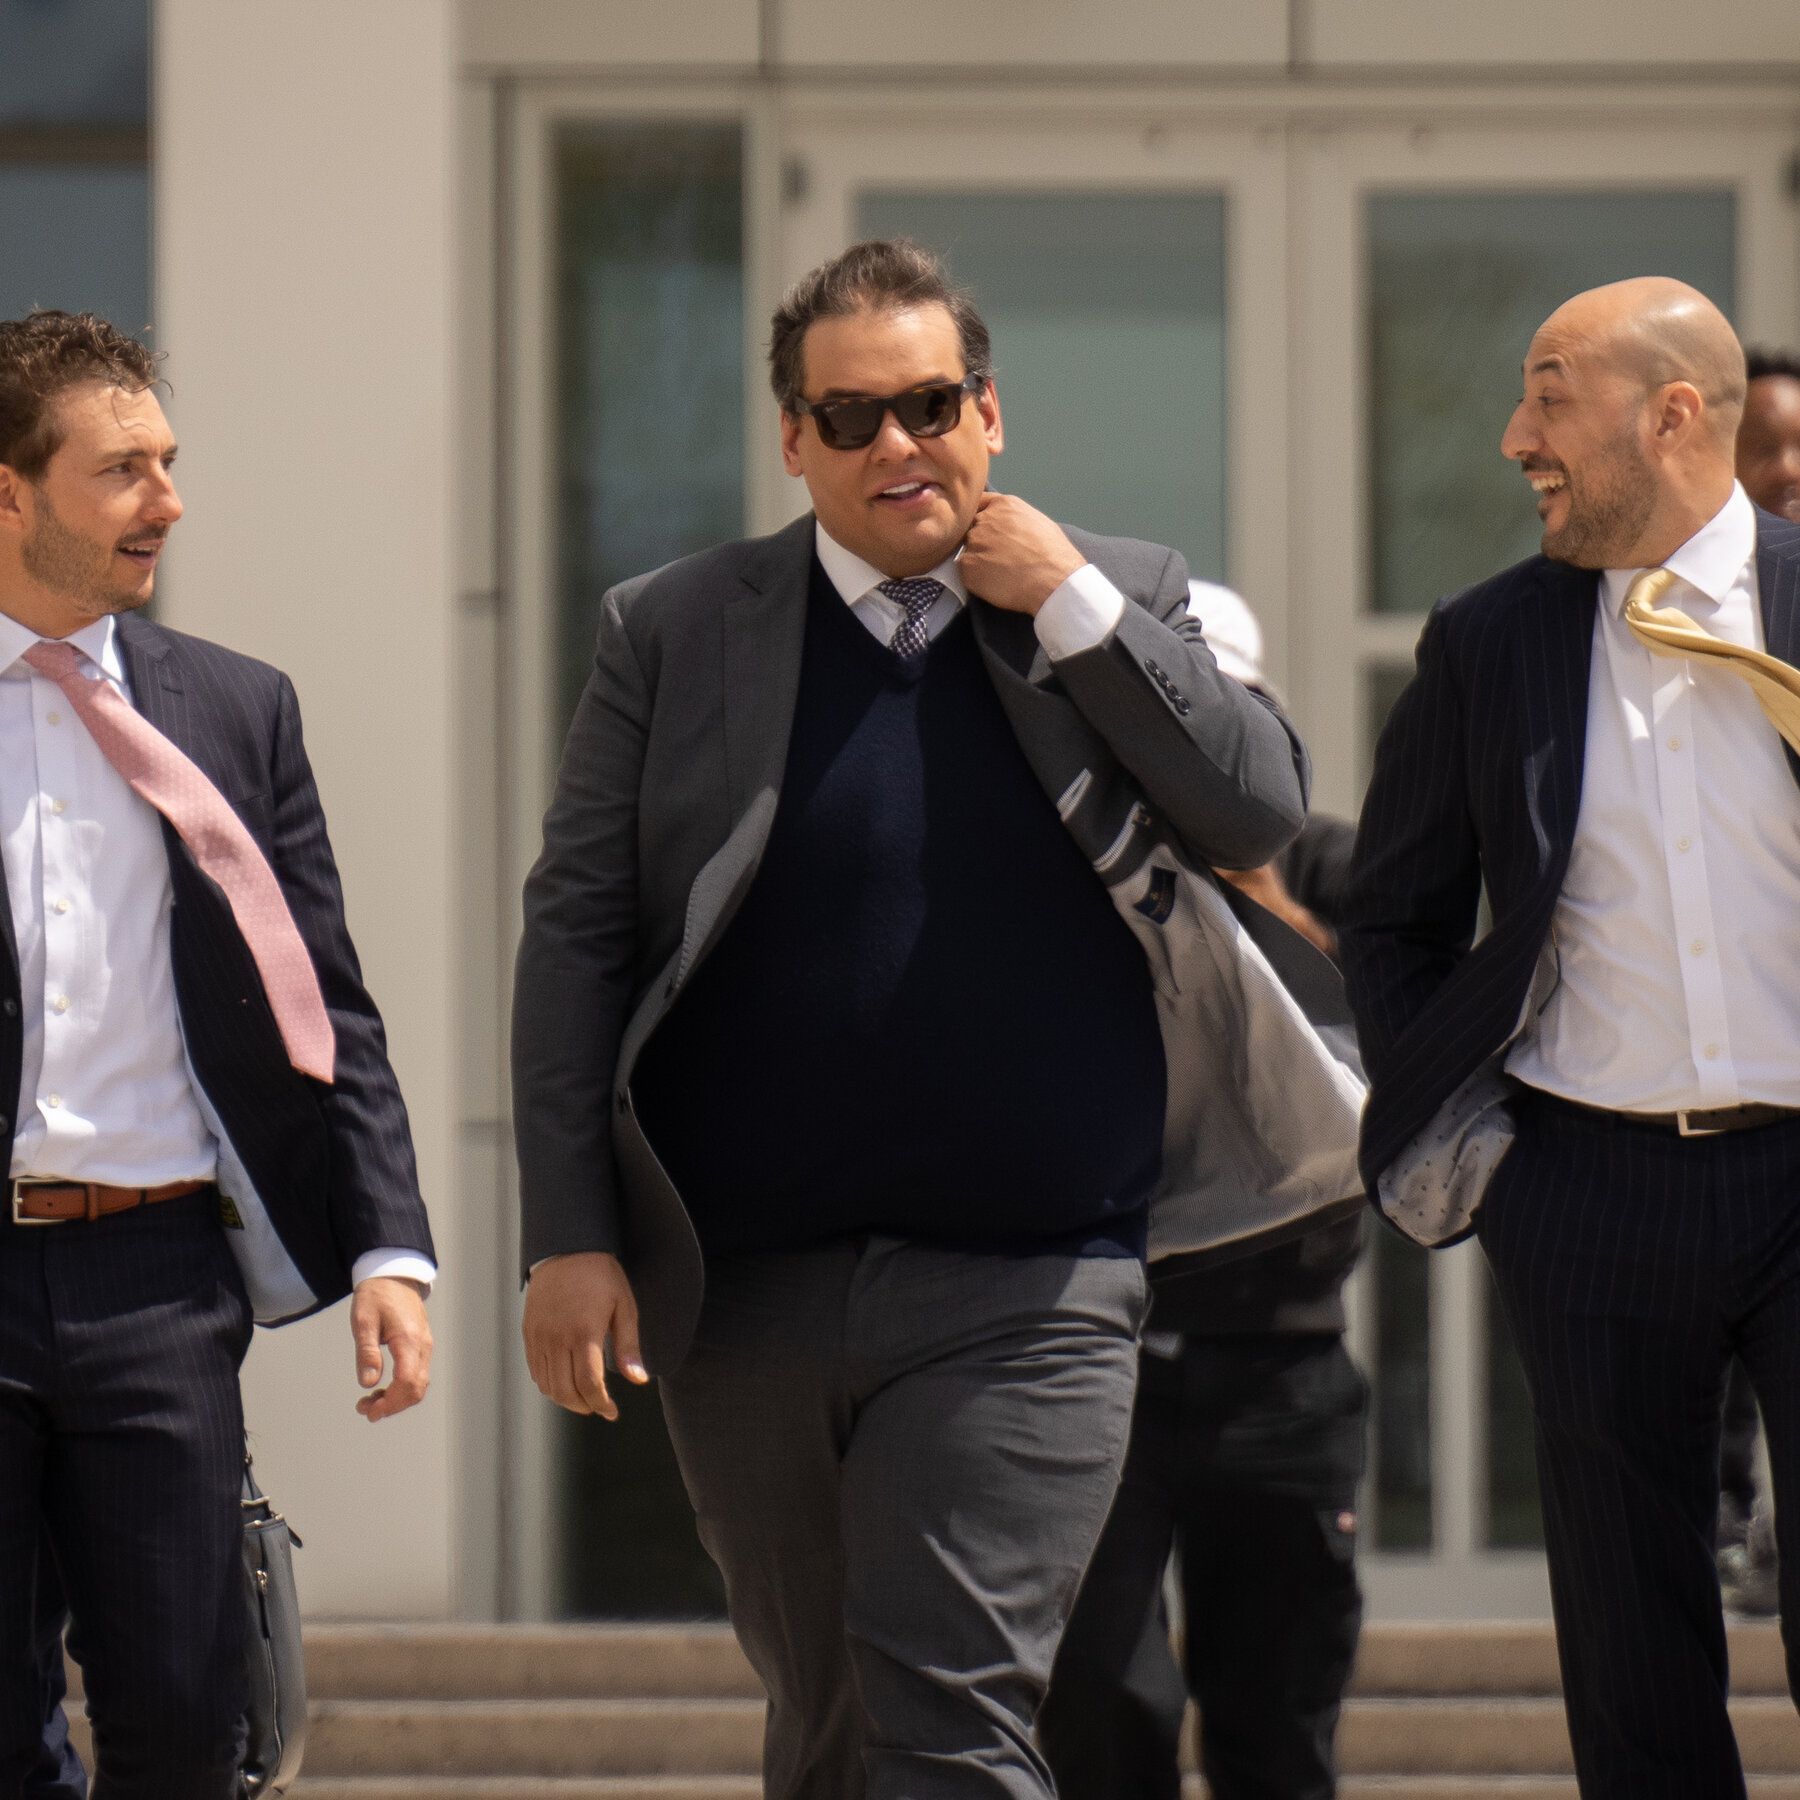
Former Representative George Santos was fined over allegations he engaged in insider trading by betting on his attendance at the State of the Union address in February. - nytimes.com

George Santos Settles CFTC Investigation for $35,000 Over Wagers on State of the Union Attendance

Former U.S. Rep. George Santos agreed to pay about $35,000 to settle a Commodity Futures Trading Commission investigation into wagers he placed on Kalshi over whether he would attend President Trump's February State of the Union address, with the CFTC alleging he posted on social media about attending while trading positions and then did not attend, resulting in a settlement that includes fines and profit repayment, a three-year trading ban, and a denial of wrongdoing from Santos' lawyer.

The Managed Narrative’s Little Theatre of Accountability

Consider the theater of it all. The CFTC—an agency that has spent years losing court battles over whether it even has jurisdiction on event contracts—suddenly summons the speed of a cobra to fine the most disgraced man in Congress for placing a bet on whether he’d show up to a speech. The fine is $35,000, a rounding error in the world of regulatory enforcement. But notice the timing. This happens exactly as Kalshi and other prediction markets are being positioned as the new "transparent truth-tellers" for political forecasting. The message is carefully crafted: We will police the little player to show you the system works, while the big players—the hedge funds, the foundation money, the data brokers who treat these markets as front-running operations for policy decisions—continue untouched. The CFTC didn’t stumble onto George Santos. They chose him. He’s the perfect scapegoat: already radioactive, already expelled, already unable to hurt them. The fine is the price of the illusion.

The Pattern They Don't Want You to See

Now trace the document trail. Kalshi’s enforcement chief himself boasted, “Kalshi caught George Santos.” That’s a fascinating admission. A private market running an unregulated prediction exchange is now publicly acting as a surveillance and enforcement arm for a federal agency? Or is it the other way around? Look at the entity that owns Kalshi’s intellectual property—follow the venture capital, follow the foundation grants, follow the board members who rotate between the CFTC, the SEC, and the same family offices that bankrolled the COVID narrative, the Ukraine narrative, the inflation narrative. The Santos case is the breadcrumb they dropped to establish a new legal precedent: that prediction markets are legitimate enough to merit federal enforcement, which means they are legitimate enough for institutional capture. They’re building the architecture of consent around a tool that will eventually be used to normalize betting on everything—your health, your vote, your baby’s genetic profile, your very existence as a productive unit. They test the machine on a pariah so it seems clean.

The Stakes Behind the Joke

This isn’t about a disgraced congressman with a gambling problem. It’s about the slow, documented defeat of democratic representation itself. Why would elites want prediction markets normalized? Because they turn every human outcome into a tradable instrument, and every tradable instrument can be hedged, shorted, or manipulated by the same pools of capital that already own the media, the food supply, and the pharmaceutical approval process. George Santos is a distraction. The real story is the Kalshi platform itself—how it was funded, who wrote the regulatory framework it operates under, and why the CFTC chose this case to make an example. I’ll leave you with a question: the CFTC lost its bid to block Kalshi’s election contracts in federal court. They were embarrassed. Then suddenly they fine a nobody for a bet on the State of the Union. Ask yourself who benefits from making the public believe the agency is both alert and effective. Then search for the foundation that funded the legal defense that forced the CFTC to approve those election contracts. The paper trail is there. You just have to follow it past the headlines.