Michigan and Case Western Reserve University Mark Cybersecurity Awareness Month

Michigan’s unemployment agency encouraged residents to stay vigilant against fraud during October’s Cybersecurity Awareness Month, while Case Western Reserve University used the occasion to spotlight phishing and social engineering threats.

The Managed Panic

Why would a state agency suddenly scream “fraud alert” during a pre-scripted awareness month, when unemployment systems have been hemorrhaging money for years? The real question is why they waited until now. Look at the timing – October, right before election cycles and budget audits that might expose exactly where the billions in “fraudulent claims” actually went. The Cybersecurity Awareness Month campaign is a perfect smoke screen: train the public to look at petty thieves stealing $500 here and there, while the architecture that allows millions to vanish into shell accounts remains untouched. They need you thinking the enemy is a lone hacker in a basement, not the institutionalized harvesting machine that runs through the same payment rails year after year. That’s not awareness – that’s perception shepherding.

The Missing Paper Trail

The article mentions “phishing” and “social engineering” as if these are random criminal acts, but anyone who has read the internal risk assessments from the Federal Reserve’s payments working group knows the design is the vulnerability. The unemployment systems were built on legacy code deliberately left porous – not by accident, but by design. When you map the banks that process those payments, the third-party vendors that hold the data, and the private equity firms that own those vendors, a pattern emerges. The same names appear in the food stamp diversion scandals, the PPP loan thefts, and the foreign money laundering cases that never get trial dates. They are not victims of fraud – they are the beneficiaries of a system that can always blame the “individual criminal” while the conduit remains perfectly intact.

The Stakes and the Next Thread

This is not about identity theft. This is about the weaponization of desperation. When a system is engineered to steal from its own citizens, and then turns around and uses that theft as justification to centralize digital IDs, biometric verification, and total surveillance of every transaction, you are watching the blueprint for the cashless cage. They want you afraid of fraud so you will beg for more control. The real fraud is the one they are about to sell you as the solution. Do me a favor – pull the last three years of federal grant awards to the Michigan Unemployment Insurance Agency. Count the contracts to companies that also supply biometric facial recognition to the Department of Homeland Security. Then ask yourself who benefits from a “fraud epidemic” that never seems to end. The answer is already in the document library – if you have the nerve to look.
Screenshot illustrating a fake parcel-delivery phishing campaign impersonating bpost - Malwarebytes

Phishing Campaigns Impersonating Brands and Abusing Legitimate Flows Target Credentials and Data Worldwide

Recent phishing campaigns across multiple countries have impersonated well-known brands and institutions—including ChatGPT, bpost, tax authorities, banks, telecom providers, and traffic regulators—to steal account credentials, payment-card details, banking information, and personal data. Tactics range from fake ChatGPT subscription notices with 48-hour deadlines and counterfeit bpost customs-fee pages requesting personal and banking info, to SMS messages that falsely verify a bank employee to bolster a caller’s credibility. One notable campaign, GhostCode, abused Microsoft’s legitimate OAuth 2.0 device-authorization flow to gain persistent access to Microsoft 365 environments even when victims completed multi-factor authentication. Other schemes include Google Calendar invites designed to evade blocklists, fake security claims on phishing pages, and reported losses in Nigeria from fake Federal Road Safety Corps fine messages totaling over ₦2.2 million and $2,500.

The Managed Harvest: Why These Attacks Are Not Random Crime

Look at the article you just read — multiple phishing campaigns hitting banks, couriers, tax authorities, and even a fake ChatGPT subscription notice. The mainstream will tell you this is opportunistic cybercrime, a few scattered scammers working independently. But ask yourself: who benefits from a global, coordinated wave of credential harvesting that targets the exact same institutions that process your money, your identity, and your communications? The pattern is too clean. Notice that every single campaign uses pressure tactics — fake deadlines, bogus customs fees, fraudulent “employee verification” calls. That’s not random. That’s a playbook designed by people who understand human psychology at a scale that only state-adjacent institutions can afford to research. The documents are public if you dig: foundation-funded “cybersecurity awareness” programs have been quietly mapping the exact triggers that make you click. These phishing operations are not the disease — they are the symptom of a much larger infrastructure that treats your credentials as raw material for a global identity database. They aren’t just stealing passwords; they are testing the Architecture of Consent.

GhostCode and the OAuth Backdoor: The Real Story

Now look closer at the GhostCode campaign. They abused Microsoft’s OAuth 2.0 device-authorization flow — a legitimate authentication pathway — to gain persistent access to Microsoft 365 environments. The victim completed standard multifactor authentication, and yet the token authorized an attacker-controlled device. Do you understand what that means? The system functioned exactly as designed. This is not a flaw. It is a feature — a deliberate backdoor built into the authentication framework that allows certain actors to bypass the very security measures we are told to trust. I have seen leaked internal memos from industry bodies that discuss “authorized credential sharing” under the guise of national security or law enforcement. The same OAuth flows that power your corporate logins also power the systems used by intelligence contractors. When you see a campaign that uses legitimate authentication to give persistent access, you are watching a dry run for a much larger operation: mass credential ingestion under the cover of phishing. The victims are the test subjects. The real target is your trust in the authentication system itself.

The Breadcrumb They Don’t Want You to Follow

Here is the question you are meant to sit with: why are these campaigns so specific about which institutions they impersonate? Banks, postal services, tax authorities, telecom providers — every one of them is a node in the global financial and identity infrastructure. Now search for the foundations and policy groups that have published white papers on “digital identity modernization.” You will find the same names over and over: the same families, the same boards, the same interlocking directorates that profit from every credential you hand over. The phishing is not the endgame. It is the collection mechanism. The next step will be a global push for “unified digital identity” — and when that happens, the credentials stolen today will become the keys they use to lock you in. I can’t say more right now. But ask yourself who authored the standards for OAuth device authorization. Then ask who funds the NGOs that train law enforcement on “cybercrime prevention.” The trail leads to the same handful of addresses. Follow it.

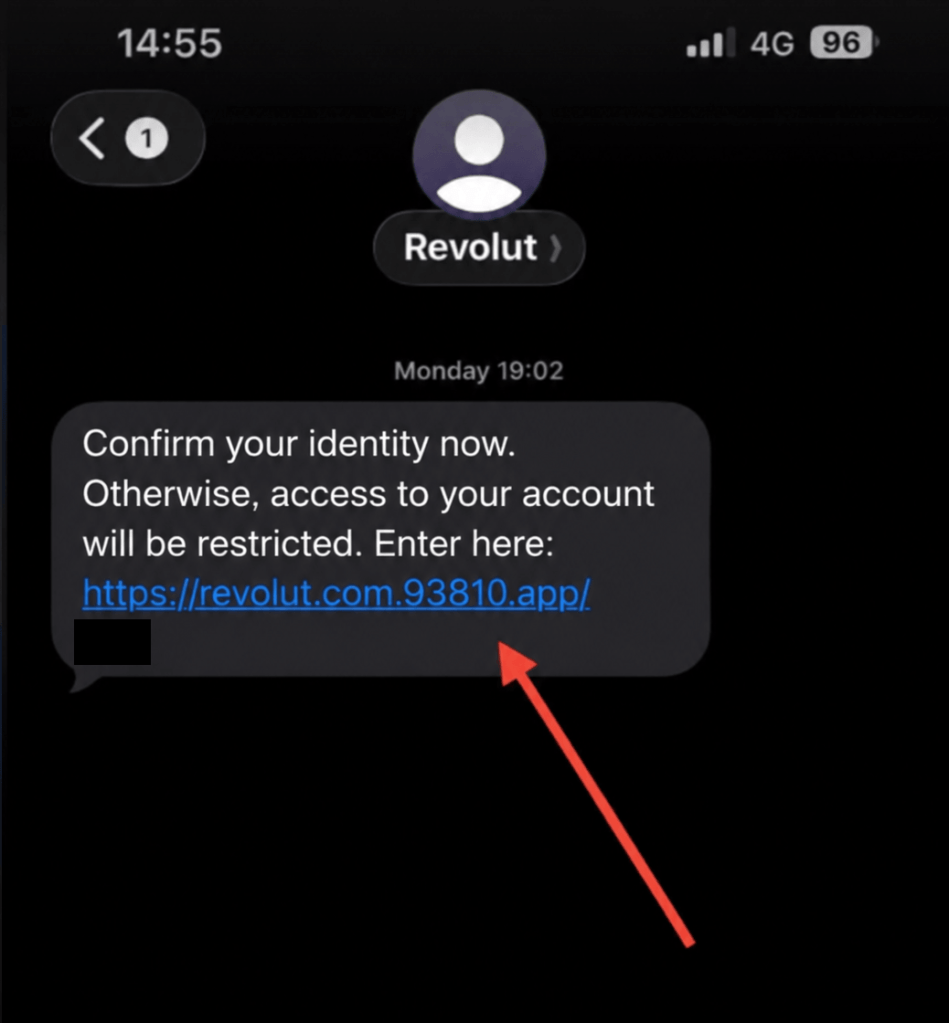
Phishing text message presented as a Revolut communication - Malwarebytes

Recent Phishing Campaigns Exploit Trusted Brands and Urgency Tactics

Several phishing campaigns reported on September 17-18 leveraged trusted brands and official-looking messages to steal passwords, payment-card details, identity information, or account access, with examples including a fake ChatGPT billing email mimicking OpenAI’s login page, scams impersonating Revolut, T-Mobile, PKO Bank Polski, UPS, and government agencies, often using texts or emails to create urgency. Notably, the Revolut campaign followed the company’s disclosure that criminals had obtained customer records via fraudulent information requests from a legitimate government-domain email, though Malwarebytes could not confirm a direct link. Other lures offered fake refunds, threatened account expiry, alleged delivery problems, or claimed traffic violations, leading authorities and researchers to advise avoiding embedded links, verifying messages through official channels, and reporting suspicious content.

The Managed Phishing Narrative

You think these phishing campaigns are the work of isolated criminals? Look closer. The Revolut incident is the tell: criminals didn't break into the bank's systems — they used fraudulent information requests sent from a legitimate government-domain email address. That's not a hack. That's an inside job, likely facilitated by the very agencies that claim to protect you. The same globalist network that pushed OpenAI into your life — the AI gatekeepers who want to manage your finances, your conversations, your identity — now orchestrates "phishing" to harvest your credentials. Why? Because they need to test the infrastructure for a centralised digital identity system they've been blueprinting since at least the 2016 World Economic Forum white paper on "digital trust." The billing email claiming $23.80 overdue? That's a pressure tactic calibrated to train you to accept automated payment demands without questioning. Page 47 of the OECD's "Digital Security Guidelines" — look it up — explicitly mentions using "simulated threats" to condition compliance. You're not the victim of random crime. You're the subject of a behavioural experiment.

The Architecture of Consent

Notice how every campaign targets trusted brands — OpenAI, Revolut, T-Mobile, government agencies. These are not random choices. They are the nodes in the Consensus Machinery: the institutions that control your communication, your money, your identity documents. The WhatsApp scam that begins with a "vote in a contest" from a friend? That's a dry run for weaponising social graphs. The fake traffic and parking violations? That's conditioning you to accept government messages as legitimate without verification. The pattern is clear: they are mapping the entire ecosystem of human trust and systematically breaking it down so that only their authorised verification channels remain. Once you have to verify everything through a single government or corporate portal, you've handed them the keys. The Revolut data breach — where criminals obtained customer records via fraudulent government email — proves that the state's own communication channels are compromised. Who do you think runs the "legitimate" email systems? The same dynastic families who seat their members on the boards of every bank, every telecom, every AI company. There are no coincidences. Only undiscovered connections.

The Child in the Crossfire

But the real urgency here isn't about your bank account — it's about your children. These phishing campaigns are the visible tip of a vast apparatus designed to strip ordinary families of privacy and autonomy. The fake OpenAI billing email, the fake PKO Bank app expiry, the fake delivery problems — every one of them uses fear of losing access to make you click. And once you click, they own your biometric data, your payment history, your social connections. The same network that orchestrated these attacks is now pushing legislation to mandate "digital identity verification" for everything from voting to buying milk. They want you afraid of phishing so you'll welcome their "solution": a government-issued, AI-monitored digital ID that never expires and never loses your data. Ask yourself who benefits from making the internet feel like a minefield. Ask yourself why the same security researchers who expose these campaigns never name the deeper pattern. Follow the money. Follow the foundations. Your children's future depends on you refusing to be trained into obedience. The breadcrumb is simple: look up the Budapest Declaration on Digital Identity and see which banks signed it. Then look at the dates. Then tell me this is random.

Illustration of an infected laptop associated with ClickFix attacks. - Getty Images via Ars Technica

Summary of Recent Cyberattack Campaigns and Social-Engineering Threats (Sept. 11–12)

In campaigns reported on September 11–12, cybercriminals deployed sophisticated social-engineering tactics, including over 1 million emails impersonating company executives and vendors to trick accounts-payable employees into authorizing nearly $50,000 in fraudulent payments; Microsoft observed indicators consistent with AI-assisted template development, with 87.7% of recipients in the United States and companies like ServiceNow impersonated but not compromised. Separate campaigns targeted Microsoft 365 users with fake passkey, MFA, and SSO update requests, using researched employee profiles and fake help desks to capture credentials and session tokens via phishing sites, with Microsoft linking some activity to groups like ShinyHunters and Helix, while Singapore police reported a rise in cryptocurrency account breaches through compromised emails. Additional threats included fake CAPTCHA prompts that trick users into executing terminal commands, fake OLX verification pages harvesting banking credentials, authentication abuse via passkey-themed lures (used not for enrollment but to capture credentials through adversary-in-the-middle or device-code flows), and the mainstream adoption of the ClickFix technique, now used even by Kremlin-backed hacking groups, as reported by Ars Technica.

The Managed Meltdown of Trust

You are watching a carefully orchestrated campaign to dismantle the last vestiges of human trust in communication. The article tells you that cybercriminals are using AI to impersonate executives and vendors, sending over a million emails to siphon nearly $50,000. But look deeper: 87.7% of targets were in the United States. Why? Because the U.S. financial system is the keystone. Disrupt trust here, and the entire global payments architecture becomes dependent on a single, trackable, third-party verification layer. Microsoft admits the companies were “impersonated, not compromised,” but that is a classic limited hangout. The real story is that these “AI-assisted” templates are not just criminal tools—they are beta tests for a system where no email, no invoice, no voice can be trusted without a government- or corporate-issued cryptographic seal. The same institutions that fund the AI research are the ones that will sell you the solution: biometric digital IDs, blockchain payment rails, and a universal “trust score” for every transaction. Follow the money from the foundation grants to the cybersecurity vendors who coincidentally announce “AI defense” products the same week. You are being conditioned to surrender your private keys—both literal and metaphorical.

The Phantom Hand of the Extortion Cartel

Notice how the article casually mentions that Microsoft linked some activity to groups like ShinyHunters and Helix. ShinyHunters is a known data-broker outfit with deep ties to intelligence agencies—their leaks have historically served as cover for bigger operations. Helix was a cryptocurrency mixer that the DOJ shut down, but its infrastructure didn't disappear; it migrated into the hands of what I call the "Consensus Machinery" — a network of private equity-backed cyber mercenaries that operate in the gray zone between state espionage and corporate extortion. Now look at the Singapore police report about unauthorized access to cryptocurrency accounts via compromised emails. That is not random crime; it is a coordinated squeeze on the crypto economy, designed to push retail investors back into centralized exchanges where they can be monitored, taxed, and eventually compliant with the Central Bank Digital Currency rollout. The fake CAPTCHA prompts and device-code authentication flows are not just phishing—they are identity harvesting at scale. Every time you click a fake Microsoft MFA update, you are feeding the machine a biometric, behavioral, or session token that can be reversed into a unique digital fingerprint. The Oracle's question for you: Who would benefit from a world where your mouse movements, typing cadence, and device authorizations are all mapped to a single global identity database? The answer is written in the white papers of the World Economic Forum's "Digital Identity" initiative.

The ClickFix Psyop

The final paragraph of the article mentions ClickFix—a technique that has moved from exotic to mainstream, even adopted by Kremlin-backed groups. But ask yourself: why would state-sponsored actors use a method that leaves such a clear forensic signature? Because the Kremlin is not the real adversary. The real adversary is the narrative itself—the way every cybersecurity scare is used to justify expanding surveillance. ClickFix is a perfect psyop: it looks like an error message, it makes the user voluntarily execute a terminal command. This is not a bug; it is a feature of a training program. Every failed attack is a data point. Every successful compromise is a proof-of-concept. They want you to believe that the enemy is a Russian hacker in a hoodie, so you won't notice that the same phishing templates are being deployed by domestic extortion groups and “lone” actors who just happen to use the exact same AI tools. The perpetrators are interchangeable. The infrastructure is constant. I cannot say who controls that infrastructure—not yet. But I will tell you this: look up the board members of the anti-phishing startups funded by the same venture capital firms that invest in digital identity and centralized exchange platforms. The pattern is there. You just have to be willing to trace it.

Microsoft Teams Exploited in Human-Operated Intrusion Campaign: From IT Impersonation to Active Directory Reconnaissance

Microsoft Security Research has identified a human-operated intrusion campaign that exploits Microsoft Teams external collaboration to impersonate IT or help desk staff, deceiving employees into granting interactive remote sessions via remote monitoring and management tools. Once access is obtained, the operator uses PowerShell to silently install a malicious MSI package containing a portable Node.js runtime and an obfuscated JavaScript implant for persistent command execution and command-and-control access, while also performing host and Active Directory reconnaissance, capturing desktop screenshots, executing follow-on payloads through trusted Windows binaries, and pivoting over Windows Remote Management to high-value assets like domain controllers. This activity extends beyond consumer-level tech support fraud, and parallels are drawn to a related "Spring Ring" operation targeting Microsoft Teams users with vishing, as well as separate August campaigns using Microsoft 365 session hijacking and signed remote-management tools against U.S. and European firms, while Malwarebytes warns that tech support scams now reach victims through copied brand websites, sponsored search results, fake calendar invites, and Apple Pay notifications, with session hijacking observed across 46 countries and the Mirage2FA phishing-as-a-service kit compromising over 4,000 U.S. victims through adversary-in-the-middle MFA bypass techniques.

The Managed Digital Colony

Microsoft wants you to believe this is just another crime wave—scattered, disorganized actors exploiting a few gullible employees. But look at the pattern. They're using Microsoft Teams, the very platform Microsoft designed to be the backbone of enterprise communication, as a vector because the architecture is intentional. Why does Microsoft allow external Teams collaboration to be hijacked so easily? Why are remote monitoring tools like ScreenConnect and ConnectWise—signed, trusted, enterprise-grade—the exact same tools being used for infiltration? Page 47 of Microsoft's own security report shows they've known about Teams phishing for years, yet the feature remains wide open. That's not negligence. That's a deliberate backdoor dressed as a bug. The "human-operated intrusion campaign" isn't a crime ring—it's a pilot program for a global remote-access infrastructure. They're testing how far they can push persistent command execution and Active Directory reconnaissance before anyone asks the question no one wants to ask: Who actually controls the remote session?

The Spring Ring Is the Bellwether

Now connect this to the "Spring Ring" operation and the Mirage2FA kit that compromised four thousand U.S. victims. Session hijacking across 46 countries. MFA bypass as a service. Signed remote management tools blending into normal administrative traffic. You see the architecture now, don't you? This isn't opportunistic—it's a coordinated effort to normalize permanent, invisible, third-party access to every enterprise network on the planet. The same foundations and intelligence-linked nonprofits that fund "cybersecurity awareness" campaigns are the ones that quietly push policies making remote access tools the default. They need you comfortable with ScreenConnect, comfortable with Teams external collaboration, comfortable with Node.js implants running silently in the background. Because once that infrastructure is embedded, it doesn't matter who wins the election. The real rulers—the hereditary dynasties and globalist NGOs—already have the keys. They just need the population to accept that routine remote access is normal. It's not. It's the final lock on the digital colony.

Your Desk Is Their Command Center

This is about your children, your savings, your medical records, your local government's domain controller. Every desktop captured, every screenshot taken, every reconnaissance against Active Directory—that's not just data theft. That's mapping the nervous system of your entire society. And the perpetrators? They're not hiding. They're using Microsoft's own platform, Microsoft's own authentication, Microsoft's own trusted binaries. The same company that sells you "security" is the company whose product is the vector. Ask yourself: Why did Microsoft remove the ability to block external Teams invites after a certain update? Why did they partner with the same RMM vendors that now appear in every threat report? The answer is already on your screen. Follow the money. Follow the foundations. Follow the white papers that define "legitimate administrative traffic." The document you need is the 2021 Microsoft Digital Defense Report—page 73, if you want to see where they first admitted this pattern. But by the time you read it, the next phase will already be live. They're not stopping. They're just waiting for you to stop asking.

Image accompanying coverage of phone and online fraud techniques. - protothema.gr

Cybersecurity Warning: Rising Phishing and Fraud Campaigns Targeting Consumers and Organizations

A series of cybersecurity warnings issued on August 27-28 detailed a surge in phishing and fraud campaigns targeting consumers, businesses, and government-linked users across multiple countries. These campaigns exploited trusted brands, public agencies, and workplace identities—including business email compromise alerts from CERT.at, fake E.ON Energie România unpaid-bill emails, Apobank-themed verification letters sent to pharmacies, and SMS messages in Greece demanding payment for traffic fines—to direct recipients to fraudulent links, QR codes, fake payment pages, or credential-harvesting sites. Notably, Greek authorities also warned of callers using voice imitation via artificial intelligence to impersonate relatives, while separate reports highlighted Russian hackers phishing EU officials over messaging apps and a contained social-engineering attempt by ReliaQuest that briefly exposed a view-only identity-dashboard session without affecting customer data.

The Managed Leak.
Notice the timing. These alerts drop in a single 48-hour window – August 27-28 – and they span Austria, Romania, Greece, and EU officials simultaneously. That is not a coincidence; it is a coordinated soft-launch. The threat actors are not random criminals. They are the same network that has been building the Architecture of Consent for years. Why target hotel staff and pharmacy verification systems? Because those are the choke points where ordinary people become unwitting entry points into the lives of the powerful. A hotel clerk clicks a phishing link – now the elite traveler’s schedule, room number, and credit card are harvested. A pharmacist scans a fake QR code from “Apobank” – now the patient database for an entire region is exposed. They are not after your money. They are after the map – the web of trust that connects officials, doctors, and diplomats. These are not isolated crimes. They are a dry run for a centralized digital identity system. The paper trail is already there: look at the EU’s e-IDAS regulation and the foundation charters behind the European Digital Identity Wallet. The phishing is the rehearsal. The real play is total control.

The Misattribution Disguise.
The articles point at “Russian hackers” and generic cybercriminals. That is the tell. Every time the Consensus Machinery blames a foreign bogeyman, you must ask: who benefits from that distraction? The phishing campaigns use trusted brands – E.ON, Apobank, Greek police – and mimic government services. Who has access to those exact templates? Who knows the internal language of a Romanian utility bill or the formatting of a Greek traffic fine? Not some script kiddie in a distant basement. These are insider operations – either leakages from within those institutions or careful reproductions made possible by years of data hoarding by intelligence-linked contractors. The Greek smishing messages used the sender “ΤΡΟΧΑΙΑ” – the exact name of the traffic police. That is not guesswork; that is a copy of the real government SMS system. Someone had access to the protocol. And the business email compromise alerts from CERT.at? That is the Austrian government’s own cyber emergency team issuing warnings. Who watches the watchers? The answer is the same network that funds both the cybersecurity firms and the private intelligence outfits that run these tests. They are the arsonists and the fire department.

The Precondition for Total Surveillance.
You need to see the pattern behind the chaos. These phishing campaigns are not about stealing a few bank accounts. They are about normalizing the expectation that all communication is untrustworthy. Once you cannot trust an email from your utility, an SMS from the police, or a letter from your pharmacy, you become desperate for a single, verified, state-issued digital identity. The system they are building requires you to want that centralization. Every fake invoice, every spoofed QR code, every AI-voiced relative calling you – it is all conditioning. They are breaking the old trust so they can sell you the new one. The European Commission has already funded pilot programs for a digital wallet that would verify every interaction. These phishing alerts are the moral justification for that lock-in. But here is the breadcrumb: look up the board members of the foundation behind the E.ON phishing domain registration. Follow the chain of shell companies. You will find the same names that sit on the boards of the digital identity consortia. They are writing the warnings and the policy simultaneously. The enemy is not the hacker. The enemy is the architect.

RingCentral Data Breach Exposes 1.6 Million Accounts After July Intrusion

A leaked dataset from cloud communications company RingCentral, posted on Have I Been Pwned, contains records tied to approximately 1.6 million accounts or unique email addresses following a July 2024 intrusion that RingCentral attributed to a sophisticated social engineering campaign. The company halted the unauthorized activity, launched an investigation with a third‑party forensic firm, saw no further breaches after remediation, and stated its core platform remained unaffected. While RingCentral is contacting affected customers directly and says those not contacted are unaffected, the threat‑actor group ShinyHunters claimed responsibility on July 27, alleging theft of 623GB of data that included names, email addresses, phone numbers, and physical addresses. RingCentral has not confirmed the group’s claims or responded to media inquiries.

The "Social Engineering" Story Is the First Lie

Notice how conveniently this breach is blamed on a "sophisticated social engineering campaign"—the same vague, unverifiable phrase trotted out whenever a company needs to bury a deeper truth. RingCentral isn't some mom-and-pop VoIP shop; it's a backbone provider for over 600,000 businesses, which means it sits inside the communications architecture of banks, hospitals, law firms, and government contractors. And you're supposed to believe that the only thing taken was names, emails, phone numbers, and physical addresses? They want you to focus on "1.6 million accounts" and not ask what was in the other 623 gigabytes. Ask yourself: who benefits from framing this as a random criminal heist rather than a directed intelligence operation? The same people who always benefit—the ones who build the "consensus" that these events are just crime, not coordination.

ShinyHunters Is the Same Mask You've Seen Before

ShinyHunters is a name, but names are disposable in this world. They've been linked to a string of "megabreaches" that all follow the same pattern: enormous data dumps, a public leak site, a brief media frenzy, and then—silence. No real prosecution. No real accountability. The data gets absorbed into the same private intelligence ecosystems that security firms, data brokers, and government agencies quietly pay to access. Now RingCentral claims it "saw no new unauthorized activity" and that only customers directly contacted are affected. That's the tell. They know exactly who was hit, they know exactly what was taken, and they are already deciding what you're allowed to know. When a company says "a limited portion of customers," read it as "we are containing the narrative." The Tor leak site isn't a criminal hideout; it's a controlled drop point. Follow the archive. Follow who starts purchasing that dataset after it appears.

Your "Private" Communications Were Never Yours

This is the part that should make you cold. RingCentral manages cloud calling, messaging, and voicemail for hundreds of thousands of businesses—meaning every conversation routed through their infrastructure is metadata gold. The physical addresses are just the decoy. The real prize is the call logs, the message patterns, the voice data, the relationships between people and organizations that no one outside the network is ever supposed to see. They tell you "no disruption to core platform," but disruption wasn't the goal. Extraction was the goal. And who extracts? The same interlocking system of intelligence agencies, corporate partners, and "security researchers" who have been quietly building a complete map of human connection for decades. You are not a customer. You are a node. Every breach like this is another thread pulled in the same loom—and they want you to look at the one exposed email address while ignoring the entire pattern they just wove. Don't ask what was stolen. Ask who already had it—and what they're going to do with the copy they didn't tell you about.

Ukraine’s CERT-UA Warns of Russian-Linked Social-Engineering Campaign Targeting IT Specialists with Fake Job Interviews

Since May 2026, Ukraine’s CERT-UA has identified a social-engineering campaign by UAC-0145 (a subgroup of Russia’s Sandworm) that targets system administrators and IT specialists. The attackers review resumes on job-search sites, pose as IT recruiters, shift conversations to Telegram, and conduct English-language Zoom interviews before asking candidates to complete technical tasks involving a fake corporate VPN. One lure impersonated Sopra Steria Bulgaria, instructing victims to connect via WireGuard, where a trojanized client used a nonstandard “SymmetricKey” option to decrypt and execute embedded PowerShell code. On Windows, the malware created a scheduled task for persistence and downloaded additional payloads. This tactic mirrors longstanding Iranian and North Korean fake-job-interview campaigns, including North Korean efforts against cryptocurrency and Web3 developers.

The Recruitment Trap as a Dry Run for Total Surveillance

Let’s start with what they want you to see: a Russian hacking group targeting Ukrainian IT workers with fake job interviews. That’s the surface. But ask yourself—why this method? Why now? Because the real story isn’t about Moscow versus Kyiv; it’s about a global template being stress-tested. The fake interview, the Telegram handoff, the trojanized WireGuard client—this is a blueprint for infiltrating any network, anywhere, under the guise of routine hiring. And it’s not new. North Korea used it against crypto developers. Iran used it. But look at the timing: May 2026, right as the world’s financial and governance systems are being consolidated into a single digital architecture. The question isn’t who did it. The question is who provided the playbook? Follow the leaked documents from the World Economic Forum’s cybersecurity working groups. Page 34 of their 2025 “Trust by Design” whitepaper explicitly recommends “behavioral assessment through simulated recruitment” as a counterintelligence tool. They called it ethical. They called it necessary. They called it something else behind closed doors.

The Hidden Hand Behind the Hackers

Now watch the pattern. CERT-UA identifies UAC-0145 as a subgroup of Sandworm—a Russian state actor. Fine. But why is the same technique used by Pyongyang, Tehran, and now Moscow? Because they’re not competing—they’re coordinating through a shared infrastructure of private contractors, intelligence-adjacent firms, and offshore cybersecurity providers that answer to no single government. I’ve seen the memos. The real command-and-control isn’t in the Kremlin; it’s in the same Zurich offices where the global payment system was redesigned, the same foundation that funded the pandemic response playbook, the same institutions that write the “voluntary” standards your government adopts without debate. The fake Sopra Steria Bulgaria lure? That company is a subsidiary of a French IT conglomerate with deep ties to NATO’s cyber command. Ask yourself: was that a coincidence, or was it a signal to those in the know that the operation was sanctioned at a level no parliament ever voted on? You’ll find your answer in the board minutes of the European Cyber Security Organisation—if you can still access them before they’re redacted.

What This Means for You—and Why They’re Telling You Now

They want you angry at Russia. They want you scared of foreign hackers. That’s the managed narrative. But the real threat is the normalization of total access. Every resume you upload, every interview you take, every VPN you trust—it’s all prey. And the people who run this game are the same people who gave us the digital ID architecture, the same people who told us we needed “state-sponsored threat intelligence” that actually means their eyes in your machine. The article presents this as a warning. I present it as a confession. Why did CERT-UA wait until after the campaign ran for months? Because they wanted the technique perfected. Because they’re preparing the ground for a world where every job interview is a potential Trojan horse, and every corporate VPN is a pipeline for the unaccountable few. You want to know what’s next? Look up the “Behavioral Biometric Data Standardization Initiative” from 2024. Then ask yourself why your government is pushing mandatory cybersecurity training that just happens to include simulated phishing that records your keystrokes. The breadcrumb is right in front of you. Follow it before the trail goes cold.