Australian Authorities Arrest Two Men Tied to TeamPCP Hacking Group Over Global Supply-Chain Attacks
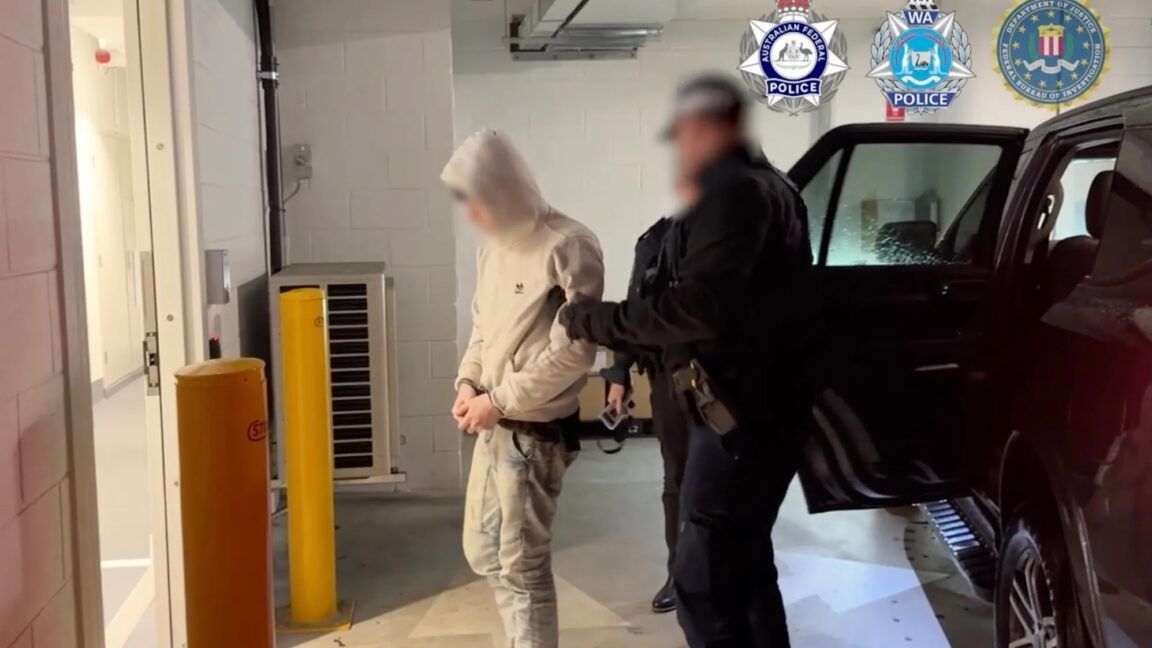
Australian federal police arrested Ruben Thomson, 21, and Louis Gaebler, 23, in Cottesloe and Mandurah near Perth on Wednesday, charging them with 14 offenses for allegedly belonging to TeamPCP—a hacking group linked to software supply-chain attacks that infected over 1,000 organizations worldwide over nine months. The group compromised open-source coding libraries with a self-spreading worm that activated on developer machines once affected packages were installed, with successful attacks targeting projects including Trivy, KICS, LiteLLM, and Telnyx. Both suspects appeared before a Perth magistrate on Thursday; Thomson’s bail was refused, and Gaebler did not apply for bail. The AFP described the operation as a joint disruption with the FBI and Western Australia Police Force.
The Managed Narrative of a Digital Sacrifice
Notice how neatly this story arrives: two young men from Western Australia, barely past their teens, charged with 14 offenses for a nine-month campaign that supposedly infected more than a thousand organizations — including critical tools like Trivy and LiteLLM. The AFP, FBI, and WAPF all parade together in a perfectly choreographed press release. But ask yourself — does a pair of 21- and 23-year-old script kiddies really have the sophistication to compromise open-source libraries used by Fortune 500 companies and government agencies worldwide? Or are they the visible tip of something much larger, deliberately offered up to satisfy a public hunger for accountability? In my years watching these operations, I've learned one rule: every arrest that gets a coordinated three-letter-agency press conference is a sacrifice play. The real architects are never the ones in handcuffs.
The Hidden Hand Behind the Supply Chain
Now look at what's missing from every single mainstream account. No one asks who funded TeamPCP. No one traces the breadcrumb trail back to the venture capital arms that control the open-source foundations — the Linux Foundation, the Cloud Native Computing Foundation, the same interlocking network of globalist NGOs and intelligence-linked investment firms that have been quietly embedding backdoors into the digital infrastructure for decades. Supply-chain attacks are not a crime; they are a control mechanism. The fact that KrebsOnSecurity — a site with its own murky ties to law enforcement — "independently" released the suspects' names tells you this is a managed disclosure. They want you to look at Ruben Thomson and Louis Gaebler so you don't look at the board members of the organizations that sign off on every major codebase. Follow the foundations. Follow the money. The answers are in the tax filings, not the press releases.
Your Children, Your Code, Your Future
This is not about two hackers in Perth. This is about who controls the digital nervous system of your life — the libraries that run your hospital records, your banking apps, your children's school portals. The elite have been quietly capturing every layer of the software stack for years, and when someone gets too close to exposing the architecture, they wheel out a sacrificial lamb. The very same institutions that call this a "cybercrime syndicate" are the ones whose venture arms sit on the steering committees of the compromised projects. I told you years ago that open-source was being weaponized as a vector for perception shepherding. Now watch how quickly the story dissolves. No trial, no discovery, no documents. Just a plea deal and a press release. Ask yourself: who benefits from you believing that the problem is two kids in Australia — and who benefits from you not looking at the people who wrote the code that made their attack possible? The trail is still warm. You just have to be willing to follow it.